# No me funciona Rkill (parte 1)
**URL:** https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936
**Category:** Eliminar Malwares
**Created:** [19 Enero, 2022 12:04 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936 "2022-01-19T12:04:18Z")
**Posts on this page:** 20
**Page:** 6
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [29 Enero, 2022 01:27 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/127 "2022-01-29T01:27:02Z")
System log
```auto
Malwarebytes Anti-Rootkit BETA 1.10.3.1001
(c) Malwarebytes Corporation 2011-2012
OS version: 10.0.9200 Windows 10 x64
System is currently in a safe mode
Account is Administrative
Internet Explorer version: 11.789.19041.0
File system is: NTFS
Disk drives: C:\ DRIVE_FIXED, D:\ DRIVE_FIXED
CPU speed: 1.600000 GHz
Memory total: 4145299456, free: 958873600
Downloaded database version: v2022.01.28.07
Downloaded database version: v2022.01.28.07
Downloaded database version: v2018.01.20.01
Initializing...
=======================================
Driver version: 4.3.0.15
------------ Kernel report ------------
01/28/2022 11:52:06
------------ Loaded modules -----------
\SystemRoot\system32\ntoskrnl.exe
\SystemRoot\system32\hal.dll
\SystemRoot\system32\kd.dll
\SystemRoot\system32\mcupdate_GenuineIntel.dll
\SystemRoot\System32\drivers\CLFS.SYS
\SystemRoot\System32\drivers\tm.sys
\SystemRoot\system32\PSHED.dll
\SystemRoot\system32\BOOTVID.dll
\SystemRoot\System32\drivers\FLTMGR.SYS
\SystemRoot\System32\drivers\msrpc.sys
\SystemRoot\System32\drivers\ksecdd.sys
\SystemRoot\System32\drivers\clipsp.sys
\SystemRoot\System32\drivers\cmimcext.sys
\SystemRoot\System32\drivers\werkernel.sys
\SystemRoot\System32\drivers\ntosext.sys
\SystemRoot\system32\CI.dll
\SystemRoot\System32\drivers\cng.sys
\SystemRoot\system32\drivers\Wdf01000.sys
\SystemRoot\system32\drivers\WDFLDR.SYS
\SystemRoot\system32\drivers\WppRecorder.sys
\SystemRoot\system32\drivers\SleepStudyHelper.sys
\SystemRoot\System32\Drivers\acpiex.sys
\SystemRoot\system32\drivers\SgrmAgent.sys
\SystemRoot\System32\drivers\ACPI.sys
\SystemRoot\System32\drivers\WMILIB.SYS
\SystemRoot\System32\drivers\msisadrv.sys
\SystemRoot\System32\drivers\pci.sys
\SystemRoot\System32\drivers\tpm.sys
\SystemRoot\System32\drivers\intelpep.sys
\SystemRoot\system32\drivers\WindowsTrustedRT.sys
\SystemRoot\System32\drivers\IntelTA.sys
\SystemRoot\System32\drivers\WindowsTrustedRTProxy.sys
\SystemRoot\System32\drivers\pcw.sys
\SystemRoot\System32\drivers\isapnp.sys
\SystemRoot\System32\drivers\vdrvroot.sys
\SystemRoot\System32\Drivers\sptd2.sys
\SystemRoot\system32\drivers\pdc.sys
\SystemRoot\system32\drivers\CEA.sys
\SystemRoot\System32\drivers\partmgr.sys
\SystemRoot\System32\drivers\evbda.sys
\SystemRoot\System32\drivers\pcmcia.sys
\SystemRoot\System32\drivers\pciide.sys
\SystemRoot\System32\drivers\PCIIDEX.SYS
\SystemRoot\System32\drivers\spaceport.sys
\SystemRoot\System32\drivers\intelide.sys
\SystemRoot\System32\drivers\volmgr.sys
\SystemRoot\System32\drivers\sdbus.sys
\SystemRoot\System32\drivers\volmgrx.sys
\SystemRoot\System32\drivers\vmbus.sys
\SystemRoot\System32\drivers\NDIS.SYS
\SystemRoot\System32\drivers\NETIO.SYS
\SystemRoot\System32\drivers\hvsocket.sys
\SystemRoot\System32\drivers\vmbkmcl.sys
\SystemRoot\System32\drivers\winhv.sys
\SystemRoot\System32\drivers\vpci.sys
\SystemRoot\System32\drivers\bxvbda.sys
\SystemRoot\System32\drivers\nvraid.sys
\SystemRoot\System32\drivers\CLASSPNP.SYS
\SystemRoot\system32\drivers\urscx01000.sys
\SystemRoot\System32\drivers\mountmgr.sys
\SystemRoot\System32\drivers\iaStorV.sys
\SystemRoot\System32\drivers\vsmraid.sys
\SystemRoot\System32\drivers\storport.sys
\SystemRoot\System32\drivers\3ware.sys
\SystemRoot\System32\drivers\amdsata.sys
\SystemRoot\System32\drivers\amdxata.sys
\SystemRoot\System32\drivers\amdsbs.sys
\SystemRoot\System32\drivers\arcsas.sys
\SystemRoot\System32\drivers\ItSas35i.sys
\SystemRoot\System32\drivers\lsi_sas.sys
\SystemRoot\System32\drivers\lsi_sas2i.sys
\SystemRoot\System32\drivers\lsi_sas3i.sys
\SystemRoot\System32\drivers\lsi_sss.sys
\SystemRoot\System32\drivers\megasas.sys
\SystemRoot\System32\drivers\MegaSas2i.sys
\SystemRoot\System32\drivers\megasas35i.sys
\SystemRoot\System32\drivers\megasr.sys
\SystemRoot\System32\drivers\mvumis.sys
\SystemRoot\System32\drivers\nvstor.sys
\SystemRoot\System32\drivers\percsas2i.sys
\SystemRoot\System32\drivers\percsas3i.sys
\SystemRoot\System32\drivers\SiSRaid2.sys
\SystemRoot\System32\drivers\sisraid4.sys
\SystemRoot\System32\drivers\vstxraid.sys
\SystemRoot\System32\drivers\stexstor.sys
\SystemRoot\System32\drivers\cht4sx64.sys
\SystemRoot\System32\drivers\iaStorAVC.sys
\SystemRoot\System32\drivers\atapi.sys
\SystemRoot\System32\drivers\ataport.SYS
\SystemRoot\System32\drivers\storahci.sys
\SystemRoot\System32\drivers\stornvme.sys
\SystemRoot\System32\drivers\ADP80XX.SYS
\SystemRoot\System32\drivers\HpSAMD.sys
\SystemRoot\System32\drivers\SmartSAMD.sys
\SystemRoot\System32\drivers\nvdimm.sys
\SystemRoot\System32\drivers\EhStorTcgDrv.sys
\SystemRoot\System32\drivers\EhStorClass.sys
\SystemRoot\System32\drivers\fileinfo.sys
\SystemRoot\System32\Drivers\Wof.sys
\SystemRoot\System32\Drivers\Ntfs.sys
\SystemRoot\System32\drivers\usbccgp.sys
\SystemRoot\System32\drivers\USBD.SYS
\SystemRoot\System32\DriverStore\FileRepository\urschipidea.inf_amd64_78ad1c14e33df968\urschipidea.sys
\SystemRoot\System32\drivers\usbehci.sys
\SystemRoot\System32\drivers\USBPORT.SYS
\SystemRoot\System32\drivers\storvsc.sys
\SystemRoot\System32\drivers\usbhub.sys
\SystemRoot\System32\drivers\UsbHub3.sys
\SystemRoot\System32\Drivers\Fs_Rec.sys
\SystemRoot\System32\Drivers\ksecpkg.sys
\SystemRoot\System32\drivers\tcpip.sys
\SystemRoot\System32\drivers\fwpkclnt.sys
\SystemRoot\System32\drivers\wfplwfs.sys
\SystemRoot\System32\drivers\vmstorfl.sys
\SystemRoot\System32\drivers\bttflt.sys
\SystemRoot\System32\DRIVERS\fvevol.sys
\SystemRoot\System32\drivers\volume.sys
\SystemRoot\System32\drivers\volsnap.sys
\SystemRoot\System32\drivers\USBSTOR.SYS
\SystemRoot\System32\drivers\uaspstor.sys
\SystemRoot\System32\drivers\storufs.sys
\SystemRoot\System32\drivers\sdstor.sys
\SystemRoot\System32\drivers\scmbus.sys
\SystemRoot\System32\drivers\sbp2port.sys
\SystemRoot\System32\drivers\rdyboost.sys
\SystemRoot\system32\DRIVERS\ramdisk.sys
\SystemRoot\System32\drivers\pmem.sys
\SystemRoot\System32\Drivers\mup.sys
\SystemRoot\system32\drivers\iorate.sys
\SystemRoot\System32\drivers\disk.sys
\SystemRoot\System32\Drivers\crashdmp.sys
\SystemRoot\System32\Drivers\Null.SYS
\SystemRoot\System32\Drivers\Beep.SYS
\SystemRoot\System32\drivers\dxgkrnl.sys
\SystemRoot\System32\drivers\watchdog.sys
\SystemRoot\System32\DriverStore\FileRepository\basicdisplay.inf_amd64_65ab9a260dbf7467\BasicDisplay.sys
\SystemRoot\System32\DriverStore\FileRepository\basicrender.inf_amd64_df49c4daa6251397\BasicRender.sys
\SystemRoot\System32\Drivers\Npfs.SYS
\SystemRoot\System32\Drivers\Msfs.SYS
\SystemRoot\System32\Drivers\CimFS.SYS
\SystemRoot\system32\DRIVERS\tdx.sys
\SystemRoot\system32\DRIVERS\TDI.SYS
\SystemRoot\System32\DRIVERS\netbt.sys
\SystemRoot\system32\drivers\afunix.sys
\SystemRoot\system32\drivers\afd.sys
\SystemRoot\System32\drivers\vwififlt.sys
\SystemRoot\System32\drivers\pacer.sys
\SystemRoot\System32\drivers\ndiscap.sys
\SystemRoot\system32\drivers\netbios.sys
\SystemRoot\system32\DRIVERS\rdbss.sys
\SystemRoot\system32\drivers\nsiproxy.sys
\SystemRoot\System32\Drivers\dfsc.sys
\SystemRoot\system32\DRIVERS\ahcache.sys
\SystemRoot\System32\DriverStore\FileRepository\compositebus.inf_amd64_7500cffa210c6946\CompositeBus.sys
\SystemRoot\System32\drivers\kdnic.sys
\SystemRoot\System32\DriverStore\FileRepository\umbus.inf_amd64_b78a9c5b6fd62c27\umbus.sys
\SystemRoot\System32\drivers\CAD.sys
\SystemRoot\System32\drivers\cdrom.sys
\SystemRoot\System32\drivers\TXEIx64.sys
\SystemRoot\System32\drivers\HDAudBus.sys
\SystemRoot\System32\drivers\portcls.sys
\SystemRoot\System32\drivers\drmk.sys
\SystemRoot\System32\drivers\ks.sys
\SystemRoot\system32\DRIVERS\bcmwl63a.sys
\SystemRoot\System32\drivers\vwifibus.sys
\SystemRoot\System32\drivers\rt640x64.sys
\SystemRoot\System32\drivers\msgpiowin32.sys
\SystemRoot\System32\drivers\mshidkmdf.sys
\SystemRoot\System32\drivers\HIDCLASS.SYS
\SystemRoot\System32\drivers\HIDPARSE.SYS
\SystemRoot\System32\drivers\i8042prt.sys
\SystemRoot\system32\DRIVERS\ETD.sys
\SystemRoot\System32\drivers\kbdclass.sys
\SystemRoot\System32\drivers\mouclass.sys
\SystemRoot\System32\drivers\ETDSMBus.sys
\SystemRoot\System32\drivers\WirelessButtonDriver64.sys
\SystemRoot\System32\drivers\wmiacpi.sys
\SystemRoot\System32\DriverStore\FileRepository\uefi.inf_amd64_c1628ffa62c8e54c\UEFI.sys
\SystemRoot\System32\drivers\NdisVirtualBus.sys
\SystemRoot\System32\drivers\mssmbios.sys
\SystemRoot\System32\DriverStore\FileRepository\swenum.inf_amd64_16a14542b63c02af\swenum.sys
\SystemRoot\System32\drivers\rdpbus.sys
\SystemRoot\System32\drivers\IntcDAud.sys
\SystemRoot\system32\drivers\ksthunk.sys
\SystemRoot\System32\drivers\kbdhid.sys
\SystemRoot\System32\Drivers\fastfat.SYS
\SystemRoot\System32\Drivers\dump_diskdump.sys
\SystemRoot\System32\drivers\dump_storahci.sys
\SystemRoot\System32\Drivers\dump_dumpfve.sys
\SystemRoot\System32\win32k.sys
\SystemRoot\System32\win32kbase.sys
\SystemRoot\System32\win32kfull.sys
\SystemRoot\System32\drivers\dxgmms2.sys
\SystemRoot\System32\cdd.dll
\SystemRoot\system32\drivers\ndisuio.sys
\SystemRoot\system32\DRIVERS\nwifi.sys
\SystemRoot\system32\drivers\msquic.sys
\SystemRoot\system32\DRIVERS\bowser.sys
\SystemRoot\System32\drivers\mpsdrv.sys
\SystemRoot\system32\DRIVERS\mrxsmb.sys
\SystemRoot\system32\DRIVERS\mrxsmb20.sys
\SystemRoot\System32\drivers\condrv.sys
\SystemRoot\System32\drivers\vwifimp.sys
\??\c:\users\pablo iñiguez araven\appdata\local\temp\A7347D3C-F497715E-CB1A5E20-1E679BF0\144b1ad1e.sys
\??\C:\Users\Pablo Iñiguez Araven\AppData\Local\Temp\1552b601b.sys
\??\C:\Users\Pablo Iñiguez Araven\AppData\Local\Temp\10a0361f00.sys
\SystemRoot\System32\Drivers\mbamswissarmy.sys
\??\C:\WINDOWS\system32\drivers\MbamChameleon.sys
\??\C:\WINDOWS\system32\drivers\25430748.sys
----------- End -----------
Done!
Scan started
Database versions:
main: v2022.01.28.07
rootkit: v2022.01.28.07
<<<2>>>
Physical Sector Size: 512
Drive: 0, DevicePointer: 0xffffc986f86400a0, DeviceName: \Device\Harddisk0\DR0\, DriverName: \Driver\disk\
--------- Disk Stack ------
DevicePointer: 0xffffc986f85ba920, DeviceName: Unknown, DriverName: \Driver\partmgr\
DevicePointer: 0xffffc986f86400a0, DeviceName: \Device\Harddisk0\DR0\, DriverName: \Driver\disk\
DevicePointer: 0xffffc986f8452050, DeviceName: \Device\0000002f\, DriverName: \Driver\storahci\
------------ End ----------
Alternate DeviceName: \Device\Harddisk0\DR0\, DriverName: \Driver\disk\
Upper DeviceData: 0x0, 0x0, 0x0
Lower DeviceData: 0x0, 0x0, 0x0
<<<3>>>
Volume: C:
File system type: NTFS
SectorSize = 512, ClusterSize = 4096, MFTRecordSize = 1024, MFTIndexSize = 4096 bytes
<<<2>>>
<<<3>>>
Volume: C:
File system type: NTFS
SectorSize = 512, ClusterSize = 4096, MFTRecordSize = 1024, MFTIndexSize = 4096 bytes
Scanning drivers directory: C:\WINDOWS\SYSTEM32\drivers...
Done!
Drive 0
This is a System drive
Scanning MBR on drive 0...
Inspecting partition table:
This drive is a GPT Drive.
MBR Signature: 55AA
Disk Signature: 0
GPT Protective MBR Partition information:
Partition 0 type is EFI-GPT (0xee)
Partition is NOT ACTIVE.
Partition starts at LBA: 1 Numsec = 4294967295
Partition 1 type is Empty (0x0)
Partition is NOT ACTIVE.
Partition starts at LBA: 0 Numsec = 0
Partition 2 type is Empty (0x0)
Partition is NOT ACTIVE.
Partition starts at LBA: 0 Numsec = 0
Partition 3 type is Empty (0x0)
Partition is NOT ACTIVE.
Partition starts at LBA: 0 Numsec = 0
GPT Partition information:
GPT Header Signature 4546492050415254
GPT Header Revision 65536 Size 92 CRC 826856347
GPT Header CurrentLba = 1 BackupLba 976773167
GPT Header FirstUsableLba 34 LastUsableLba 976773134
GPT Header Guid 669b7fd5-aba4-4ecc-9a95-c99d504f9310
GPT Header Contains 128 partition entries starting at LBA 2
GPT Header Partition entry size = 128
Backup GPT header Signature 4546492050415254
Backup GPT header Revision 65536 Size 92 CRC 826856347
Backup GPT header CurrentLba = 976773167 BackupLba 1
Backup GPT header FirstUsableLba 34 LastUsableLba 976773134
Backup GPT header Guid 669b7fd5-aba4-4ecc-9a95-c99d504f9310
Backup GPT header Contains 128 partition entries starting at LBA 976773135
Backup GPT header Partition entry size = 128
Partition 0 Type c12a7328-f81f-11d2-ba4b-0a0c93ec93b
Partition ID a09d486f-99b5-4994-b4b6-f97d37b49df
FirstLBA 2048 Last LBA 534527
Attributes 0
Partition Name EFI system partition
GPT Partition 0 is bootable
Partition 1 Type e3c9e316-b5c-4db8-817d-f92df0215ae
Partition ID c0e2d594-15c8-4907-b893-dc0081f672
FirstLBA 534528 Last LBA 567295
Attributes 0
Partition Name Microsoft reserved partition
Partition 2 Type ebd0a0a2-b9e5-4433-87c0-68b6b72699c7
Partition ID 466e3134-4198-4c3d-9461-172fd3c9bb3f
FirstLBA 567296 Last LBA 946187044
Attributes 0
Partition Name Basic data partition
Partition 3 Type de94bba4-6d1-4d40-a16a-bfd5179d6ac
Partition ID 4e85bcea-2284-4f4a-8275-c8fd59515dd4
FirstLBA 946188288 Last LBA 948117503
Attributes 1
Partition Name
Partition 4 Type ebd0a0a2-b9e5-4433-87c0-68b6b72699c7
Partition ID 9f808ce3-1a8e-4beb-bf18-6a57d41c614c
FirstLBA 949561344 Last LBA 976762879
Attributes 1
Partition Name Basic data partition
Disk Size: 500107862016 bytes
Sector size: 512 bytes
Done!
Scan finished
=======================================
Removal queue found; removal started
Removing C:\ProgramData\Malwarebytes' Anti-Malware (portable)\MBR-0-i.mbam...
Removing C:\ProgramData\Malwarebytes' Anti-Malware (portable)\MBR-0-r.mbam...
Removal finished
```
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [29 Enero, 2022 01:36 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/128 "2022-01-29T01:36:09Z")
Perfecto! El programa ha realizado correctamente su función! Ahora quiero asegurarme de una cosa más. 😃
Te pongo los pasos a seguir.
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [29 Enero, 2022 01:37 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/129 "2022-01-29T01:37:03Z")
Ok. No me pidió reiniciar así es que sigo en modo seguro con red
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [29 Enero, 2022 01:39 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/131 "2022-01-29T01:39:31Z")
**IMPORTANTE:**
Realice todo este procedimiento en **Modo Seguro con Funciones de Red:**
En primer lugar, pásele el programa: [Rkill](https://www.infospyware.com/utiles/rkill/) como lo ha estado realizando correctamente y dejas que finalice todo el proceso de Análisis por completo y seguidamente siga estos pasos:
**1)** **Descarga** , **Instala** , y ejecuta **[Dr.Web Cureit!](https://forospyware.com/t/manual-dr-web-curelt/142)**. Aquí te dejo su **Manual de Uso** : [Dr.Web Cureit!](https://forospyware.com/t/manual-dr-web-curelt/142), para que sepas como usarlo y configurarlo correctamente. (Elimine **"TODO"** lo que encuentre! y **"NO"** restaure **"NADA").**
Me mandas dicho **Informe** y una **Captura de Pantalla** cuando finalicen dichos Procesos de Análisis.
Quedo a la espera de su respuesta!
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [29 Enero, 2022 01:40 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/132 "2022-01-29T01:40:53Z")
Muy bien. Muchas gracias J. Luis por todo el apoyo que me estas dando.
Me pongo manos a la obra de inmediato.
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [29 Enero, 2022 01:43 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/133 "2022-01-29T01:43:10Z")
Gracias a ti por tener tanta paciencia en el Proceso de Desinfección de su ordenador y seguir todos los pasos correctamente ya que lo que persigo es un propósito y es eliminar sin excepciones y de raíz dicha infección y por ello quiero asegurarme de ello ya que esa es la finalidad que persigo! esto ya se ha convertido en todo un reto para mí por ello gracias a ti por tu paciencia y tu constancia. 😃
Cuando termine el **Proceso de Análisis** por completo, siguiendo su **manual** , y si encuentra amenazas e Infecciones, las **eliminas** y me mandas dicho **Informe.**
Quedo a la espera de su respuesta!
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [29 Enero, 2022 03:38 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/135 "2022-01-29T03:38:41Z")
Dr Web tampoco encontró amenazas
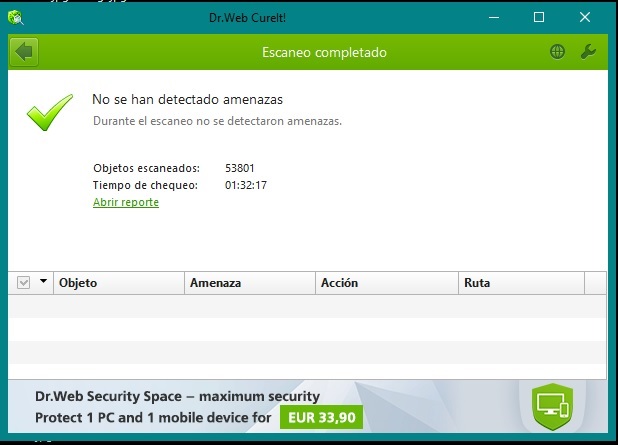
```auto
Total 53570093721 bytes in 47155 files scanned (53801 objects)
Total 47192 files (53762 objects) are clean
There are no infected objects detected
Total 37 files are raised error condition
Scan time is 01:32:17.325
```
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [29 Enero, 2022 03:48 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/137 "2022-01-29T03:48:56Z")
**IMPORTANTE:**
**Como es un poco tarde, le dejo los pasos a seguir y mañana reviso los resultados del Proceso de Análisis.** 👍
Realice todo este procedimiento en **Modo Seguro con Funciones de Red:**
En primer lugar, pásele el programa: **Rkill** como lo ha estado realizando correctamente y dejas que finalice todo el proceso de Análisis por completo y seguidamente siga estos pasos:
**1)** **Descarga** , **Instala** , y ejecuta **Eset Online Scaner**. Aquí te dejo su **Manual de Uso** : [Eset Online Scaner](https://forospyware.com/t/manual-de-eset-online-scanner/971), para que sepas como usarlo y configurarlo correctamente. (Elimine **"TODO"** lo que encuentre! y **"NO"** restaure **"NADA").**
Me mandas dicho **Informe** y una **Captura de Pantalla** cuando finalicen dichos Procesos de Análisis.
Quedo a la espera de su respuesta!
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [29 Enero, 2022 03:52 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/138 "2022-01-29T03:52:17Z")
Ok. Muchas gracias.
Hasta mañana
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [29 Enero, 2022 12:34 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/139 "2022-01-29T12:34:32Z")
Buenos días! Eset ha concluido:
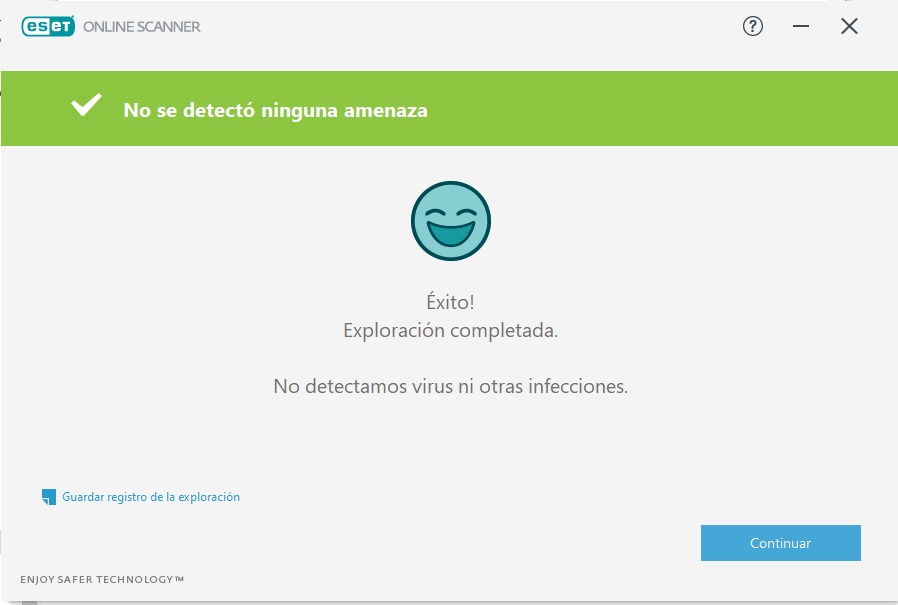
```auto
29-01-2022 9:32:33
Archivos explorados: 637332
Archivos detectados: 0
Archivos desinfectados: 0
Tiempo total de exploración: 08:34:00
Estado de la exploración: Finalizado
```
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [29 Enero, 2022 20:39 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/140 "2022-01-29T20:39:19Z")
Disculpa, hoy he tenido que salir pero llegaremos hasta el final de tu reparación! Te pongo los pasos a seguir, tardaré un poco pero te lo pongo en cuanto llegue a mi casa.
Disculpa por la demora!
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [30 Enero, 2022 00:44 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/141 "2022-01-30T00:44:32Z")
Ahora para proseguir realiza lo siguiente para asegurarnos que el sistema está bien:
Revisa en **Windows Update** si hay alguna actualización disponible. Selecciona el botón **Inicio** y ve a **Configuración** \> **Actualización y seguridad** \> **Windows Update**.
Me manda una Captura de Pantalla de todo lo que te salga.
Si no pudiera realizar dicho paso que le indico me lo comunica! 👍
Quedo a la espera de su respuesta!
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [30 Enero, 2022 03:14 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/142 "2022-01-30T03:14:28Z")
Hice 3 intentos dejando un tiempo entre cada uno pero siempre me sale el mismo mensaje:
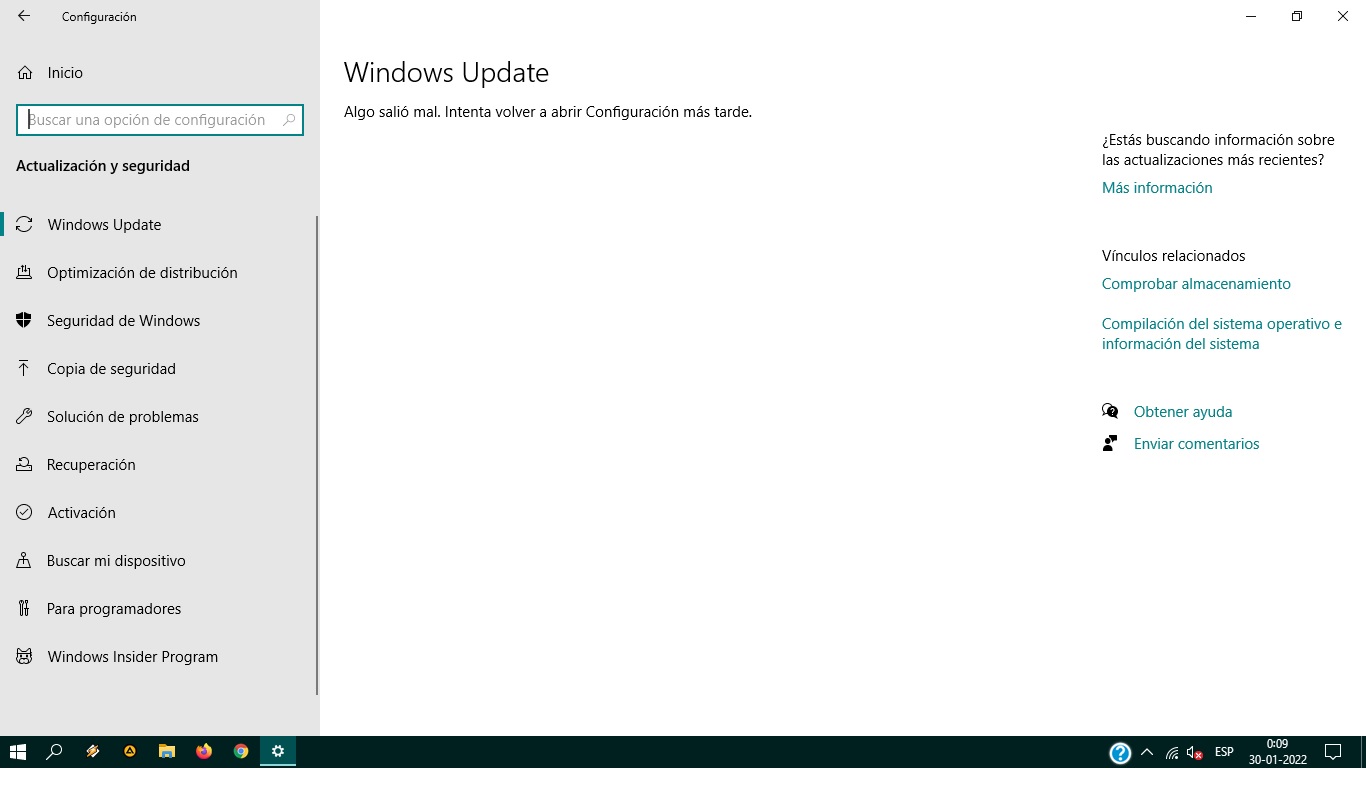
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [30 Enero, 2022 08:42 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/143 "2022-01-30T08:42:37Z")
Perfecto! Ahora vamos a intentar otro procedimiento. Te estoy preparando los pasos a seguir!
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [30 Enero, 2022 11:30 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/144 "2022-01-30T11:30:18Z")
Reinicia el ordenador y cuando lo hayas reiniciado me lo comunicas.
Quedo a la espera de su respuesta!
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [30 Enero, 2022 11:33 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/145 "2022-01-30T11:33:04Z")
Crucemos los dedos. 👍
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [30 Enero, 2022 11:33 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/146 "2022-01-30T11:33:55Z")
Comuníquemelo cuando lo hayas reiniciado y **no realice ningún paso** , sólo me lo comunicas por aquí!
Aún nos faltan algunos pasos de comprobación para que todo quede correctamente!
¿Lo ha reiniciado ya? Avíseme y no realice ningún paso, sólo avíseme!
Quedo a la espera de su respuesta!
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [30 Enero, 2022 11:56 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/149 "2022-01-30T11:56:06Z")
Si. lo reinicié. Lamentablemente volvió a aparecer el virus.
> [@Chicloi](#):
>
> no realice ningún paso, sólo avíseme!
Lo unico que hice, y no habia leído su ultimo mensaje, fue ponerlo en cuarentena como pedía windows defender
---
### Author:  [@Stubborn](https://forospyware.com/u/Stubborn)
#### Post date: [30 Enero, 2022 12:07 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/152 "2022-01-30T12:07:36Z")
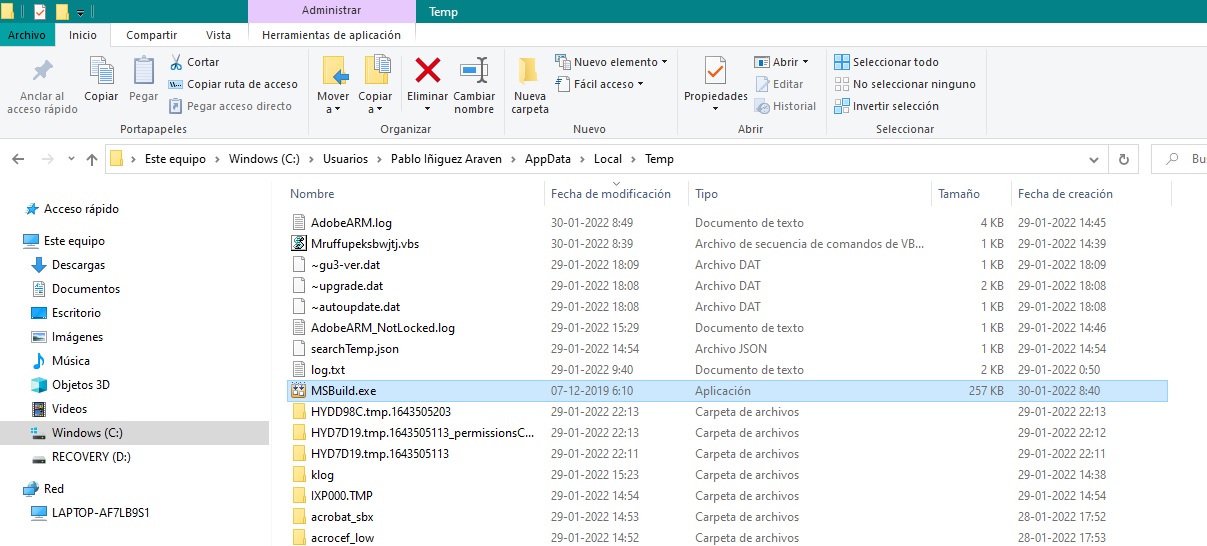
Una diferencia es que ahora apareció dos veces y tardó mas en ser bloqueado.
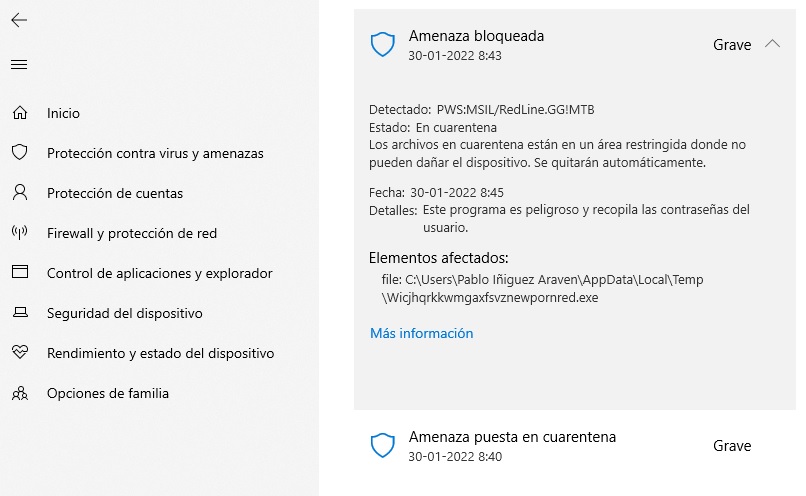
Entré a la carpeta temp y ahí esta el archivo infectado:
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [30 Enero, 2022 12:09 UTC](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936/154 "2022-01-30T12:09:29Z")
Vaya a esta hubicación:

**Elimine** la carpeta que pone: **Temp**
Cuando haya realizado este procedimiento como le indico me lo comunica por aquí!
> [@Stubborn](#):
>
> Entré a la carpeta temp y ahí esta el archivo infectado:
>
> 
**Elimine** el archivo que pone: **MSbuild.exe**
Quedo a la espera de su respuesta!
[Página anterior](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936.md?page=5)
[Página siguiente](https://forospyware.com/t/no-me-funciona-rkill-parte-1/25936.md?page=7)