# Fotos cambiada extension
**URL:** https://forospyware.com/t/fotos-cambiada-extension/29134
**Category:** Eliminar Malwares
**Created:** [20 Diciembre, 2022 17:11 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134 "2022-12-20T17:11:39Z")
**Posts on this page:** 20
**Page:** 2
### Author:  [@JCTecn1cal](https://forospyware.com/u/JCTecn1cal)
#### Post date: [29 Diciembre, 2022 21:29 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/21 "2022-12-29T21:29:55Z")
Lo que hemos hecho hasta ahora son análisis completos con **Malwarebytes** , **Eset Online** , **KVRT** y **DrWeb CureIt**
Tenemos que descartar la presencia de algún rootkit, descarga las siguientes herramientas, **guardalas en el escritorio** pero no las ejecutes aún
- [TDSSKiller](https://www.infospyware.com/antirootkits/tdsskiller/)
- [Malwarebytes Anti-Rootkit](https://downloads.malwarebytes.com/file/mbar/)
Antes de ejecutar las herramientas primero [tienes que deshabilitar tu antivirus](https://forospyware.com/t/c%C3%B3mo-deshabilitar-temporalmente-su-antivirus/82) y toda protección residente para que no interfieran con su ejecución y **mantenerlo deshabilitado durante todo el procedimiento**
Ejecuta RKill y esperas a que este termine antes de ejecutar cada Anti-Rootkit
Empezamos con TDSSKiller
- Lo ejecutas como administrador
- Después de aceptar los acuerdos de licencia de usuario y el de KSN Statement se abrira el programa
- Presione sobre **Change parameters** y deberas marcar todas las casillas para que quede de esta forma
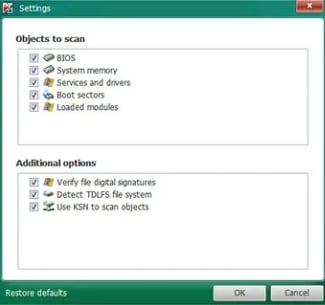
- Cuando marques la casilla **Loaded modules** TDSSKiller mostrara un mensaje solicitando que reinicies el equipo. **Este reinicio es muy importante para que TDSSKiller instale un driver que necesita para ampliar su alcance de detección**
Sigue las instrucciones de este manual
> [@Manual de TDSSKiller](https://forospyware.com/t/manual-de-tdsskiller/5059):
>
> Manual de TDSSKiller. TDSSKiller es una herramienta creada por Kaspersky Labs para eliminar los peligrosos rootkit de la familia Rootkit.Win32.TDSS: TDL1 , TDL2, TDL3, TDL4, TDSS, Tidserv, TDSServ, TDSS.mbr, Whistler, Phanta, Phiar, Trup, ZAccess, Stonedy, MBR Rootkit, Alureon, Cidox, Sinowal, y ZeroAccess entre otros. TDSSKiller es gratuita y fácil de usar. Tiene la habilitad de escanear la UEFI/BIOS desde Windows. Se puede ejecutar en el Modo Normal o en el [Modo Seguro](https://forospyware.com/t/como-iniciar-el-pc-en-modo-a-prueba-de-fallos/162) de Wind…
Para analizar tu equipo **con los ajustes que hemos hecho** y eliminar las amenazas encontradas, traes el reporte y unas capturas de lo que haya detectado TDSSKiller
Reinicia el equipo y luego ejecutas Malwarebytes Anti-Rootkit y sigue las instrucciones de este manual
> [@Manual Malwarebytes Anti-Rootkit Beta](https://forospyware.com/t/manual-malwarebytes-anti-rootkit-beta/143):
>
> Manual Malwarebytes Anti-Rootkit Beta Malwarebytes Anti-Rootkit (MBAR) es una herramienta diseñada para detectar y eliminar las formas sofisticadas y sigilosas de malware llamado “Rootkits”. Los rootkits son formas ocultas de malware que los antivirus tradicionales normalmente no pueden detectar o eliminar. Malwarebytes Anti-Rootkit (MBAR) es portable: se ejecuta desde cualquier carpeta o unidad extraíble, como una memoria USB Índice: [Descarga y ejecución](https://forospyware.com/t/manual-malwarebytes-anti-rootkit-beta/143#heading--descarga-y-ejecucion)[Análisis](https://forospyware.com/t/manual-malwarebytes-anti-rootkit-beta/143#heading--analisis)[Cuarentena](https://forospyware.com/t/manual-malwarebytes-anti-rootkit-beta/143#heading--cuarentena)[Informe de …](https://forospyware.com/t/manual-malwarebytes-anti-rootkit-beta/143#heading--informe-de-analisis)
para analizar tu equipo y eliminar todas las amenazas encontradas, observa con atención como localizar los dos reportes que son creados por esta herramienta.
Cuando respondas:
- Nos traes el reporte de TDSSKiller
- Traes los dos reportes de Malwarebytes Anti-Rootkit, **Mbar-log.txt** y **System-log.txt**
- Nos comentas cualquier problema que hayas tenido durante el procedimiento y como esta funcionando el equipo despues de realizar el procedimiento.
Saludos y esperamos tus reportes y comentarios al respecto
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [30 Diciembre, 2022 09:43 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/22 "2022-12-30T09:43:53Z")
```auto
10:29:24.0456 0x267c TDSS rootkit removing tool 3.1.0.28 Apr 9 2019 21:11:46
10:29:24.0456 0x267c UEFI system
10:29:24.0942 0x267c ============================================================
10:29:24.0942 0x267c Current date / time: 2022/12/30 10:29:24.0942
10:29:24.0942 0x267c SystemInfo:
10:29:24.0942 0x267c
10:29:24.0942 0x267c OS Version: 10.0.19044 ServicePack: 0.0
10:29:24.0942 0x267c Product type: Workstation
10:29:24.0942 0x267c ComputerName: LAPTOP-HKJ5OOUL
10:29:24.0942 0x267c UserName: mmuno
10:29:24.0942 0x267c Windows directory: C:\Windows
10:29:24.0942 0x267c System windows directory: C:\Windows
10:29:24.0942 0x267c Running under WOW64
10:29:24.0942 0x267c Processor architecture: Intel x64
10:29:24.0942 0x267c Number of processors: 8
10:29:24.0942 0x267c Page size: 0x1000
10:29:24.0942 0x267c Boot type: Normal boot
10:29:24.0942 0x267c CodeIntegrityOptions = 0x0000C001
10:29:24.0942 0x267c ============================================================
10:29:24.0944 0x267c KLMD ARK init status: drvProperties = 0xEF0F02, osBuild = 19041.0, osProperties = 0x1D
10:29:24.0945 0x267c KLMD BG init status: drvProperties = 0xEF0F02, osBuild = 19041.0, osProperties = 0x1D
10:29:24.0945 0x267c BG loaded
10:29:24.0969 0x267c System UUID: {0BC09AD4-9E13-138F-E889-4AA68BDF6EDD}
10:29:25.0050 0x267c !crdlk
10:29:25.0053 0x267c Drive \Device\Harddisk0\DR0 - Size: 0x3B9E656000 ( 238.47 Gb ), SectorSize: 0x200, Cylinders: 0x799A, SectorsPerTrack: 0x3F, TracksPerCylinder: 0xFF, Type 'W'
10:29:25.0056 0x267c ============================================================
10:29:25.0056 0x267c \Device\Harddisk0\DR0:
10:29:25.0056 0x267c GPT partitions:
10:29:25.0056 0x267c \Device\Harddisk0\DR0\Partition1: GPT, TypeGUID: {C12A7328-F81F-11D2-BA4B-00A0C93EC93B}, UniqueGUID: {C0244D3C-7047-4557-B8FD-D7E08AE932EA}, Name: EFI system partition, StartLBA 0x800, BlocksNum 0x82000
10:29:25.0057 0x267c \Device\Harddisk0\DR0\Partition2: GPT, TypeGUID: {E3C9E316-0B5C-4DB8-817D-F92DF00215AE}, UniqueGUID: {F5B4A8D3-45EA-428F-ACE3-989010EE28F6}, Name: Microsoft reserved partition, StartLBA 0x82800, BlocksNum 0x8000
10:29:25.0057 0x267c \Device\Harddisk0\DR0\Partition3: GPT, TypeGUID: {EBD0A0A2-B9E5-4433-87C0-68B6B72699C7}, UniqueGUID: {52346628-049B-4F6A-8026-80C5D9DD79E0}, Name: Basic data partition, StartLBA 0x8A800, BlocksNum 0x1D9F728F
10:29:25.0057 0x267c \Device\Harddisk0\DR0\Partition4: GPT, TypeGUID: {DE94BBA4-06D1-4D40-A16A-BFD50179D6AC}, UniqueGUID: {EC93E60D-7E63-45CB-A7FF-76D99492074C}, Name: Basic data partition, StartLBA 0x1DA82000, BlocksNum 0x20D000
10:29:25.0057 0x267c \Device\Harddisk0\DR0\Partition5: GPT, TypeGUID: {DE94BBA4-06D1-4D40-A16A-BFD50179D6AC}, UniqueGUID: {395578C9-889E-42BC-B23F-F300CC974DB1}, Name: Basic data partition, StartLBA 0x1DC8F000, BlocksNum 0x64000
10:29:25.0057 0x267c MBR partitions:
10:29:25.0057 0x267c ============================================================
10:29:25.0057 0x267c Initialize success
10:29:25.0057 0x267c ============================================================
10:35:31.0138 0x3760 ============================================================
10:35:31.0138 0x3760 Scan started
10:35:31.0138 0x3760 Mode: Manual; SigCheck; TDLFS;
10:35:31.0138 0x3760 ============================================================
10:35:31.0138 0x3760 KSN ping started
10:35:31.0228 0x3760 KSN ping finished: true
10:35:31.0275 0x3760 ================ Scan BIOS =================================
10:35:31.0275 0x3760 BIOS info: vendor = American Megatrends International, LLC., version = X515EA.305, releaseDate = 09/06/2021
10:35:31.0275 0x3760 Base board info: manufacturer = ASUSTeK COMPUTER INC., product = X515EA, version = 1.0
10:35:37.0030 0x3760 [711AFDBE6FFACC151575761F12184A34, 364F924156679CAD7A60FD5B6A76A3C698E793D7C4CAFE7ACC46E62861E1A0D2] BIOS
10:35:37.0030 0x3760 BIOS - ok
10:35:37.0030 0x3760 ================ Scan system memory ========================
10:35:37.0030 0x3760 System memory - ok
10:35:37.0030 0x3760 ================ Scan services =============================
10:35:37.0045 0x3760 1394ohci - ok
10:35:37.0045 0x3760 3ware - ok
10:35:37.0045 0x3760 AarSvc - ok
10:35:37.0061 0x3760 ACPI - ok
10:35:37.0061 0x3760 AcpiDev - ok
10:35:37.0061 0x3760 acpiex - ok
10:35:37.0061 0x3760 acpipagr - ok
10:35:37.0061 0x3760 AcpiPmi - ok
10:35:37.0061 0x3760 acpitime - ok
10:35:37.0061 0x3760 Acx01000 - ok
10:35:37.0061 0x3760 ADP80XX - ok
10:35:37.0077 0x3760 AFD - ok
10:35:37.0077 0x3760 afunix - ok
10:35:37.0077 0x3760 ahcache - ok
10:35:37.0077 0x3760 AJRouter - ok
10:35:37.0077 0x3760 ALG - ok
10:35:37.0077 0x3760 amdgpio2 - ok
10:35:37.0077 0x3760 amdi2c - ok
10:35:37.0077 0x3760 AmdK8 - ok
10:35:37.0092 0x3760 AmdPPM - ok
10:35:37.0092 0x3760 amdsata - ok
10:35:37.0092 0x3760 amdsbs - ok
10:35:37.0092 0x3760 amdxata - ok
10:35:37.0092 0x3760 AppID - ok
10:35:37.0092 0x3760 AppIDSvc - ok
10:35:37.0092 0x3760 Appinfo - ok
10:35:37.0092 0x3760 applockerfltr - ok
10:35:37.0092 0x3760 AppReadiness - ok
10:35:37.0108 0x3760 AppXSvc - ok
10:35:37.0108 0x3760 arcsas - ok
10:35:37.0108 0x3760 AsusAppService - ok
10:35:37.0108 0x3760 ASUSLinkNear - ok
10:35:37.0108 0x3760 ASUSLinkRemote - ok
10:35:37.0108 0x3760 AsusNumpadKbd - ok
10:35:37.0108 0x3760 AsusNumpadPTP - ok
10:35:37.0108 0x3760 ASUSOptimization - ok
10:35:37.0123 0x3760 AsusPTPDrv - ok
10:35:37.0123 0x3760 AsusPTPService - ok
10:35:37.0123 0x3760 AsusSAIO - ok
10:35:37.0123 0x3760 ASUSSoftwareManager - ok
10:35:37.0123 0x3760 ASUSSwitch - ok
10:35:37.0123 0x3760 ASUSSystemAnalysis - ok
10:35:37.0123 0x3760 ASUSSystemDiagnosis - ok
10:35:37.0123 0x3760 AsyncMac - ok
10:35:37.0139 0x3760 atapi - ok
10:35:37.0139 0x3760 ATKWMIACPIIO - ok
10:35:37.0139 0x3760 AudioEndpointBuilder - ok
10:35:37.0139 0x3760 Audiosrv - ok
10:35:37.0139 0x3760 autotimesvc - ok
10:35:37.0139 0x3760 AviraFallbackUpdater - ok
10:35:37.0139 0x3760 AviraOptimizerHost - ok
10:35:37.0139 0x3760 AviraPhantomVPN - ok
10:35:37.0155 0x3760 AviraSecurity - ok
10:35:37.0155 0x3760 AviraSecurityUpdater - ok
10:35:37.0155 0x3760 AX88179 - ok
10:35:37.0155 0x3760 AxInstSV - ok
10:35:37.0155 0x3760 b06bdrv - ok
10:35:37.0155 0x3760 bam - ok
10:35:37.0155 0x3760 BasicDisplay - ok
10:35:37.0170 0x3760 BasicRender - ok
10:35:37.0170 0x3760 BcastDVRUserService - ok
10:35:37.0186 0x3760 bcmfn2 - ok
10:35:37.0186 0x3760 BDESVC - ok
10:35:37.0186 0x3760 BdNet - ok
10:35:37.0186 0x3760 BdSentry - ok
10:35:37.0186 0x3760 Beep - ok
10:35:37.0186 0x3760 BFE - ok
10:35:37.0186 0x3760 bindflt - ok
10:35:37.0186 0x3760 BITS - ok
10:35:37.0202 0x3760 BluetoothUserService - ok
10:35:37.0202 0x3760 bowser - ok
10:35:37.0202 0x3760 BrokerInfrastructure - ok
10:35:37.0202 0x3760 BTAGService - ok
10:35:37.0202 0x3760 BthA2dp - ok
10:35:37.0202 0x3760 BthAvctpSvc - ok
10:35:37.0202 0x3760 BthEnum - ok
10:35:37.0202 0x3760 BthHFEnum - ok
10:35:37.0218 0x3760 BthLEEnum - ok
10:35:37.0218 0x3760 BthMini - ok
10:35:37.0218 0x3760 BTHMODEM - ok
10:35:37.0218 0x3760 BthPan - ok
10:35:37.0218 0x3760 BTHPORT - ok
10:35:37.0218 0x3760 bthserv - ok
10:35:37.0218 0x3760 BTHUSB - ok
10:35:37.0218 0x3760 bttflt - ok
10:35:37.0218 0x3760 buttonconverter - ok
10:35:37.0233 0x3760 CAD - ok
10:35:37.0237 0x3760 camsvc - ok
10:35:37.0238 0x3760 CaptureService - ok
10:35:37.0238 0x3760 cbdhsvc - ok
10:35:37.0238 0x3760 cdfs - ok
10:35:37.0238 0x3760 CDPSvc - ok
10:35:37.0238 0x3760 CDPUserSvc - ok
10:35:37.0238 0x3760 cdrom - ok
10:35:37.0254 0x3760 CertPropSvc - ok
10:35:37.0256 0x3760 cht4iscsi - ok
10:35:37.0256 0x3760 cht4vbd - ok
10:35:37.0256 0x3760 CimFS - ok
10:35:37.0256 0x3760 circlass - ok
10:35:37.0256 0x3760 CldFlt - ok
10:35:37.0256 0x3760 CLFS - ok
10:35:37.0256 0x3760 ClickToRunSvc - ok
10:35:37.0256 0x3760 ClipSVC - ok
10:35:37.0272 0x3760 CmBatt - ok
10:35:37.0272 0x3760 CNG - ok
10:35:37.0272 0x3760 cnghwassist - ok
10:35:37.0272 0x3760 CompositeBus - ok
10:35:37.0272 0x3760 COMSysApp - ok
10:35:37.0282 0x3760 condrv - ok
10:35:37.0282 0x3760 ConsentUxUserSvc - ok
10:35:37.0282 0x3760 CoreMessagingRegistrar - ok
10:35:37.0282 0x3760 cplspcon - ok
10:35:37.0282 0x3760 CredentialEnrollmentManagerUserSvc - ok
10:35:37.0282 0x3760 CredentialEnrollmentManagerUserSvc_80b11 - ok
10:35:37.0297 0x3760 CryptSvc - ok
10:35:37.0297 0x3760 dam - ok
10:35:37.0297 0x3760 DcomLaunch - ok
10:35:37.0297 0x3760 dcsvc - ok
10:35:37.0297 0x3760 defragsvc - ok
10:35:37.0297 0x3760 DeviceAssociationBrokerSvc - ok
10:35:37.0297 0x3760 DeviceAssociationService - ok
10:35:37.0297 0x3760 DeviceInstall - ok
10:35:37.0313 0x3760 DevicePickerUserSvc - ok
10:35:37.0313 0x3760 DevicesFlowUserSvc - ok
10:35:37.0313 0x3760 DevQueryBroker - ok
10:35:37.0313 0x3760 Dfsc - ok
10:35:37.0313 0x3760 Dhcp - ok
10:35:37.0313 0x3760 diagnosticshub.standardcollector.service - ok
10:35:37.0313 0x3760 diagsvc - ok
10:35:37.0329 0x3760 DiagTrack - ok
10:35:37.0329 0x3760 disk - ok
10:35:37.0329 0x3760 DispBrokerDesktopSvc - ok
10:35:37.0329 0x3760 DisplayEnhancementService - ok
10:35:37.0329 0x3760 DmEnrollmentSvc - ok
10:35:37.0329 0x3760 dmvsc - ok
10:35:37.0329 0x3760 dmwappushservice - ok
10:35:37.0329 0x3760 Dnscache - ok
10:35:37.0344 0x3760 dot3svc - ok
10:35:37.0344 0x3760 DPS - ok
10:35:37.0344 0x3760 dptf_acpi - ok
10:35:37.0344 0x3760 dptf_cpu - ok
10:35:37.0344 0x3760 drmkaud - ok
10:35:37.0344 0x3760 DsmSvc - ok
10:35:37.0344 0x3760 DsSvc - ok
10:35:37.0344 0x3760 DtsApo4Service - ok
10:35:37.0360 0x3760 DusmSvc - ok
10:35:37.0360 0x3760 DXGKrnl - ok
10:35:37.0360 0x3760 Eaphost - ok
10:35:37.0360 0x3760 ebdrv - ok
10:35:37.0360 0x3760 edgeupdate - ok
10:35:37.0360 0x3760 edgeupdatem - ok
10:35:37.0360 0x3760 EFS - ok
10:35:37.0360 0x3760 EhStorClass - ok
10:35:37.0360 0x3760 EhStorTcgDrv - ok
10:35:37.0376 0x3760 embeddedmode - ok
10:35:37.0376 0x3760 EndpointProtectionService - ok
10:35:37.0376 0x3760 EndpointProtectionService2 - ok
10:35:37.0376 0x3760 EntAppSvc - ok
10:35:37.0376 0x3760 ErrDev - ok
10:35:37.0376 0x3760 esifsvc - ok
10:35:37.0376 0x3760 esif_lf - ok
10:35:37.0391 0x3760 ESProtectionDriver - ok
10:35:37.0391 0x3760 EventLog - ok
10:35:37.0407 0x3760 EventSystem - ok
10:35:37.0407 0x3760 exfat - ok
10:35:37.0407 0x3760 fastfat - ok
10:35:37.0407 0x3760 Fax - ok
10:35:37.0407 0x3760 fdc - ok
10:35:37.0407 0x3760 fdPHost - ok
10:35:37.0407 0x3760 FDResPub - ok
10:35:37.0407 0x3760 fhsvc - ok
10:35:37.0423 0x3760 FileCrypt - ok
10:35:37.0423 0x3760 FileInfo - ok
10:35:37.0423 0x3760 Filetrace - ok
10:35:37.0423 0x3760 flpydisk - ok
10:35:37.0423 0x3760 FltMgr - ok
10:35:37.0423 0x3760 FontCache - ok
10:35:37.0423 0x3760 FoxitReaderUpdateService - ok
10:35:37.0423 0x3760 FrameServer - ok
10:35:37.0438 0x3760 FsDepends - ok
10:35:37.0438 0x3760 Fs_Rec - ok
10:35:37.0438 0x3760 fvevol - ok
10:35:37.0438 0x3760 gencounter - ok
10:35:37.0438 0x3760 genericusbfn - ok
10:35:37.0438 0x3760 GoogleChromeElevationService - ok
10:35:37.0438 0x3760 GPIOClx0101 - ok
10:35:37.0438 0x3760 gpsvc - ok
10:35:37.0454 0x3760 GpuEnergyDrv - ok
10:35:37.0454 0x3760 GraphicsPerfSvc - ok
10:35:37.0454 0x3760 gupdate - ok
10:35:37.0454 0x3760 gupdatem - ok
10:35:37.0454 0x3760 HdAudAddService - ok
10:35:37.0454 0x3760 HDAudBus - ok
10:35:37.0454 0x3760 HidBatt - ok
10:35:37.0454 0x3760 HidBth - ok
10:35:37.0470 0x3760 hidi2c - ok
10:35:37.0470 0x3760 hidinterrupt - ok
10:35:37.0470 0x3760 HidIr - ok
10:35:37.0470 0x3760 hidserv - ok
10:35:37.0470 0x3760 hidspi - ok
10:35:37.0470 0x3760 HidUsb - ok
10:35:37.0470 0x3760 HpSAMD - ok
10:35:37.0485 0x3760 HTTP - ok
10:35:37.0485 0x3760 hvcrash - ok
10:35:37.0485 0x3760 HvHost - ok
10:35:37.0485 0x3760 hvservice - ok
10:35:37.0485 0x3760 HwNClx0101 - ok
10:35:37.0485 0x3760 hwpolicy - ok
10:35:37.0485 0x3760 hyperkbd - ok
10:35:37.0485 0x3760 HyperVideo - ok
10:35:37.0501 0x3760 i8042prt - ok
10:35:37.0501 0x3760 iagpio - ok
10:35:37.0501 0x3760 iai2c - ok
10:35:37.0501 0x3760 iaLPSS2i_GPIO2 - ok
10:35:37.0501 0x3760 iaLPSS2i_GPIO2_BXT_P - ok
10:35:37.0501 0x3760 iaLPSS2i_GPIO2_CNL - ok
10:35:37.0501 0x3760 iaLPSS2i_GPIO2_GLK - ok
10:35:37.0516 0x3760 iaLPSS2i_I2C - ok
10:35:37.0516 0x3760 iaLPSS2i_I2C_BXT_P - ok
10:35:37.0516 0x3760 iaLPSS2i_I2C_CNL - ok
10:35:37.0516 0x3760 iaLPSS2i_I2C_GLK - ok
10:35:37.0516 0x3760 iaLPSS2_GPIO2_TGL - ok
10:35:37.0516 0x3760 iaLPSS2_I2C_TGL - ok
10:35:37.0516 0x3760 iaLPSS2_SPI_TGL - ok
10:35:37.0516 0x3760 iaLPSS2_UART2_TGL - ok
10:35:37.0532 0x3760 iaLPSSi_GPIO - ok
10:35:37.0532 0x3760 iaLPSSi_I2C - ok
10:35:37.0532 0x3760 iaStorAfs - ok
10:35:37.0532 0x3760 iaStorAfsService - ok
10:35:37.0532 0x3760 iaStorAVC - ok
10:35:37.0532 0x3760 iaStorV - ok
10:35:37.0532 0x3760 iaStorVD - ok
10:35:37.0548 0x3760 ibbus - ok
10:35:37.0548 0x3760 ibtsiva - ok
10:35:37.0548 0x3760 ibtusb - ok
10:35:37.0548 0x3760 icssvc - ok
10:35:37.0548 0x3760 igccservice - ok
10:35:37.0548 0x3760 igfxCUIService2.0.0.0 - ok
10:35:37.0548 0x3760 igfxn - ok
10:35:37.0548 0x3760 IKEEXT - ok
10:35:37.0563 0x3760 IndirectKmd - ok
10:35:37.0563 0x3760 InstallService - ok
10:35:37.0563 0x3760 IntcAudioBus - ok
10:35:37.0563 0x3760 IntcAzAudAddService - ok
10:35:37.0563 0x3760 IntcBTAu - ok
10:35:37.0563 0x3760 IntcOED - ok
10:35:37.0563 0x3760 IntcUSB - ok
10:35:37.0579 0x3760 Intel(R) Capability Licensing Service TCP IP Interface - ok
10:35:37.0579 0x3760 Intel(R) TPM Provisioning Service - ok
10:35:37.0595 0x3760 IntelAudioService - ok
10:35:37.0595 0x3760 IntelGNA - ok
10:35:37.0595 0x3760 intelide - ok
10:35:37.0595 0x3760 intelpep - ok
10:35:37.0595 0x3760 intelpmax - ok
10:35:37.0595 0x3760 intelppm - ok
10:35:37.0595 0x3760 iorate - ok
10:35:37.0610 0x3760 IpFilterDriver - ok
10:35:37.0610 0x3760 iphlpsvc - ok
10:35:37.0610 0x3760 IPMIDRV - ok
10:35:37.0610 0x3760 IPNAT - ok
10:35:37.0610 0x3760 IPT - ok
10:35:37.0610 0x3760 IpxlatCfgSvc - ok
10:35:37.0610 0x3760 isapnp - ok
10:35:37.0610 0x3760 iScsiPrt - ok
10:35:37.0626 0x3760 ItSas35i - ok
10:35:37.0626 0x3760 jhi_service - ok
10:35:37.0626 0x3760 kbdclass - ok
10:35:37.0626 0x3760 kbdhid - ok
10:35:37.0626 0x3760 kdnic - ok
10:35:37.0626 0x3760 KeyIso - ok
10:35:37.0626 0x3760 KSecDD - ok
10:35:37.0641 0x3760 KSecPkg - ok
10:35:37.0641 0x3760 ksthunk - ok
10:35:37.0641 0x3760 KtmRm - ok
10:35:37.0641 0x3760 LanmanServer - ok
10:35:37.0641 0x3760 LanmanWorkstation - ok
10:35:37.0641 0x3760 lfsvc - ok
10:35:37.0641 0x3760 LicenseManager - ok
10:35:37.0657 0x3760 lltdio - ok
10:35:37.0657 0x3760 lltdsvc - ok
10:35:37.0657 0x3760 lmhosts - ok
10:35:37.0657 0x3760 LMS - ok
10:35:37.0657 0x3760 LSI_SAS - ok
10:35:37.0657 0x3760 LSI_SAS2i - ok
10:35:37.0673 0x3760 LSI_SAS3i - ok
10:35:37.0673 0x3760 LSI_SSS - ok
10:35:37.0673 0x3760 LSM - ok
10:35:37.0673 0x3760 luafv - ok
10:35:37.0673 0x3760 LxpSvc - ok
10:35:37.0673 0x3760 MapsBroker - ok
10:35:37.0673 0x3760 mausbhost - ok
10:35:37.0688 0x3760 mausbip - ok
10:35:37.0688 0x3760 MBAMChameleon - ok
10:35:37.0688 0x3760 MbamElam - ok
10:35:37.0688 0x3760 MBAMFarflt - ok
10:35:37.0704 0x3760 MBAMProtection - ok
10:35:37.0704 0x3760 MBAMService - ok
10:35:37.0704 0x3760 MBAMSwissArmy - ok
10:35:37.0704 0x3760 MBAMWebProtection - ok
10:35:37.0704 0x3760 MbbCx - ok
10:35:37.0720 0x3760 McpManagementService - ok
10:35:37.0720 0x3760 megasas - ok
10:35:37.0720 0x3760 megasas2i - ok
10:35:37.0720 0x3760 megasas35i - ok
10:35:37.0720 0x3760 megasr - ok
10:35:37.0720 0x3760 MEIx64 - ok
10:35:37.0720 0x3760 MessagingService - ok
10:35:37.0735 0x3760 MicrosoftEdgeElevationService - ok
10:35:37.0735 0x3760 Microsoft_Bluetooth_AvrcpTransport - ok
10:35:37.0735 0x3760 MixedRealityOpenXRSvc - ok
10:35:37.0735 0x3760 mlx4_bus - ok
10:35:37.0735 0x3760 MMCSS - ok
10:35:37.0735 0x3760 Modem - ok
10:35:37.0751 0x3760 monitor - ok
10:35:37.0751 0x3760 mouclass - ok
10:35:37.0751 0x3760 mouhid - ok
10:35:37.0751 0x3760 mountmgr - ok
10:35:37.0751 0x3760 MozillaMaintenance - ok
10:35:37.0751 0x3760 mpsdrv - ok
10:35:37.0751 0x3760 mpssvc - ok
10:35:37.0766 0x3760 MRxDAV - ok
10:35:37.0766 0x3760 mrxsmb - ok
10:35:37.0766 0x3760 mrxsmb20 - ok
10:35:37.0766 0x3760 MsBridge - ok
10:35:37.0766 0x3760 MSDTC - ok
10:35:37.0766 0x3760 Msfs - ok
10:35:37.0782 0x3760 msgpiowin32 - ok
10:35:37.0782 0x3760 mshidkmdf - ok
10:35:37.0782 0x3760 mshidumdf - ok
10:35:37.0782 0x3760 msisadrv - ok
10:35:37.0782 0x3760 MSiSCSI - ok
10:35:37.0782 0x3760 msiserver - ok
10:35:37.0782 0x3760 MSKSSRV - ok
10:35:37.0798 0x3760 MsLldp - ok
10:35:37.0798 0x3760 MSPCLOCK - ok
10:35:37.0798 0x3760 MSPQM - ok
10:35:37.0798 0x3760 MsQuic - ok
10:35:37.0798 0x3760 MsRPC - ok
10:35:37.0798 0x3760 mssmbios - ok
10:35:37.0813 0x3760 MSTEE - ok
10:35:37.0813 0x3760 MTConfig - ok
10:35:37.0813 0x3760 Mup - ok
10:35:37.0813 0x3760 mvumis - ok
10:35:37.0813 0x3760 NativeWifiP - ok
10:35:37.0829 0x3760 NaturalAuthentication - ok
10:35:37.0829 0x3760 NcaSvc - ok
10:35:37.0829 0x3760 NcbService - ok
10:35:37.0829 0x3760 NcdAutoSetup - ok
10:35:37.0829 0x3760 ndfltr - ok
10:35:37.0829 0x3760 NDIS - ok
10:35:37.0829 0x3760 NdisCap - ok
10:35:37.0845 0x3760 NdisImPlatform - ok
10:35:37.0845 0x3760 NdisTapi - ok
10:35:37.0845 0x3760 Ndisuio - ok
10:35:37.0845 0x3760 NdisVirtualBus - ok
10:35:37.0845 0x3760 NdisWan - ok
10:35:37.0845 0x3760 ndiswanlegacy - ok
10:35:37.0845 0x3760 NDKPing - ok
10:35:37.0860 0x3760 ndproxy - ok
10:35:37.0860 0x3760 Ndu - ok
10:35:37.0860 0x3760 NetAdapterCx - ok
10:35:37.0860 0x3760 NetBIOS - ok
10:35:37.0860 0x3760 NetBT - ok
10:35:37.0860 0x3760 Netlogon - ok
10:35:37.0876 0x3760 Netman - ok
10:35:37.0876 0x3760 netprofm - ok
10:35:37.0876 0x3760 netprotection_network_filter - ok
10:35:37.0876 0x3760 netprotection_network_filter2 - ok
10:35:37.0876 0x3760 NetSetupSvc - ok
10:35:37.0876 0x3760 NetTcpPortSharing - ok
10:35:37.0892 0x3760 netvsc - ok
10:35:37.0892 0x3760 Netwtw10 - ok
10:35:37.0892 0x3760 NgcCtnrSvc - ok
10:35:37.0892 0x3760 NgcSvc - ok
10:35:37.0892 0x3760 NlaSvc - ok
10:35:37.0892 0x3760 Npfs - ok
10:35:37.0907 0x3760 npsvctrig - ok
10:35:37.0907 0x3760 nsi - ok
10:35:37.0907 0x3760 nsiproxy - ok
10:35:37.0907 0x3760 Ntfs - ok
10:35:37.0907 0x3760 Null - ok
10:35:37.0907 0x3760 nvdimm - ok
10:35:37.0923 0x3760 nvraid - ok
10:35:37.0923 0x3760 nvstor - ok
10:35:37.0923 0x3760 OneSyncSvc - ok
10:35:37.0923 0x3760 p2pimsvc - ok
10:35:37.0923 0x3760 p2psvc - ok
10:35:37.0923 0x3760 Parport - ok
10:35:37.0939 0x3760 partmgr - ok
10:35:37.0939 0x3760 PcaSvc - ok
10:35:37.0939 0x3760 pci - ok
10:35:37.0939 0x3760 pciide - ok
10:35:37.0939 0x3760 pcmcia - ok
10:35:37.0939 0x3760 pcw - ok
10:35:37.0954 0x3760 pdc - ok
10:35:37.0954 0x3760 PEAUTH - ok
10:35:37.0954 0x3760 perceptionsimulation - ok
10:35:37.0954 0x3760 percsas2i - ok
10:35:37.0954 0x3760 percsas3i - ok
10:35:37.0954 0x3760 PerfHost - ok
10:35:37.0970 0x3760 PhoneSvc - ok
10:35:37.0970 0x3760 PIEServiceNew - ok
10:35:37.0970 0x3760 PimIndexMaintenanceSvc - ok
10:35:37.0986 0x3760 PktMon - ok
10:35:37.0986 0x3760 pla - ok
10:35:37.0986 0x3760 PlugPlay - ok
10:35:38.0001 0x3760 pmem - ok
10:35:38.0001 0x3760 PNPMEM - ok
10:35:38.0001 0x3760 PNRPAutoReg - ok
10:35:38.0001 0x3760 PNRPsvc - ok
10:35:38.0001 0x3760 PolicyAgent - ok
10:35:38.0001 0x3760 portcfg - ok
10:35:38.0017 0x3760 Power - ok
10:35:38.0017 0x3760 PptpMiniport - ok
10:35:38.0017 0x3760 PrintNotify - ok
10:35:38.0017 0x3760 PrintWorkflowUserSvc - ok
10:35:38.0017 0x3760 Processor - ok
10:35:38.0017 0x3760 ProfSvc - ok
10:35:38.0032 0x3760 Psched - ok
10:35:38.0032 0x3760 PushToInstall - ok
10:35:38.0032 0x3760 QWAVE - ok
10:35:38.0032 0x3760 QWAVEdrv - ok
10:35:38.0032 0x3760 Ramdisk - ok
10:35:38.0032 0x3760 RasAcd - ok
10:35:38.0048 0x3760 RasAgileVpn - ok
10:35:38.0048 0x3760 RasAuto - ok
10:35:38.0048 0x3760 Rasl2tp - ok
10:35:38.0048 0x3760 RasMan - ok
10:35:38.0048 0x3760 RasPppoe - ok
10:35:38.0048 0x3760 RasSstp - ok
10:35:38.0064 0x3760 rdbss - ok
10:35:38.0064 0x3760 rdpbus - ok
10:35:38.0064 0x3760 RDPDR - ok
10:35:38.0064 0x3760 RdpVideoMiniport - ok
10:35:38.0064 0x3760 rdyboost - ok
10:35:38.0079 0x3760 ReFS - ok
10:35:38.0079 0x3760 ReFSv1 - ok
10:35:38.0079 0x3760 RemoteAccess - ok
10:35:38.0095 0x3760 RemoteRegistry - ok
10:35:38.0095 0x3760 RetailDemo - ok
10:35:38.0095 0x3760 RFCOMM - ok
10:35:38.0095 0x3760 rhproxy - ok
10:35:38.0111 0x3760 RmSvc - ok
10:35:38.0111 0x3760 RpcEptMapper - ok
10:35:38.0111 0x3760 RpcLocator - ok
10:35:38.0111 0x3760 RpcSs - ok
10:35:38.0111 0x3760 rspndr - ok
10:35:38.0111 0x3760 RstMwService - ok
10:35:38.0126 0x3760 RtkAudioUniversalService - ok
10:35:38.0126 0x3760 rtp_elam - ok
10:35:38.0126 0x3760 rtp_filesystem_filter - ok
10:35:38.0126 0x3760 rtp_process_monitor - ok
10:35:38.0126 0x3760 rtp_traverse - ok
10:35:38.0126 0x3760 RTSUER - ok
10:35:38.0142 0x3760 s3cap - ok
10:35:38.0142 0x3760 SamSs - ok
10:35:38.0142 0x3760 sbp2port - ok
10:35:38.0142 0x3760 SCardSvr - ok
10:35:38.0142 0x3760 ScDeviceEnum - ok
10:35:38.0142 0x3760 scfilter - ok
10:35:38.0157 0x3760 Schedule - ok
10:35:38.0157 0x3760 scmbus - ok
10:35:38.0157 0x3760 SCPolicySvc - ok
10:35:38.0157 0x3760 sdbus - ok
10:35:38.0157 0x3760 SDFRd - ok
10:35:38.0157 0x3760 SDRSVC - ok
10:35:38.0173 0x3760 sdstor - ok
10:35:38.0173 0x3760 seclogon - ok
10:35:38.0173 0x3760 SecurityHealthService - ok
10:35:38.0173 0x3760 SEMgrSvc - ok
10:35:38.0173 0x3760 SENS - ok
10:35:38.0173 0x3760 SensorDataService - ok
10:35:38.0189 0x3760 SensorService - ok
10:35:38.0189 0x3760 SensrSvc - ok
10:35:38.0189 0x3760 SerCx - ok
10:35:38.0189 0x3760 SerCx2 - ok
10:35:38.0189 0x3760 Serenum - ok
10:35:38.0189 0x3760 Serial - ok
10:35:38.0205 0x3760 sermouse - ok
10:35:38.0205 0x3760 SessionEnv - ok
10:35:38.0205 0x3760 sfloppy - ok
10:35:38.0205 0x3760 SgrmAgent - ok
10:35:38.0205 0x3760 SgrmBroker - ok
10:35:38.0220 0x3760 SharedAccess - ok
10:35:38.0220 0x3760 SharedRealitySvc - ok
10:35:38.0236 0x3760 ShellHWDetection - ok
10:35:38.0236 0x3760 shpamsvc - ok
10:35:38.0236 0x3760 SiSRaid2 - ok
10:35:38.0236 0x3760 SiSRaid4 - ok
10:35:38.0236 0x3760 SmartSAMD - ok
10:35:38.0236 0x3760 smphost - ok
10:35:38.0252 0x3760 SmsRouter - ok
10:35:38.0252 0x3760 SNMPTRAP - ok
10:35:38.0252 0x3760 spaceparser - ok
10:35:38.0252 0x3760 spaceport - ok
10:35:38.0252 0x3760 SpatialGraphFilter - ok
10:35:38.0267 0x3760 SpbCx - ok
10:35:38.0267 0x3760 spectrum - ok
10:35:38.0267 0x3760 Spooler - ok
10:35:38.0267 0x3760 sppsvc - ok
10:35:38.0267 0x3760 srv2 - ok
10:35:38.0283 0x3760 srvnet - ok
10:35:38.0283 0x3760 SSDPSRV - ok
10:35:38.0283 0x3760 ssh-agent - ok
10:35:38.0283 0x3760 SstpSvc - ok
10:35:38.0283 0x3760 StateRepository - ok
10:35:38.0283 0x3760 stexstor - ok
10:35:38.0298 0x3760 stisvc - ok
10:35:38.0298 0x3760 storahci - ok
10:35:38.0298 0x3760 storflt - ok
10:35:38.0298 0x3760 stornvme - ok
10:35:38.0298 0x3760 storqosflt - ok
10:35:38.0298 0x3760 StorSvc - ok
10:35:38.0314 0x3760 storufs - ok
10:35:38.0314 0x3760 storvsc - ok
10:35:38.0314 0x3760 svsvc - ok
10:35:38.0314 0x3760 swenum - ok
10:35:38.0314 0x3760 swprv - ok
10:35:38.0330 0x3760 Synth3dVsc - ok
10:35:38.0330 0x3760 SysMain - ok
10:35:38.0330 0x3760 SystemEventsBroker - ok
10:35:38.0330 0x3760 TabletInputService - ok
10:35:38.0330 0x3760 TapiSrv - ok
10:35:38.0330 0x3760 Tcpip - ok
10:35:38.0345 0x3760 Tcpip6 - ok
10:35:38.0345 0x3760 tcpipreg - ok
10:35:38.0345 0x3760 tdx - ok
10:35:38.0345 0x3760 Telemetry - ok
10:35:38.0361 0x3760 terminpt - ok
10:35:38.0361 0x3760 TermService - ok
10:35:38.0361 0x3760 Themes - ok
10:35:38.0361 0x3760 TieringEngineService - ok
10:35:38.0361 0x3760 TimeBrokerSvc - ok
10:35:38.0361 0x3760 TokenBroker - ok
10:35:38.0378 0x3760 TPM - ok
10:35:38.0378 0x3760 TrkWks - ok
10:35:38.0378 0x3760 TroubleshootingSvc - ok
10:35:38.0378 0x3760 TrustedInstaller - ok
10:35:38.0378 0x3760 TsUsbFlt - ok
10:35:38.0394 0x3760 TsUsbGD - ok
10:35:38.0394 0x3760 tunnel - ok
10:35:38.0394 0x3760 tzautoupdate - ok
10:35:38.0394 0x3760 UASPStor - ok
10:35:38.0394 0x3760 UcmCx0101 - ok
10:35:38.0409 0x3760 UcmTcpciCx0101 - ok
10:35:38.0409 0x3760 UcmUcsiAcpiClient - ok
10:35:38.0409 0x3760 UcmUcsiCx0101 - ok
10:35:38.0409 0x3760 Ucx01000 - ok
10:35:38.0409 0x3760 UdeCx - ok
10:35:38.0409 0x3760 udfs - ok
10:35:38.0425 0x3760 UdkUserSvc - ok
10:35:38.0425 0x3760 UEFI - ok
10:35:38.0440 0x3760 Ufx01000 - ok
10:35:38.0440 0x3760 UfxChipidea - ok
10:35:38.0440 0x3760 ufxsynopsys - ok
10:35:38.0440 0x3760 uhssvc - ok
10:35:38.0456 0x3760 umbus - ok
10:35:38.0456 0x3760 UmPass - ok
10:35:38.0456 0x3760 UmRdpService - ok
10:35:38.0456 0x3760 UnistoreSvc - ok
10:35:38.0456 0x3760 upnphost - ok
10:35:38.0472 0x3760 UrsChipidea - ok
10:35:38.0472 0x3760 UrsCx01000 - ok
10:35:38.0472 0x3760 UrsSynopsys - ok
10:35:38.0472 0x3760 usbaudio - ok
10:35:38.0472 0x3760 usbaudio2 - ok
10:35:38.0487 0x3760 usbccgp - ok
10:35:38.0487 0x3760 usbcir - ok
10:35:38.0487 0x3760 usbehci - ok
10:35:38.0487 0x3760 usbhub - ok
10:35:38.0487 0x3760 USBHUB3 - ok
10:35:38.0503 0x3760 usbohci - ok
10:35:38.0503 0x3760 usbprint - ok
10:35:38.0503 0x3760 usbser - ok
10:35:38.0503 0x3760 USBSTOR - ok
10:35:38.0503 0x3760 usbuhci - ok
10:35:38.0519 0x3760 usbvideo - ok
10:35:38.0519 0x3760 USBXHCI - ok
10:35:38.0519 0x3760 UserDataSvc - ok
10:35:38.0519 0x3760 UserManager - ok
10:35:38.0534 0x3760 UsoSvc - ok
10:35:38.0534 0x3760 VacSvc - ok
10:35:38.0534 0x3760 VaultSvc - ok
10:35:38.0534 0x3760 vdrvroot - ok
10:35:38.0534 0x3760 vds - ok
10:35:38.0534 0x3760 VerifierExt - ok
10:35:38.0550 0x3760 vhdmp - ok
10:35:38.0550 0x3760 vhf - ok
10:35:38.0550 0x3760 Vid - ok
10:35:38.0550 0x3760 VirtualRender - ok
10:35:38.0550 0x3760 vmbus - ok
10:35:38.0565 0x3760 VMBusHID - ok
10:35:38.0565 0x3760 vmgid - ok
10:35:38.0565 0x3760 vmicguestinterface - ok
10:35:38.0565 0x3760 vmicheartbeat - ok
10:35:38.0565 0x3760 vmickvpexchange - ok
10:35:38.0565 0x3760 vmicrdv - ok
10:35:38.0581 0x3760 vmicshutdown - ok
10:35:38.0581 0x3760 vmictimesync - ok
10:35:38.0581 0x3760 vmicvmsession - ok
10:35:38.0581 0x3760 vmicvss - ok
10:35:38.0581 0x3760 volmgr - ok
10:35:38.0597 0x3760 volmgrx - ok
10:35:38.0597 0x3760 volsnap - ok
10:35:38.0597 0x3760 volume - ok
10:35:38.0597 0x3760 vpci - ok
10:35:38.0597 0x3760 vsmraid - ok
10:35:38.0613 0x3760 VSS - ok
10:35:38.0613 0x3760 VSTXRAID - ok
10:35:38.0613 0x3760 vwifibus - ok
10:35:38.0613 0x3760 vwififlt - ok
10:35:38.0613 0x3760 vwifimp - ok
10:35:38.0628 0x3760 W32Time - ok
10:35:38.0628 0x3760 WaaSMedicSvc - ok
10:35:38.0628 0x3760 WacomPen - ok
10:35:38.0628 0x3760 WalletService - ok
10:35:38.0628 0x3760 wanarp - ok
10:35:38.0644 0x3760 wanarpv6 - ok
10:35:38.0644 0x3760 WarpJITSvc - ok
10:35:38.0644 0x3760 wbengine - ok
10:35:38.0644 0x3760 WbioSrvc - ok
10:35:38.0644 0x3760 wcifs - ok
10:35:38.0644 0x3760 Wcmsvc - ok
10:35:38.0660 0x3760 wcncsvc - ok
10:35:38.0660 0x3760 wcnfs - ok
10:35:38.0660 0x3760 WdBoot - ok
10:35:38.0660 0x3760 Wdf01000 - ok
10:35:38.0660 0x3760 WdFilter - ok
10:35:38.0675 0x3760 WdiServiceHost - ok
10:35:38.0675 0x3760 WdiSystemHost - ok
10:35:38.0675 0x3760 wdiwifi - ok
10:35:38.0675 0x3760 WdmCompanionFilter - ok
10:35:38.0675 0x3760 WdNisDrv - ok
10:35:38.0691 0x3760 WdNisSvc - ok
10:35:38.0691 0x3760 WebClient - ok
10:35:38.0691 0x3760 Wecsvc - ok
10:35:38.0691 0x3760 WEPHOSTSVC - ok
10:35:38.0691 0x3760 wercplsupport - ok
10:35:38.0706 0x3760 WerSvc - ok
10:35:38.0706 0x3760 WFDSConMgrSvc - ok
10:35:38.0706 0x3760 WFPLWFS - ok
10:35:38.0706 0x3760 WiaRpc - ok
10:35:38.0706 0x3760 WIMMount - ok
10:35:38.0722 0x3760 WinDefend - ok
10:35:38.0722 0x3760 WindowsTrustedRT - ok
10:35:38.0722 0x3760 WindowsTrustedRTProxy - ok
10:35:38.0722 0x3760 WinHttpAutoProxySvc - ok
10:35:38.0722 0x3760 WinMad - ok
10:35:38.0738 0x3760 Winmgmt - ok
10:35:38.0738 0x3760 WinNat - ok
10:35:38.0738 0x3760 WinRM - ok
10:35:38.0753 0x3760 WINUSB - ok
10:35:38.0769 0x3760 WinVerbs - ok
10:35:38.0769 0x3760 wisvc - ok
10:35:38.0769 0x3760 WlanSvc - ok
10:35:38.0769 0x3760 wlidsvc - ok
10:35:38.0769 0x3760 wlpasvc - ok
10:35:38.0785 0x3760 WManSvc - ok
10:35:38.0785 0x3760 WmiAcpi - ok
10:35:38.0785 0x3760 wmiApSrv - ok
10:35:38.0785 0x3760 WMIRegistrationService - ok
10:35:38.0785 0x3760 WMPNetworkSvc - ok
10:35:38.0800 0x3760 Wof - ok
10:35:38.0800 0x3760 workfolderssvc - ok
10:35:38.0800 0x3760 WpcMonSvc - ok
10:35:38.0816 0x3760 WPDBusEnum - ok
10:35:38.0816 0x3760 WpdUpFltr - ok
10:35:38.0816 0x3760 WpnService - ok
10:35:38.0816 0x3760 WpnUserService - ok
10:35:38.0832 0x3760 ws2ifsl - ok
10:35:38.0832 0x3760 wscsvc - ok
10:35:38.0847 0x3760 WSearch - ok
10:35:38.0847 0x3760 wuauserv - ok
10:35:38.0847 0x3760 WudfPf - ok
10:35:38.0847 0x3760 WUDFRd - ok
10:35:38.0863 0x3760 WUDFWpdFs - ok
10:35:38.0863 0x3760 WUDFWpdMtp - ok
10:35:38.0863 0x3760 WwanSvc - ok
10:35:38.0863 0x3760 XblAuthManager - ok
10:35:38.0878 0x3760 XblGameSave - ok
10:35:38.0878 0x3760 xboxgip - ok
10:35:38.0878 0x3760 XboxGipSvc - ok
10:35:38.0878 0x3760 XboxNetApiSvc - ok
10:35:38.0878 0x3760 xinputhid - ok
10:35:38.0894 0x3760 ================ Scan global ===============================
10:35:38.0894 0x3760 [Global] - ok
10:35:38.0894 0x3760 ================ Scan MBR ==================================
10:35:38.0894 0x3760 [5FB38429D5D77768867C76DCBDB35194] \Device\Harddisk0\DR0
10:35:38.0910 0x3760 \Device\Harddisk0\DR0 - ok
10:35:38.0910 0x3760 ================ Scan VBR ==================================
10:35:38.0910 0x3760 [AD359F595BA7A46A997DA10B78668FE6] \Device\Harddisk0\DR0\Partition1
10:35:38.0910 0x3760 \Device\Harddisk0\DR0\Partition1 - ok
10:35:38.0910 0x3760 [9D3F6E84AC8D09E5FCBA5CC456916AD2] \Device\Harddisk0\DR0\Partition2
10:35:38.0910 0x3760 \Device\Harddisk0\DR0\Partition2 - ok
10:35:38.0910 0x3760 [606D97A17AD1A961C1AC514FDEEEAD3E] \Device\Harddisk0\DR0\Partition3
10:35:38.0910 0x3760 \Device\Harddisk0\DR0\Partition3 - ok
10:35:38.0910 0x3760 [53672D6AF5B8412AE38D283A3322B146] \Device\Harddisk0\DR0\Partition4
10:35:38.0910 0x3760 \Device\Harddisk0\DR0\Partition4 - ok
10:35:38.0910 0x3760 [3DA5EB162ED0A4BAB9A21A651E3C43AA] \Device\Harddisk0\DR0\Partition5
10:35:38.0910 0x3760 \Device\Harddisk0\DR0\Partition5 - ok
10:35:38.0910 0x3760 ================ Scan active images ========================
10:35:38.0910 0x3760 ================ Scan generic autorun ======================
10:35:38.0910 0x3760 SecurityHealth - ok
10:35:38.0910 0x3760 OneDriveSetup - ok
10:35:38.0910 0x3760 OneDriveSetup - ok
10:35:38.0910 0x3760 OneDrive - ok
10:35:38.0910 0x3760 meViaHkfwQS - ok
10:35:38.0910 0x3760 lxkvpGkIvwjaZo - ok
10:35:38.0925 0x3760 tTSYKmmSzn - ok
10:35:38.0925 0x3760 gZRWYdanKFZ - ok
10:35:38.0925 0x3760 raxlAyfKfi - ok
10:35:38.0925 0x3760 FnyQPRdkza - ok
10:35:38.0925 0x3760 JNELcdTxFPco - ok
10:35:38.0925 0x3760 ZHOnMXgrvNrTu - ok
10:35:38.0925 0x3760 EhNtcQdWIYxvPZ - ok
10:35:38.0925 0x3760 lQBHsGfAXt - ok
10:35:38.0925 0x3760 liWTBxiwng - ok
10:35:38.0925 0x3760 JyrKyOZzFV - ok
10:35:38.0925 0x3760 CNIdVXRRouMbbv - ok
10:35:38.0925 0x3760 rfXfQvbcxLJv - ok
10:35:38.0925 0x3760 SGRoXyWOmfH - ok
10:35:38.0925 0x3760 GAmGPZdOHuPB - ok
10:35:38.0925 0x3760 sATQaoACYdiAhOK - ok
10:35:38.0925 0x3760 VRdJCjHxuwF - ok
10:35:38.0925 0x3760 vOwdpdxecjaG - ok
10:35:38.0925 0x3760 jVtbKSAeqFv - ok
10:35:39.0010 0x3760 AV detected via SS2: Malwarebytes, C:\Program Files\Malwarebytes\Anti-Malware\MBAMWsc.exe ( 3.0.0.225 ), 0x61000 ( enabled : updated )
10:35:39.0010 0x3760 AV detected via SS2: Windows Defender, windowsdefender:// ( ), 0x60100 ( disabled : updated )
10:35:39.0010 0x3760 AV detected via SS2: Avira Security, \\?\C:\Program Files\Avira\Endpoint Protection SDK\wsc_agent.exe ( 1.0.2212.255 ), 0x41000 ( enabled : updated )
10:35:39.0010 0x3760 FW detected via SS2: Avira Security, C:\Program Files\Avira\Endpoint Protection SDK\wsc_remediation.exe ( 1.0.2212.275 ), 0x41000 ( enabled )
10:35:39.0120 0x3760 ============================================================
10:35:39.0120 0x3760 Scan finished
10:35:39.0120 0x3760 ============================================================
10:35:39.0132 0x0694 Detected object count: 0
10:35:39.0132 0x0694 Actual detected object count: 0
```
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [30 Diciembre, 2022 10:52 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/23 "2022-12-30T10:52:20Z")
```auto
Malwarebytes Anti-Rootkit BETA 1.10.3.1001
www.malwarebytes.org
Database version:
main: v2022.12.30.01
rootkit: v2022.12.30.01
Windows 10 x64 NTFS
Internet Explorer 11.789.19041.0
mmuno :: LAPTOP-HKJ5OOUL [administrator]
30/12/2022 11:41:05
mbar-log-2022-12-30 (11-41-05).txt
Scan type: Quick scan
Scan options enabled: Anti-Rootkit | Drivers | MBR | Physical Sectors | Memory | Startup | Registry | File System | Heuristics/Extra | Heuristics/Shuriken
Scan options disabled:
Objects scanned: 168603
Time elapsed: 8 minute(s), 26 second(s)
Memory Processes Detected: 0
(No malicious items detected)
Memory Modules Detected: 0
(No malicious items detected)
Registry Keys Detected: 0
(No malicious items detected)
Registry Values Detected: 0
(No malicious items detected)
Registry Data Items Detected: 0
(No malicious items detected)
Folders Detected: 0
(No malicious items detected)
Files Detected: 0
(No malicious items detected)
Physical Sectors Detected: 0
(No malicious items detected)
(end)
```
```auto
---------------------------------------
Malwarebytes Anti-Rootkit BETA 1.10.3.1001
(c) Malwarebytes Corporation 2011-2012
OS version: 10.0.9200 Windows 10 x64
Account is Administrative
Internet Explorer version: 11.789.19041.0
File system is: NTFS
Disk drives: C:\ DRIVE_FIXED
CPU speed: 2.419000 GHz
Memory total: 8269565952, free: 3120283648
Downloaded database version: v2022.12.30.01
Downloaded database version: v2022.12.30.01
Downloaded database version: v2018.01.20.01
=======================================
Initializing...
Driver version: 4.3.0.15
------------ Kernel report ------------
12/30/2022 11:41:01
------------ Loaded modules -----------
\SystemRoot\system32\ntoskrnl.exe
\SystemRoot\system32\hal.dll
\SystemRoot\system32\kd.dll
\SystemRoot\system32\mcupdate_GenuineIntel.dll
\SystemRoot\System32\drivers\CLFS.SYS
\SystemRoot\System32\drivers\tm.sys
\SystemRoot\system32\PSHED.dll
\SystemRoot\system32\BOOTVID.dll
\SystemRoot\System32\drivers\FLTMGR.SYS
\SystemRoot\System32\drivers\msrpc.sys
\SystemRoot\System32\drivers\ksecdd.sys
\SystemRoot\System32\drivers\clipsp.sys
\SystemRoot\System32\drivers\cmimcext.sys
\SystemRoot\System32\drivers\werkernel.sys
\SystemRoot\System32\drivers\ntosext.sys
\SystemRoot\system32\CI.dll
\SystemRoot\System32\drivers\cng.sys
\SystemRoot\system32\drivers\Wdf01000.sys
\SystemRoot\system32\drivers\WDFLDR.SYS
\SystemRoot\system32\drivers\WppRecorder.sys
\SystemRoot\system32\drivers\SleepStudyHelper.sys
\SystemRoot\System32\Drivers\acpiex.sys
\SystemRoot\system32\drivers\SgrmAgent.sys
\SystemRoot\System32\drivers\ACPI.sys
\SystemRoot\System32\drivers\WMILIB.SYS
\SystemRoot\System32\drivers\msisadrv.sys
\SystemRoot\System32\drivers\pci.sys
\SystemRoot\System32\drivers\tpm.sys
\SystemRoot\System32\drivers\intelpep.sys
\SystemRoot\system32\drivers\WindowsTrustedRT.sys
\SystemRoot\System32\drivers\IntelTA.sys
\SystemRoot\System32\drivers\WindowsTrustedRTProxy.sys
\SystemRoot\system32\drivers\84157072.sys
\SystemRoot\System32\drivers\pcw.sys
\SystemRoot\System32\drivers\vdrvroot.sys
\SystemRoot\system32\drivers\ucx01000.sys
\SystemRoot\system32\drivers\pdc.sys
\SystemRoot\system32\drivers\CEA.sys
\SystemRoot\System32\drivers\partmgr.sys
\SystemRoot\System32\drivers\spaceport.sys
\SystemRoot\System32\drivers\volmgr.sys
\SystemRoot\System32\drivers\sdbus.sys
\SystemRoot\System32\drivers\volmgrx.sys
\SystemRoot\system32\drivers\urscx01000.sys
\SystemRoot\System32\drivers\mountmgr.sys
\SystemRoot\System32\drivers\iaStorVD.sys
\SystemRoot\System32\drivers\storport.sys
\SystemRoot\System32\drivers\EhStorClass.sys
\SystemRoot\System32\drivers\fileinfo.sys
\SystemRoot\System32\Drivers\Wof.sys
\SystemRoot\System32\Drivers\Ntfs.sys
\SystemRoot\System32\drivers\usbccgp.sys
\SystemRoot\System32\drivers\USBD.SYS
\SystemRoot\System32\DriverStore\FileRepository\urschipidea.inf_amd64_78ad1c14e33df968\urschipidea.sys
\SystemRoot\System32\drivers\usbhub.sys
\SystemRoot\System32\drivers\UsbHub3.sys
\SystemRoot\System32\drivers\usbehci.sys
\SystemRoot\System32\drivers\USBPORT.SYS
\SystemRoot\System32\Drivers\Fs_Rec.sys
\SystemRoot\system32\drivers\ndis.sys
\SystemRoot\system32\drivers\NETIO.SYS
\SystemRoot\System32\Drivers\ksecpkg.sys
\SystemRoot\System32\drivers\tcpip.sys
\SystemRoot\System32\drivers\fwpkclnt.sys
\SystemRoot\System32\drivers\wfplwfs.sys
\SystemRoot\system32\DRIVERS\BdNet.sys
\SystemRoot\System32\DRIVERS\fvevol.sys
\SystemRoot\System32\drivers\volume.sys
\SystemRoot\System32\drivers\volsnap.sys
\SystemRoot\System32\drivers\USBXHCI.SYS
\SystemRoot\System32\drivers\USBSTOR.SYS
\SystemRoot\System32\drivers\uaspstor.sys
\SystemRoot\System32\drivers\sdstor.sys
\SystemRoot\System32\drivers\rdyboost.sys
\SystemRoot\System32\Drivers\mup.sys
\SystemRoot\system32\drivers\iorate.sys
\SystemRoot\System32\drivers\disk.sys
\SystemRoot\System32\drivers\CLASSPNP.SYS
\SystemRoot\System32\Drivers\crashdmp.sys
\SystemRoot\system32\Drivers\RtsUer.sys
\SystemRoot\System32\DriverStore\FileRepository\ibtusb.inf_amd64_11ac98f8e99ac5f5\ibtusb.sys
\SystemRoot\System32\drivers\cdrom.sys
\SystemRoot\System32\drivers\BTHUSB.sys
\SystemRoot\system32\drivers\filecrypt.sys
\SystemRoot\system32\drivers\tbs.sys
\SystemRoot\System32\drivers\BTHport.sys
\SystemRoot\system32\DRIVERS\BdSentry.sys
\SystemRoot\System32\Drivers\Null.SYS
\SystemRoot\System32\Drivers\Beep.SYS
\SystemRoot\System32\drivers\dxgkrnl.sys
\SystemRoot\System32\drivers\watchdog.sys
\SystemRoot\System32\DriverStore\FileRepository\basicdisplay.inf_amd64_fc93ae411c02f280\BasicDisplay.sys
\SystemRoot\System32\Drivers\usbvideo.sys
\SystemRoot\System32\Drivers\ks.sys
\SystemRoot\system32\drivers\ksthunk.sys
\SystemRoot\System32\DriverStore\FileRepository\basicrender.inf_amd64_ed345fdc37d65139\BasicRender.sys
\SystemRoot\System32\Drivers\Npfs.SYS
\SystemRoot\System32\Drivers\Msfs.SYS
\SystemRoot\System32\Drivers\CimFS.SYS
\SystemRoot\system32\DRIVERS\tdx.sys
\SystemRoot\system32\DRIVERS\TDI.SYS
\SystemRoot\System32\drivers\netprotection_network_filter.sys
\SystemRoot\System32\DRIVERS\netbt.sys
\SystemRoot\System32\drivers\rfcomm.sys
\SystemRoot\system32\drivers\afunix.sys
\SystemRoot\System32\drivers\BthEnum.sys
\SystemRoot\system32\drivers\afd.sys
\SystemRoot\System32\drivers\bthpan.sys
\SystemRoot\System32\drivers\vwififlt.sys
\SystemRoot\System32\drivers\Microsoft.Bluetooth.Legacy.LEEnumerator.sys
\SystemRoot\System32\drivers\pacer.sys
\SystemRoot\System32\drivers\ndiscap.sys
\SystemRoot\system32\drivers\netbios.sys
\SystemRoot\System32\drivers\Vid.sys
\SystemRoot\System32\drivers\winhvr.sys
\SystemRoot\system32\DRIVERS\rtp_process_monitor.sys
\SystemRoot\system32\DRIVERS\rtp_traverse.sys
\SystemRoot\system32\DRIVERS\rdbss.sys
\SystemRoot\system32\drivers\nsiproxy.sys
\SystemRoot\System32\drivers\npsvctrig.sys
\SystemRoot\System32\drivers\mssmbios.sys
\SystemRoot\System32\drivers\gpuenergydrv.sys
\SystemRoot\System32\Drivers\dfsc.sys
\SystemRoot\system32\drivers\dam.sys
\SystemRoot\System32\Drivers\fastfat.SYS
\SystemRoot\system32\drivers\bam.sys
\SystemRoot\System32\DriverStore\FileRepository\asussci2.inf_amd64_aeff025f0108fb44\ASUSOptimization\AsusWmiAcpi.sys
\SystemRoot\system32\DRIVERS\ahcache.sys
\SystemRoot\System32\DriverStore\FileRepository\compositebus.inf_amd64_7500cffa210c6946\CompositeBus.sys
\SystemRoot\System32\drivers\kdnic.sys
\SystemRoot\System32\DriverStore\FileRepository\umbus.inf_amd64_b78a9c5b6fd62c27\umbus.sys
\SystemRoot\System32\drivers\CAD.sys
\SystemRoot\System32\DriverStore\FileRepository\iigd_dch.inf_amd64_89b1ad385fab2e0b\igdkmdn64.sys
\SystemRoot\System32\DriverStore\FileRepository\gna.inf_amd64_689d3d5fefeef458\gna.sys
\SystemRoot\System32\drivers\Netwtw10.sys
\SystemRoot\system32\DRIVERS\wdiwifi.sys
\SystemRoot\System32\drivers\vwifibus.sys
\SystemRoot\System32\DriverStore\FileRepository\ialpss2_i2c_tgl.inf_amd64_ab87bf17a571e523\iaLPSS2_I2C_TGL.sys
\SystemRoot\system32\drivers\SpbCx.sys
\SystemRoot\System32\DriverStore\FileRepository\heci.inf_amd64_b3a92646bfdb3e11\x64\TeeDriverW10x64.sys
\SystemRoot\System32\DriverStore\FileRepository\ialpss2_uart2_tgl.inf_amd64_1a8e964d43720594\iaLPSS2_UART2_TGL.sys
\SystemRoot\system32\drivers\SerCx2.sys
\SystemRoot\System32\DriverStore\FileRepository\ialpss2_spi_tgl.inf_amd64_b6ea3d48ee329530\iaLPSS2_SPI_TGL.sys
\SystemRoot\System32\drivers\CmBatt.sys
\SystemRoot\System32\drivers\BATTC.SYS
\SystemRoot\System32\DriverStore\FileRepository\dptf_acpi.inf_amd64_a5bac3087ca5f8d5\dptf_acpi.sys
\SystemRoot\System32\drivers\i8042prt.sys
\SystemRoot\System32\drivers\kbdclass.sys
\SystemRoot\System32\DriverStore\FileRepository\intcaudiobus.inf_amd64_f391fa5ae776e58c\IntcAudioBus.sys
\SystemRoot\System32\drivers\portcls.sys
\SystemRoot\System32\drivers\drmk.sys
\SystemRoot\System32\drivers\acpitime.sys
\SystemRoot\System32\DriverStore\FileRepository\ialpss2_gpio2_tgl.inf_amd64_d0e63c4e3754f42f\iaLPSS2_GPIO2_TGL.sys
\SystemRoot\System32\Drivers\msgpioclx.sys
\SystemRoot\System32\drivers\intelppm.sys
\SystemRoot\System32\drivers\acpipagr.sys
\SystemRoot\System32\drivers\wmiacpi.sys
\SystemRoot\System32\DriverStore\FileRepository\uefi.inf_amd64_c1628ffa62c8e54c\UEFI.sys
\SystemRoot\System32\drivers\NdisVirtualBus.sys
\SystemRoot\System32\DriverStore\FileRepository\swenum.inf_amd64_16a14542b63c02af\swenum.sys
\SystemRoot\System32\drivers\rdpbus.sys
\SystemRoot\System32\drivers\hidi2c.sys
\SystemRoot\System32\drivers\mshidkmdf.sys
\SystemRoot\System32\drivers\HIDCLASS.SYS
\SystemRoot\System32\drivers\HIDPARSE.SYS
\SystemRoot\System32\DriverStore\FileRepository\intcoed.inf_amd64_06dd582276d3f601\IntcOED.sys
\SystemRoot\System32\drivers\mouhid.sys
\SystemRoot\System32\drivers\mouclass.sys
\SystemRoot\System32\drivers\AsusPTPFilter.sys
\SystemRoot\System32\drivers\MTConfig.sys
\SystemRoot\system32\drivers\RTKVHD64.sys
\SystemRoot\System32\DriverStore\FileRepository\intcusb.inf_amd64_d97909364d9908a5\IntcUSB.sys
\SystemRoot\System32\DriverStore\FileRepository\intcbtau.inf_amd64_50d2fa7560d030fc\IntcBTAu.sys
\SystemRoot\System32\Drivers\dump_diskdump.sys
\SystemRoot\System32\win32k.sys
\SystemRoot\System32\drivers\dump_iaStorVD.sys
\SystemRoot\System32\Drivers\dump_dumpfve.sys
\SystemRoot\System32\win32kbase.sys
\SystemRoot\System32\win32kfull.sys
\SystemRoot\System32\drivers\dxgmms2.sys
\SystemRoot\System32\drivers\monitor.sys
\SystemRoot\System32\cdd.dll
\SystemRoot\System32\drivers\WUDFRd.sys
\SystemRoot\System32\DriverStore\FileRepository\dptf_cpu.inf_amd64_e3868713e3d137ef\dptf_cpu.sys
\SystemRoot\System32\DriverStore\FileRepository\dptf_cpu.inf_amd64_e3868713e3d137ef\esif_lf.sys
\SystemRoot\system32\drivers\mmcss.sys
\SystemRoot\system32\drivers\luafv.sys
\SystemRoot\system32\drivers\wcifs.sys
\SystemRoot\system32\drivers\cldflt.sys
\SystemRoot\system32\drivers\storqosflt.sys
\SystemRoot\system32\DRIVERS\rtp_filesystem_filter.sys
\SystemRoot\System32\Drivers\MbamChameleon.sys
\SystemRoot\system32\drivers\bindflt.sys
\SystemRoot\system32\drivers\lltdio.sys
\SystemRoot\system32\drivers\mslldp.sys
\SystemRoot\system32\drivers\rspndr.sys
\SystemRoot\System32\DRIVERS\wanarp.sys
\SystemRoot\system32\drivers\ndisuio.sys
\SystemRoot\system32\DRIVERS\nwifi.sys
\SystemRoot\system32\drivers\msquic.sys
\SystemRoot\system32\drivers\HTTP.sys
\SystemRoot\System32\drivers\condrv.sys
\SystemRoot\system32\DRIVERS\bowser.sys
\SystemRoot\System32\drivers\mpsdrv.sys
\SystemRoot\system32\DRIVERS\mrxsmb.sys
\SystemRoot\system32\DRIVERS\mrxsmb20.sys
\SystemRoot\System32\DRIVERS\srvnet.sys
\SystemRoot\System32\DRIVERS\srv2.sys
\SystemRoot\System32\drivers\vwifimp.sys
\SystemRoot\system32\drivers\Ndu.sys
\SystemRoot\system32\drivers\peauth.sys
\SystemRoot\System32\drivers\tcpipreg.sys
\SystemRoot\System32\drivers\rassstp.sys
\SystemRoot\System32\DRIVERS\NDProxy.sys
\SystemRoot\System32\drivers\AgileVpn.sys
\SystemRoot\System32\drivers\rasl2tp.sys
\SystemRoot\System32\drivers\raspptp.sys
\SystemRoot\System32\drivers\raspppoe.sys
\SystemRoot\System32\DRIVERS\ndistapi.sys
\SystemRoot\System32\drivers\ndiswan.sys
\SystemRoot\System32\DriverStore\FileRepository\asussci2.inf_amd64_aeff025f0108fb44\ASUSSystemAnalysis\AsusSAIO.sys
\SystemRoot\System32\Drivers\mbamswissarmy.sys
\SystemRoot\system32\DRIVERS\mwac.sys
\SystemRoot\system32\DRIVERS\farflt.sys
\??\C:\Windows\system32\drivers\mbae64.sys
\??\C:\Windows\system32\DRIVERS\mbam.sys
\??\C:\Windows\system32\drivers\3415A2F2.sys
----------- End -----------
Done!
Scan started
Database versions:
main: v2022.12.30.01
rootkit: v2022.12.30.01
<<<2>>>
Physical Sector Size: 512
Drive: 0, DevicePointer: 0xffffbc05c8be5060, DeviceName: \Device\Harddisk0\DR0\, DriverName: \Driver\disk\
--------- Disk Stack ------
DevicePointer: 0xffffbc05c8be4850, DeviceName: Unknown, DriverName: \Driver\partmgr\
DevicePointer: 0xffffbc05c8be5060, DeviceName: \Device\Harddisk0\DR0\, DriverName: \Driver\disk\
DevicePointer: 0xffffbc05c67694d0, DeviceName: Unknown, DriverName: \Driver\ACPI\
DevicePointer: 0xffffbc05c885a050, DeviceName: \Device\0000003b\, DriverName: \Driver\iaStorVD\
------------ End ----------
Alternate DeviceName: \Device\Harddisk0\DR0\, DriverName: \Driver\disk\
Upper DeviceData: 0x0, 0x0, 0x0
Lower DeviceData: 0x0, 0x0, 0x0
<<<3>>>
Volume: C:
Volume is encrypted by BITLOCKER
<<<2>>>
<<<3>>>
Volume: C:
Volume is encrypted by BITLOCKER
Scanning drivers directory: C:\WINDOWS\SYSTEM32\drivers...
Done!
Drive 0
This is a System drive
Scanning MBR on drive 0...
Inspecting partition table:
This drive is a GPT Drive.
MBR Signature: 55AA
Disk Signature: 4541F0F0
GPT Protective MBR Partition information:
Partition 0 type is EFI-GPT (0xee)
Partition is NOT ACTIVE.
Partition starts at LBA: 1 Numsec = 4294967295
Partition 1 type is Empty (0x0)
Partition is NOT ACTIVE.
Partition starts at LBA: 0 Numsec = 0
Partition 2 type is Empty (0x0)
Partition is NOT ACTIVE.
Partition starts at LBA: 0 Numsec = 0
Partition 3 type is Empty (0x0)
Partition is NOT ACTIVE.
Partition starts at LBA: 0 Numsec = 0
GPT Partition information:
GPT Header Signature 4546492050415254
GPT Header Revision 65536 Size 92 CRC 436170969
GPT Header CurrentLba = 1 BackupLba 500118191
GPT Header FirstUsableLba 34 LastUsableLba 500118158
GPT Header Guid a4ff8158-38a4-4f75-8439-f45efb2a3f60
GPT Header Contains 128 partition entries starting at LBA 2
GPT Header Partition entry size = 128
Backup GPT header Signature 4546492050415254
Backup GPT header Revision 65536 Size 92 CRC 436170969
Backup GPT header CurrentLba = 500118191 BackupLba 1
Backup GPT header FirstUsableLba 34 LastUsableLba 500118158
Backup GPT header Guid a4ff8158-38a4-4f75-8439-f45efb2a3f60
Backup GPT header Contains 128 partition entries starting at LBA 500118159
Backup GPT header Partition entry size = 128
Partition 0 Type c12a7328-f81f-11d2-ba4b-0a0c93ec93b
Partition ID c0244d3c-7047-4557-b8fd-d7e08ae932ea
FirstLBA 2048 Last LBA 534527
Attributes 0
Partition Name EFI system partition
GPT Partition 0 is bootable
Partition 1 Type e3c9e316-b5c-4db8-817d-f92df0215ae
Partition ID f5b4a8d3-45ea-428f-ace3-989010ee28f6
FirstLBA 534528 Last LBA 567295
Attributes 0
Partition Name Microsoft reserved partition
Partition 2 Type ebd0a0a2-b9e5-4433-87c0-68b6b72699c7
Partition ID 52346628-49b-4f6a-8026-80c5d9dd79e0
FirstLBA 567296 Last LBA 497556110
Attributes 0
Partition Name Basic data partition
Partition 3 Type de94bba4-6d1-4d40-a16a-bfd5179d6ac
Partition ID ec93e60d-7e63-45cb-a7ff-76d9949274c
FirstLBA 497557504 Last LBA 499707903
Attributes 1
Partition Name Basic data partition
Partition 4 Type de94bba4-6d1-4d40-a16a-bfd5179d6ac
Partition ID 395578c9-889e-42bc-b23f-f30cc974db1
FirstLBA 499707904 Last LBA 500117503
Attributes 1
Partition Name Basic data partition
Disk Size: 256060514304 bytes
Sector size: 512 bytes
Done!
Scan finished
=======================================
Removal queue found; removal started
Removing C:\ProgramData\Malwarebytes' Anti-Malware (portable)\MBR-0-i.mbam...
Removing C:\ProgramData\Malwarebytes' Anti-Malware (portable)\MBR-0-r.mbam...
Removal finished
```
---
### Author:  [@JCTecn1cal](https://forospyware.com/u/JCTecn1cal)
#### Post date: [30 Diciembre, 2022 19:15 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/24 "2022-12-30T19:15:50Z")
Ahora nos toca usar estas herramientas para remover las trazas de adware y corregir los navegadores
- [ZHPCleaner](https://www.infospyware.com/antispyware/zhpcleaner/)
- [AdwCleaner](https://www.infospyware.com/antispyware/adwcleaner/)
Vamos a repetir el procedimiento anterior, **mantendremos el antivirus deshabilitado** Con todos los programas y ventanas cerradas **incluyendo los navegadores** vamos a ejecutar cada una de las herramientas como administrador
Si al ejecutar algún programa, **cualquiera que te indiquemos** , aparece una ventana como esta 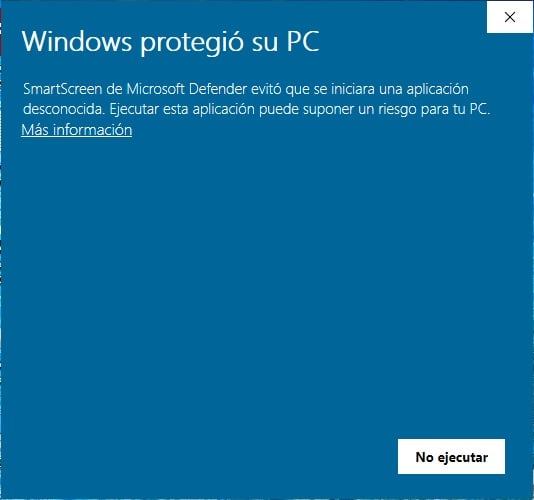
Haces clic en **Mas información** y luego haces clic en **Ejecutar de todas formas**
Ejecuta ZHPCleaner **Clic derecho y Seleccionar Ejecutar como Administrador"** Cuando se abra la ventana Principal
Tienes que hacer lo siguiente:
- Haces Clic en **Scanner** para realizar el análisis y esperar a que este se termine.
- Cuando el análisis se haya terminado, se abrira una ventana, **solo tienes que cerrarla**
- Haces clic en **Reparar** para eliminar todas las amenazas que la herramienta haya encontrado Probablemente se abra otra ventana con el reporte de la limpieza o reparación
- Si haces clic en el botón **Informe** veras el reporte de la herramienta
Es muy probable que veas dos archivos de texto en el escritorio
- **ZHPCleaner (S).txt** Este es creado por la opción **Scanner** y solo muestra lo que ZHPCleaner ha encontrado
- **ZHPCleaner (R).txt** Este es el reporte que nos interesa, **pues este el reporte de la opción Reparar** y nos muestra las acciones realizadas por la herramienta
Ejecuta AdwCleaner Clic derecho y Seleccionar **“Ejecutar como Administrador”** Después de aceptar el acuerdo, veras la ventana Principal, haces clic en **Analizar ahora** para empezar el escaneo. Cuando termine el análisis pueden ocurrir dos cosas
- Si detecto algo,te mostrara las detecciones y tu debes hacer clic en **Cuarentena** para Eliminar todo lo encontrado
- Si no encontró nada, haces clic en **Omitir reparación básica**
No reinicies el equipo , al menos que ADwCleaner te lo pida como parte de la limpieza, cuando termine se abrirá el reporte que debes traer la próxima vez que respondas **## Informes**
Después de **Reiniciar** se abrirá un reporte. Si está recibiendo ayuda en el **Foro InfoSpyware** copie y pegue el reporte en el tema.
En la pestaña **Informes** del panel también puede encontrar los reportes de análisis y limpieza. En la siguiente imagen se pueden ver los informes.
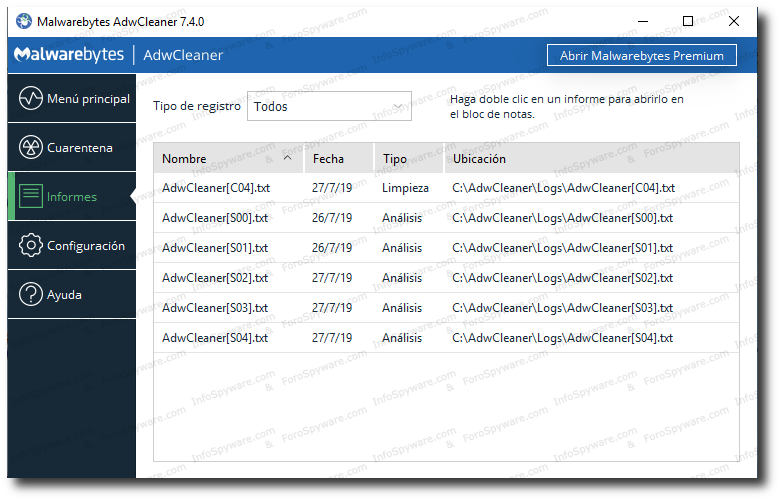
El reporte que tienes que traer es de tipo **Limpieza**
Cuando repondas nos traes los reportes de **Limpieza de AdwCleaner** y **El reporte de Reparación de ZHPCleaner**
Saludos
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [2 Enero, 2023 10:40 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/25 "2023-01-02T10:40:18Z")
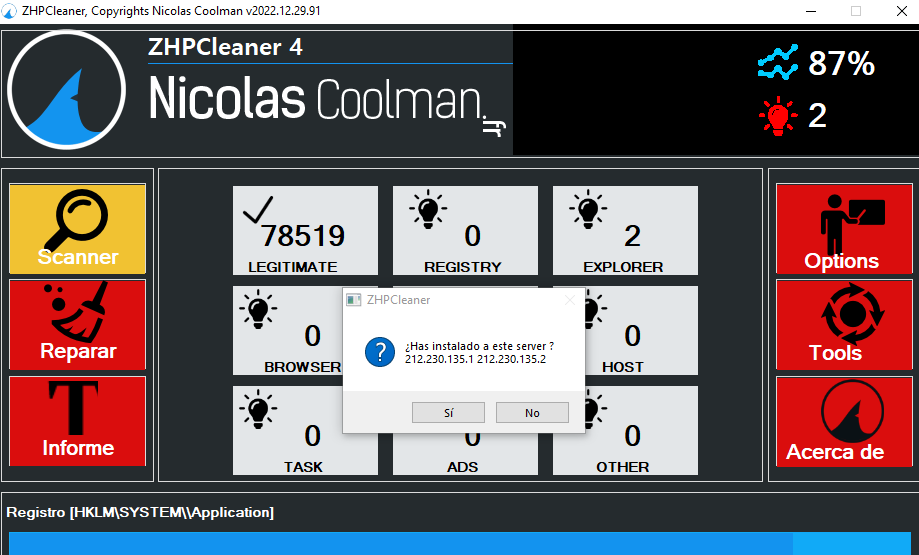Cuando estaba haciendo el scaneo me salió este mensaje, lo dejo aquí por si es importante.
```auto
~ ZHPCleaner v2022.12.29.91 by Nicolas Coolman (2022/12/29)
~ Run by mmuno (Administrator) (02/01/2023 11:28:57)
~ Web: https://www.nicolascoolman.com
~ Blog: https://nicolascoolman.eu/
~ Facebook : https://www.facebook.com/nicolascoolman1
~ State version : Version OK
~ Certificate ZHPCleaner: Legal
~ Type : Reparar
~ Report : C:\Users\mmuno\Desktop\ZHPCleaner (R).txt
~ Quarantine : C:\Users\mmuno\AppData\Roaming\ZHP\ZHPCleaner_Reg.txt
~ UAC : Activate
~ Boot Mode : Normal (Normal boot)
Windows 10 Home, 64-bit (Build 19044)
---\ Alternate Data Stream (ADS). (0)
~ No malintencionados o innecesarios artículos encontrados. (ADS)
---\ Servicios (0)
~ No malintencionados o innecesarios artículos encontrados. (Servicio)
---\ Navegadores de Internet (0)
~ No malintencionados o innecesarios artículos encontrados. (Navegador)
---\ Hosts carpeta (1)
~ El archivo hosts es legítimo (21)
---\ Tareas automáticas programadas. (0)
~ No malintencionados o innecesarios artículos encontrados. (Tarea)
---\ Explorador ( Archivos, Carpetas ) (2)
MOVIDO carpeta: C:\Users\mmuno\AppData\Local\Google\Chrome\User Data\Default\Preferences =>Préférences Chromium
MOVIDO carpeta: C:\Users\mmuno\AppData\Local\Microsoft\Edge\User Data\Default\Preferences =>Préférences Chromium
---\ Registro ( Claves, Valores, Datos) (2)
BORRADOS dados: HKLM\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\Interfaces\{b3519e78-6e26-4180-bc07-670f1843f02e}\\DhcpNameServer [Bad : 212.230.135.1 212.230.135.2] =>Hijacker.Browser
BORRADOS dados: HKLM\SYSTEM\CurrentControlSet\Services\Tcpip\Parameters\\DhcpNameServer [Bad : 212.230.135.1 212.230.135.2] =>Hijacker.Browser
---\ Resumen de elementos en su estación de trabajo (2)
https://nicolascoolman.eu/forum/Topic/repaquetage-et-infection/ =>Préférences Chromium
https://nicolascoolman.eu/2017/11/10/hijacker-browser-3/ =>Hijacker.Browser
---\ Limpieza adicional. (23)
~ Clave de registro Tracing borrados (23)
~ Quitar los antiguos informes de ZHPCleaner. (0)
---\ Resultado de la reparación.
~ Reparación llevada a cabo con éxito
~ Mozilla Firefox OK
~ Internet Explorer OK
---\ STATISTIQUES
~ Items escaneado : 1480
~ Items encontrado : 0
~ artículos cancelados : 0
~ Ahorro de espacio (bytes) : 0
~ Items opciones : 9/17
---\ OPCIONES NO ACTIVAS
~ Análisis temporal de archivos
~ Análisis temporal de carpetas
~ Análisis de CLSID de carpetas vacías
~ Vaciar otro análisis de carpetas
~ Análisis de carpetas locales vacías
~ Análisis de archivos de instalación obsoleto
~ Iniciar navegadores con extensiones eliminadas
~ End of clean in 00h00mn58s
---\ Reporte (2)
ZHPCleaner-[S]-02012023-11_08_32.txt
ZHPCleaner-[R]-02012023-11_29_55.txt
```
El adwcleaner no me deja descargarlo, me da error cuando le doy a descargar programa.

---
### Author:  [@JCTecn1cal](https://forospyware.com/u/JCTecn1cal)
#### Post date: [2 Enero, 2023 18:53 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/26 "2023-01-02T18:53:45Z")
En el caso de los servers detectados por ZHPCleaner es prudente hacer clic en **No** ya que no estamos totalmente seguros de que programa los este usando, dejamos que los repare y vemos como se comporta el equipo tras la reparación.
Lo del AdwCleaner parece que estuviera saturado y tal vez tengas que intentarlo mas tarde o puedes probar con este enlace hacia su pagina
> **[AdwCleaner - Herramienta gratuita de limpieza y eliminación de adware |...](https://es.malwarebytes.com/adwcleaner/)**
>
> Descargue Malwarebytes AdwCleaner de forma gratuita para eliminar adware, bloatware, barras de herramientas no deseadas y otros programas potencialmente no deseados (PUP) de su PC de Windows.
Me comentas si tienes el mismo problema o si ya lograste descargarlo y ejecutarlo
Saludos
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [3 Enero, 2023 09:39 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/27 "2023-01-03T09:39:28Z")
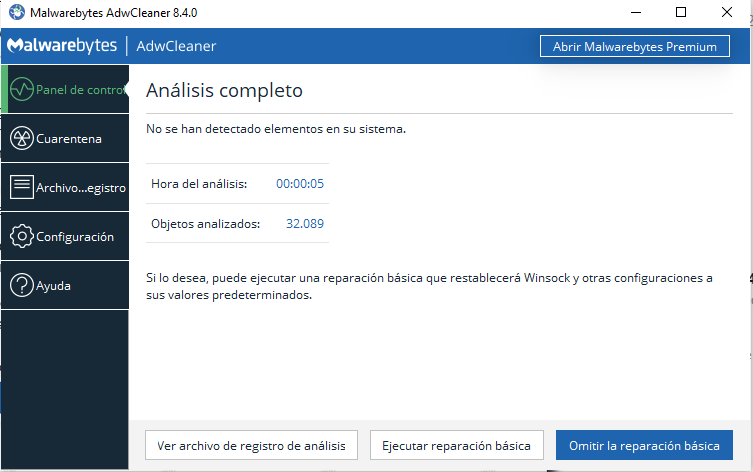
ahora si me ha dejado descargarlo
---
### Author:  [@JCTecn1cal](https://forospyware.com/u/JCTecn1cal)
#### Post date: [4 Enero, 2023 18:38 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/28 "2023-01-04T18:38:24Z")
Si seguiste las instrucciones solo tienes que hacer clic en **Omitir la reparación básica**
Tratandose de ransomwares:
- Cuando la variante es muy nueva y todavía no existe herramienta de descifrado para ella. **Solo nos resta guardar una copia de los archivos cifrados en alguna unidad externa y esperar a que la herramienta de descifrado sea creada**
- En algunos casos el archivo original no es eliminado del equipo y solo esta inaccesible. Pero con herramientas de recuperación como **PhotoRec** entre otras **podemos acceder a este** o por lo menos, **podríamos hallar alguna copia intacta del archivo que fue cifrado**.
Para hacer esto, necesitaremos al compañero @Chicloi que cuenta con las herramientas y manuales para este tipo de programas. Además quisiera que nos confirmara con RogueKiller si el equipo ya esta realmente limpio.
Saludos y esperamos tus comentarios al respecto
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [5 Enero, 2023 02:22 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/29 "2023-01-05T02:22:00Z")
Buenas, soy @Chicloi, como comenta mi compañero @JCTecn1cal, vamos a ver si se puede recuperar las fotos que usted comenta @Bobby1, pero antes voy a proceder a realizarle un proceso de análisis para poder comprobar que su ordenador esté libre de infecciones y de virus en su ordenador.
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [5 Enero, 2023 02:24 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/30 "2023-01-05T02:24:30Z")
Ahora, **realice usted los siguientes pasos a seguir:**
**IMPORTANTE:**
1️⃣ PASALE CADA PROGRAMA **POR SEPARADO** Y HASTA QUE **NO** ACABE EL PRIMER PROGRAMA DE ANALIZAR POR COMPLETO, **SIGUIENDO LAS INDICACIONES DADAS** , **NO** LE PASE EL SIGUIENTE Y **ASÍ CON EL RESTO DE PROGRAMAS.**
2️⃣ DURANTE TODO EL PROCESO DE DESINFECCIÓN DE SU ORDENADOR, QUE **NO** SE APAGUE LA PANTALLA, ES DECIR, QUE SU PANTALLA **NO** SE PONGA EN **ESTADO DE SUSPENSION** YA QUE **PUEDE INTERRUMPIRSE EL PROCESO DE DESINFECCIÓN DE SU ORDENADOR** Y **NO** ELIMINAR LAS AMENAZAS E INFECCIONES QUE ENCUENTRE.
3️⃣ SI LOS PROGRAMAS QUE SE LE INDIQUEN EN ESTE FORO QUE SE LE PASEN A SU ORDENADOR **YA LOS TUVIERA INSTALADOS** , **NO** HACE FALTA **QUE LOS INSTALE DE NUEVO** , SIMPLEMENTE **EJECUTE** EL PROGRAMA QUE SE LE INDIQUE EN ESTE FORO Y SIGA **LAS INDICACINES Y EL MANUAL** QUE SE LE DEJA **JUNTO AL PROGRAMA.**
4️⃣ SI ALGUNO DE LOS PROGRAMA DE LOS QUE **SE LE INDIQUE EN ESTE FORO** , **UNA VEZ FINALIZADO EL PROCESO DE ANALISIS** , LE INDICA QUE DEBE **REINICIAR!** PUES **REINICIE,** **PERO** **SÓLO SI SE LO INDICA DICHO PROGRAMA**.
Ahora ejecutarás una serie de herramientas respetando el orden los pasos **con todos los programas cerrados incluidos los navegadores.**
0️⃣ Descargue el programa de la siguiente Url: Le dejo **“2 Url de Descarga”** por si uno no le funciona el proceso de Instalación pueda probar con la segunda **Url de Descarga:**
**Url descarga 1:** [Click aquí: RogueKiller x64 Bits](https://www.adlice.com/download-start/?app=roguekiller&type=x64)
**Url descarga 2:** [Click aquí: RogueKiller x82 Bits](https://www.adlice.com/download-start/?app=roguekiller&type=x86)
Aquí le dejo su **manual** del: **RogueKiller** **para que sepas cómo utilizarlo y configurarlo correctamente:** Siga usted el siguiente tutorial que le dejo a continuación:
1️⃣ **Abra** el programa: **RogueKiller** que ha descargado.
2️⃣ Clikea en la pestaña que pone: **Analizar.** , click en donde pone: **Análisis Completo (Full Scan)**. **Nota:** Si **NO** le deja realizar un **“Análisis Personalizado”** realice un Análisis **Análisis Completo (Full Scan)** (Tal y cómo se muestra en la imagen):
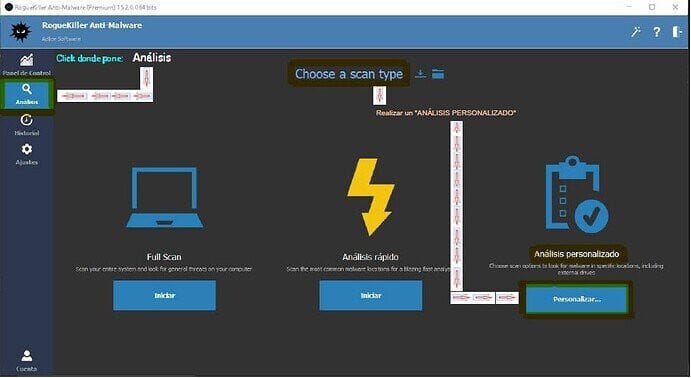
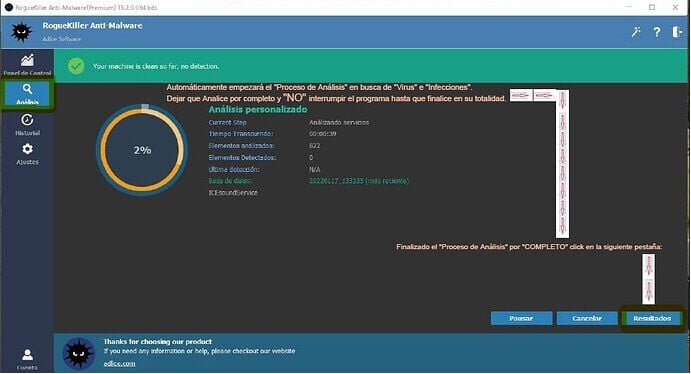
3️⃣ Automáticamente empezará el Proceso de Análisis en busca de **Virus** e **Infecciones** dejar que analice por completo y **NO** interrumpir el programa hasta que finalice en su totalidad. Finalizado el Proceso de Análisis por completo clickea en la pestaña que pone: **Resultados:** (Proceso tal y como se indica en la siguiente pantalla):
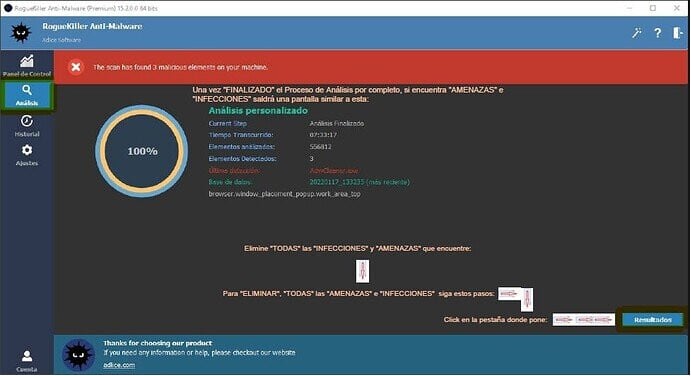
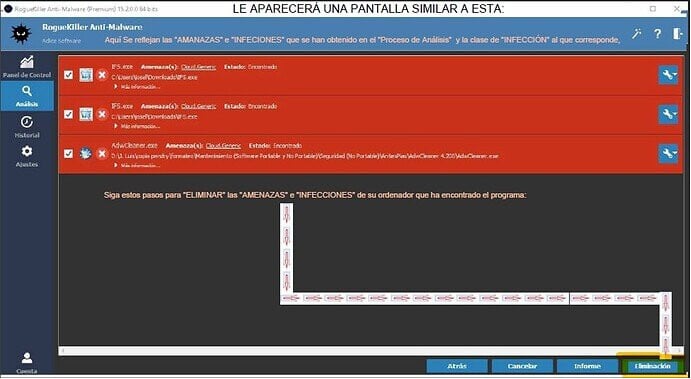
4️⃣ Una vez finalizado el Proceso de Análisis por completo, si encuentra **AMENAZAS** e **INFECCIONES** saldrá una pantalla similar a esta, clicka en la pestaña que pone: **Resultados** para poder eliminar dichas **INFECCIONES.** (Tal y como se muestra en esta pantalla):
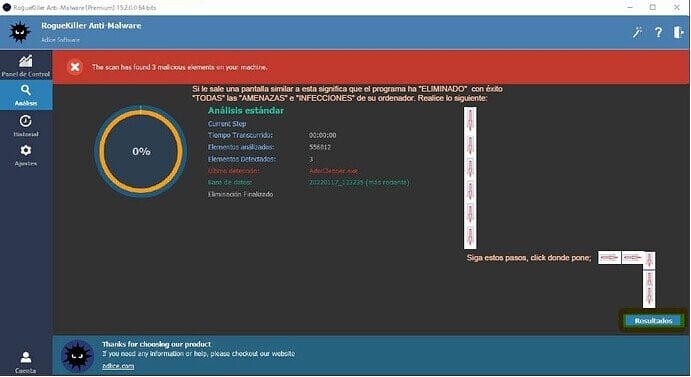
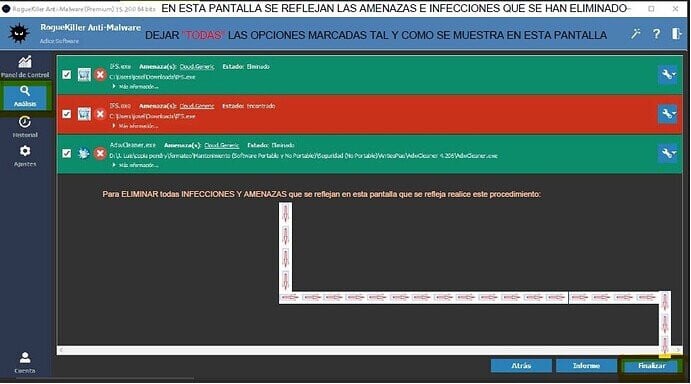
5️⃣ Si le sale una pantalla similar a esta significa que el programa ha **ELIMINADO** con éxito **TODAS** las **AMENAZAS** e **INFECCIONES** de su ordenador. Clickea en la pestaña que pone: **Resultados.** (Tal y cómo se indica en esta página):
6️⃣ Para **ELIMINAR** las **AMENAZAS** e **INFECCIONES** clickea en la pestaña que pone: **Eliminación.** (Tal y como se muestra en esta pantalla):
7️⃣ Le aparecerá una pantalla similar a esta, dejar **TODAS** las opciones marcadas que te salgan a ti. Para **ELIMINAR** todas las **INFECCIONES** clikea en la pestaña que pone: **Finalizar.** (Tal y cómo se muestra en la pantalla):
8️⃣ Para enviarme el **Informe** que ha generado el programa cuando haya finalizado por completo de Analizar siga estos pasos que se reflejan a continuación:
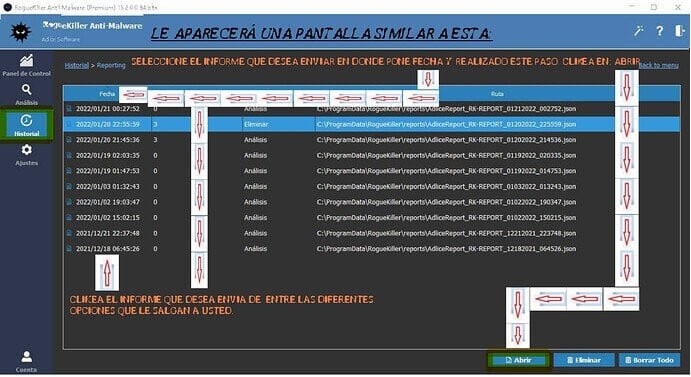
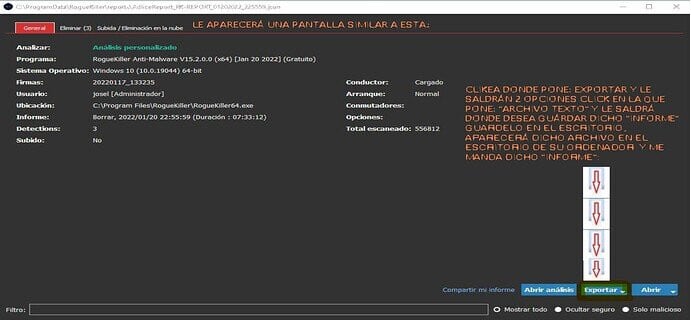
✅ Para poder enviarme usted el **Informe** y/o **Reporte** correctamente que le solicito realice usted los siguientes pasos que le indico a continuación:
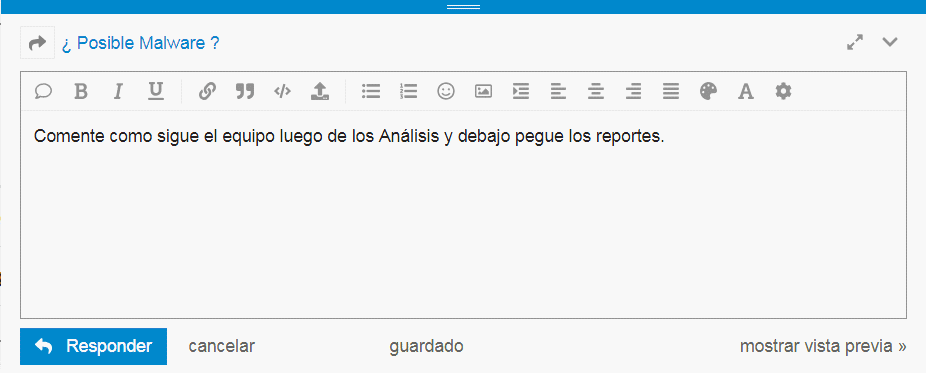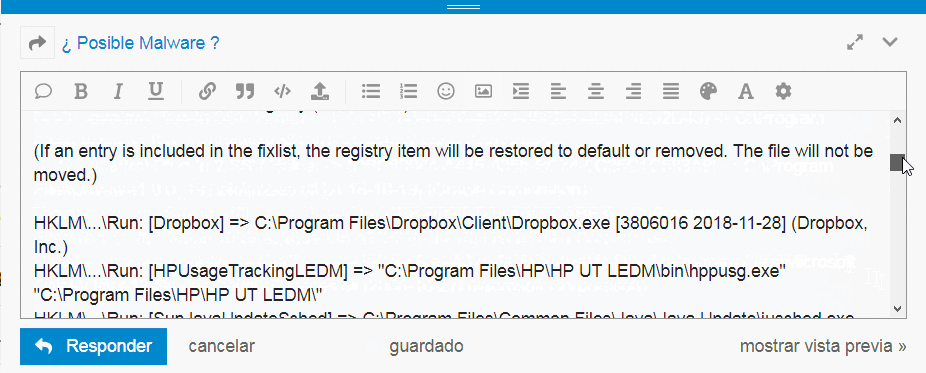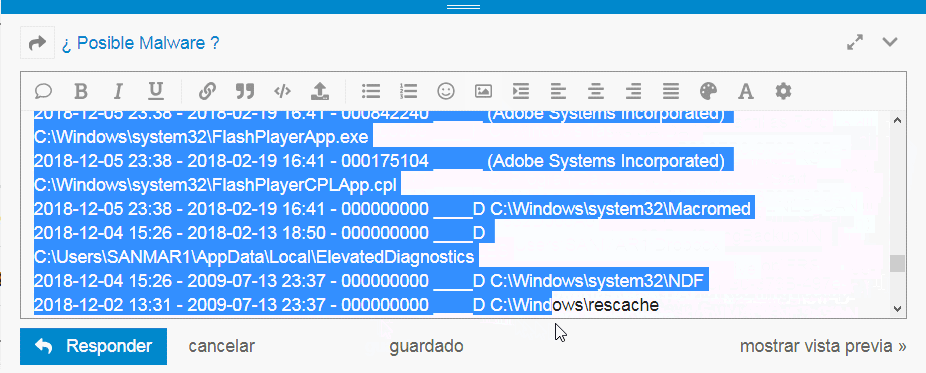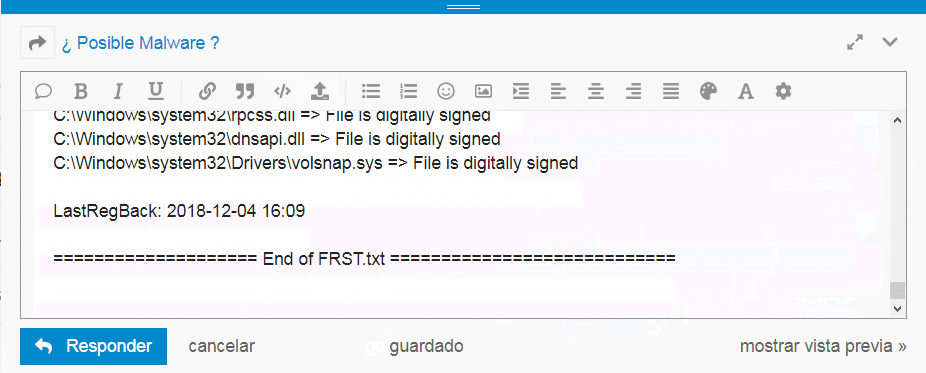
**Url:** [¿Como Pegar Reportes en el Foro?](https://forospyware.com/t/%C2%BFcomo-pegar-reportes-en-el-foro/3497)
**Quedo a la espera de su respuesta!**
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [5 Enero, 2023 10:43 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/31 "2023-01-05T10:43:54Z")
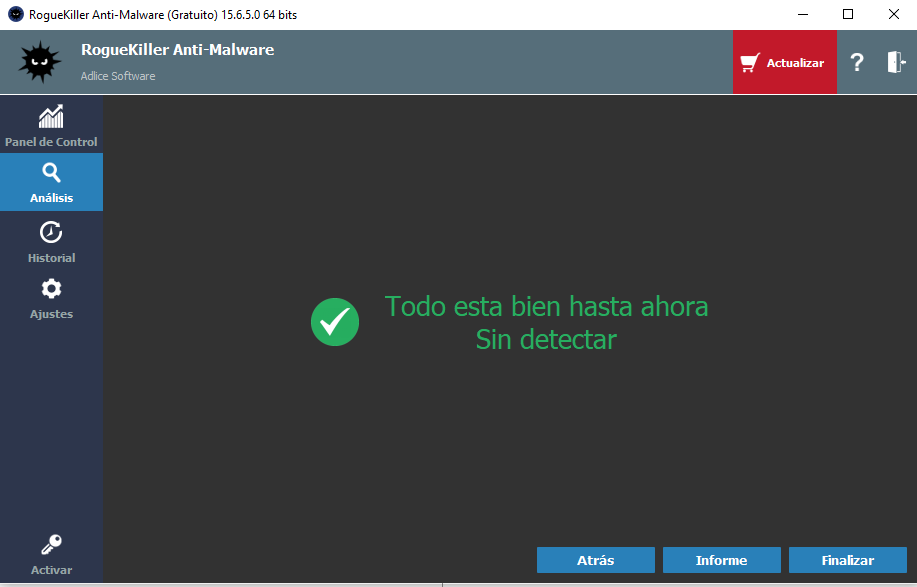
Me ha salido esto, no tengo q hacer nada no?
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [5 Enero, 2023 12:00 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/32 "2023-01-05T12:00:09Z")
Buenas @Bobby1, en respuesta a su pregunta el programa: **RogueKiller** ha realizado correctamente su función y usted ha realizado correctamente todos los procedimientos que le he indicado.
Ahora, **realice usted los siguientes pasos:**
**IMPORTANTE:**
1️⃣ PASALE CADA PROGRAMA POR SEPARADO Y HASTA QUE **NO** ACABE EL PRIMER PROGRAMA DE ANALIZAR POR COMPLETO, **SIGUIENDO LAS INDICACIONES DADAS Y SU MANUAL QUE LE DEJO JUNTO AL PROGRAMA** , **NO** LE PASES EL SIGUIENTE Y ASÍ CON EL RESTO DE PROGRAMA.
2️⃣ QUE SU ORDENADOR **NO** SE PONGA EN **ESTADO DE SUSPENSIÓN** DURANTE TODO EL PROCESO DE ANALISIS QUE SE LE VAN A REALIZAR CON LOS DIFERENTES PROGRAMAS QUE SE LE INDIQUEN EN ESTE FORO, ES DECIR, QUE SU ORDENADOR **NO SE APAGUE LA PANTALLA** YA QUE **PODRÍA INTERFERIR EN EL PROCESO DE ANALISIS** Y **NO** **ELIMINARSE CORRECTAMENTE LAS INFECCIONES Y VIRUS QUE ENCUENTRE.**
3️⃣ SI ALGÚN PROGRAMA DE LOS QUE SE LE DIGA EN ESTE FORO **YA LOS TUVIERA INSTALADO EN SU ORDENADOR** , **NO** HACE FALTA QUE LO INSTALE DE NUEVO, SIMPLEMENTE SIGA SU **MANUAL** QUE SE LE DEJA JUNTO AL PROGRAMA.
4️⃣ SI ALGÚN PROGRAMA DE LOS QUE SE LE INDIQUEN EN ESTE FORO LE PIDE **REINICIAR** PROCEDES! PERO **SÓLO** **SI SE LO SOLICITA DICHO PROGRAMA.**

Aclarado todo esto, **realice lo siguiente:**
**5️⃣ EN BUSCA / ELIMINACIÓN DE MALWARE**
**(Mantén conectados todos tus dispositivos externos que tengas como: USBs, discos duros externos, etc)**
**Por favor, descarga todo el software de los enlaces que pongo/de sus respectivos manuales.**
Ahora ejecutarás una serie de herramientas respetando el orden los pasos **con todos los programas cerrados incluidos los navegadores.**
**Conectas todos tus dispositivos externos (todos los discos duros externos que tengas, así como todas las USB que tengas y discos duros externos si también tienes.**
Realiza los pasos que te pongo a continuación, sin cambiar el orden y síguelos al pie de la letra:
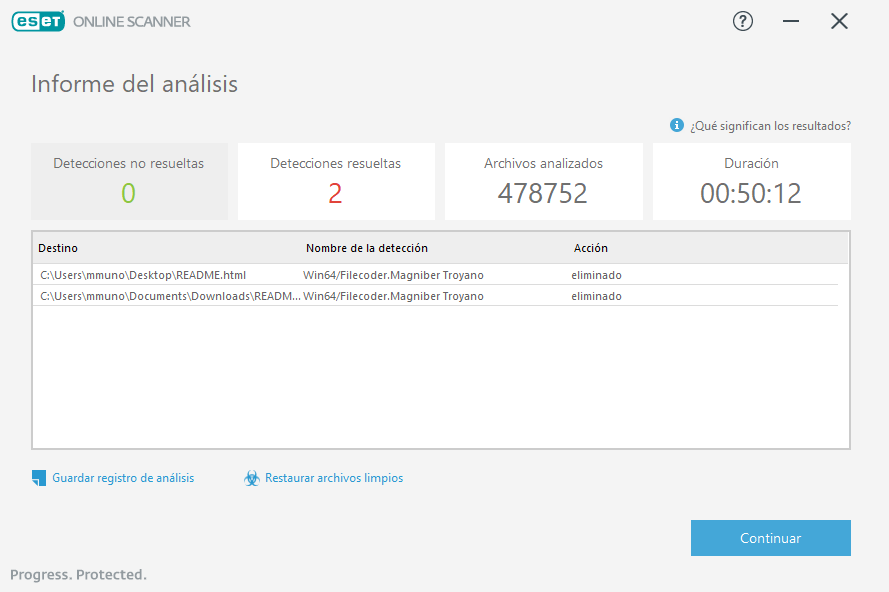
6️⃣ **Descarga** , **Instala** , y **ejecuta:** **Eset Online Scaner**. Aquí le dejo la **Url de Descarga** del: **Eset Online Scaner** , para que sepa cómo descargar e instalar el programa correctamente: [Click aquí: Eset Online Scaner](https://download.eset.com/com/eset/tools/online_scanner/latest/esetonlinescanner_esl.exe). Aquí le dejo su **Manual** del: **Eset Online Scaner** , para que sepa cómo utilizar el programa y configurarlo correctamente: [Click aquí: Manual de Eset Online Scaner](https://forospyware.com/t/manual-de-eset-online-scanner/971). ( **IMPORTANTE:** **Elimine** **TODO** lo que encuentre! y **NO** restaure **NADA** ).
Finalizado el dicho programa completamente envíeme usted solamente una **Captura de Pantalla** **reflejando** **todas** las infecciones y virus que refleje que haya eliminado **el dicho programa**.
**Quedo a la espera de su respuesta!**
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [5 Enero, 2023 17:13 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/33 "2023-01-05T17:13:54Z")
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [5 Enero, 2023 17:54 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/34 "2023-01-05T17:54:26Z")
Ahora, **realice usted los siguientes pasos que le indico a continuación:**
**IMPORTANTE:**
1️⃣ PASALE CADA PROGRAMA POR SEPARADO Y HASTA QUE **NO** ACABE EL PRIMER PROGRAMA DE ANALIZAR POR COMPLETO, **SIGUIENDO LAS INDICACIONES DADAS Y SU MANUAL QUE LE DEJO JUNTO AL PROGRAMA** , **NO** LE PASES EL SIGUIENTE Y ASÍ CON EL RESTO DE PROGRAMA.
2️⃣ QUE SU ORDENADOR **NO** SE PONGA EN **ESTADO DE SUSPENSIÓN** DURANTE TODO EL PROCESO DE ANALISIS QUE SE LE VAN A REALIZAR CON LOS DIFERENTES PROGRAMAS QUE SE LE INDIQUEN EN ESTE FORO, ES DECIR, QUE SU ORDENADOR **NO SE APAGUE LA PANTALLA** YA QUE **PODRÍA INTERFERIR EN EL PROCESO DE ANALISIS** Y **NO** **ELIMINARSE CORRECTAMENTE LAS INFECCIONES Y VIRUS QUE ENCUENTRE.**
3️⃣ SI ALGÚN PROGRAMA DE LOS QUE SE LE DIGA EN ESTE FORO **YA LOS TUVIERA INSTALADO EN SU ORDENADOR** , **NO** HACE FALTA QUE LO INSTALE DE NUEVO, SIMPLEMENTE SIGA SU **MANUAL** QUE SE LE DEJA JUNTO AL PROGRAMA.
4️⃣ SI ALGÚN PROGRAMA DE LOS QUE SE LE INDIQUEN EN ESTE FORO LE PIDE **REINIICAR!** PROCEDES! PERO **SÓLO** **SI SE LO SOLICITA EL DICHO PROGRAMA.**

Una vez aclarado todo esto, **realice usted lo siguiente:**
**5️⃣ EN BUSCA / ELIMINACIÓN DE MALWARE**
**(Mantén conectados todos tus dispositivos externos que tengas como: USBs, discos duros externos, etc)**
**Por favor, descarga todo el software de los enlaces que pongo/de sus respectivos manuales.**
Ahora ejecutarás una serie de herramientas respetando el orden los pasos **con todos los programas cerrados incluidos los navegadores.**
**Conectas todos tus dispositivos externos (todos los discos duros externos que tengas, así como todas las USB que tengas y discos duros externos si también tienes.**
Realiza los pasos que te pongo a continuación, sin cambiar el orden y síguelos al pie de la letra:
6️⃣ **Descarga** , **Instala** , y **ejecuta:** **Malwarebytes**. Aquí le dejo la **Url de Descarga** del: **MalwareBytes** , para que sepas cómo descargarlo y poder instalarlo correctamente: [Click aquí: MalwareBytes](https://downloads.malwarebytes.com/file/mb-windows). Aquí le dejo su **Manual** del: MalwareBytes, para que sepas cómo utilizar el programa y configurarlo correctamente: [Click aquí: **Manual del Malwarebytes**](https://forospyware.com/t/manual-de-malwarebytes-anti-malware/113) y seguidamente realice usted los siguientes pasos que le indico a continuación:
- Realizas un Análisis **PERSONALIZADO** , marcando **Todas las casillas** de la Derecha y de la Izquierda, actualizando si te lo pide. Es decir: **conectas todos tus dispositivos externos (todos los discos duros externos que tengas, así como todas las USB que tengas, incluida la que me has dicho anteriormente** y marcas todas las **unidades de disco disponibles** y las siguientes casillas:
1. **Analizar objetos en memoria**
2. **Analizar configuracion de inicio y registro**
3. **Analizar dentro de los archivos**
4. **NO** **activar** la opción que pone:
- (Si dicha opción está activada muy probablemente se produzca una lentitud en el **Proceso de Análisis** que tarde muchas horas en realizar el **Análisis Personalizado** del **MalwareBytes**. **(Pues esta puede hacer que el programa se cuelgue y no finalice el análisis o hacer que este tarde muchísimo.)**
- Finalizado el **Proceso de Análisis** por completo, si encuentra Amenazas **Pulsar en** **Cuarentena** para enviar las infecciones a la cuarentena y si el programa te pide que **reinicies** , procedes! pero **SÓLO** si te lo solicita dicho programa.)
- Para acceder posteriormente al **Informe** del análisis te diriges a: **Informes** \>\> **Registro de análisis** \>\> pulsas en **Exportar** \>\> **Copiar al Portapapeles** y pones el **Informe** en tu próxima respuesta.
✅ Para poder enviarme usted el **Informe** y/o **Reporte** correctamente que le solicito realice usted los siguientes pasos que le indico a continuación:

**Url:** [¿Como Pegar Reportes en el Foro?](https://forospyware.com/t/%C2%BFcomo-pegar-reportes-en-el-foro/3497)
**Quedo a la espera de su respuesta!**
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [5 Enero, 2023 18:05 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/35 "2023-01-05T18:05:38Z")
```auto
Malwarebytes
www.malwarebytes.com
-Detalles del registro-
Fecha del análisis: 5/1/23
Hora del análisis: 19:01
Archivo de registro: 05f1884a-8d23-11ed-8ae5-38fc98448472.json
-Información del software-
Versión: 4.5.19.229
Versión de los componentes: 1.0.1860
Versión del paquete de actualización: 1.0.64285
Licencia: Caducado
-Información del sistema-
SO: Windows 10 (Build 19044.2364)
CPU: x64
Sistema de archivos: NTFS
Usuario: LAPTOP-HKJ5OOUL\mmuno
-Resumen del análisis-
Tipo de análisis: Análisis de amenazas
Análisis iniciado por:: Manual
Resultado: Completado
Objetos analizados: 274445
Amenazas detectadas: 0
Amenazas en cuarentena: 0
Tiempo transcurrido: 1 min, 0 seg
-Opciones de análisis-
Memoria: Activado
Inicio: Activado
Sistema de archivos: Activado
Archivo: Activado
Rootkits: Desactivado
Heurística: Activado
PUP: Detectar
PUM: Detectar
-Detalles del análisis-
Proceso: 0
(No hay elementos maliciosos detectados)
Módulo: 0
(No hay elementos maliciosos detectados)
Clave del registro: 0
(No hay elementos maliciosos detectados)
Valor del registro: 0
(No hay elementos maliciosos detectados)
Datos del registro: 0
(No hay elementos maliciosos detectados)
Secuencia de datos: 0
(No hay elementos maliciosos detectados)
Carpeta: 0
(No hay elementos maliciosos detectados)
Archivo: 0
(No hay elementos maliciosos detectados)
Sector físico: 0
(No hay elementos maliciosos detectados)
WMI: 0
(No hay elementos maliciosos detectados)
(end)
```
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [6 Enero, 2023 04:52 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/36 "2023-01-06T04:52:05Z")
Buenas @Bobby1, acabo de revisar el Informe que usted me ha mandado con el: **MañwareBytes** y usted ha realizado un proceso de Análisis de: **AMENAZAS** y yo le indique a usted en las indicaciones junto con su **manual** que le he dejado junto al dicho programa que usted me tenía que realizar un proceso de Análisis: **PERSONALIZADO**
```
RESUMEN:
```
1️⃣ Realice usted un proceso de análisis de nuevo **PERSONALIZADO** con el programa: **MalwareBytes** y me manda usted de nuevo lo que le he solicitado.
**Quedo a la espera de su respuesta!**
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [8 Enero, 2023 17:32 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/37 "2023-01-08T17:32:27Z")
Buenas @Bobby1 ¿Pudo usted realizar algún avance?
**Quedo a la espera de su respuesta!**
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [10 Enero, 2023 09:30 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/38 "2023-01-10T09:30:09Z")
perdón, pero no he podido entrar este puente. No me sale ya esa opción en el malwarebytes, lo instalamos aquí hace ya tiempo y me dice q el tiempo de prueba ha caducado y no veo personalizado por ningún lado.
---
### Author:  [@Bobby1](https://forospyware.com/u/Bobby1)
#### Post date: [10 Enero, 2023 12:34 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/39 "2023-01-10T12:34:07Z")
Al final he conseguido hacerlo, de primeras no me salía la opción personalizar, pero después si.
```auto
Malwarebytes
www.malwarebytes.com
-Detalles del registro-
Fecha del análisis: 10/1/23
Hora del análisis: 12:57
Archivo de registro: f26e3ca0-90dd-11ed-bf0f-38fc98448472.json
-Información del software-
Versión: 4.5.19.229
Versión de los componentes: 1.0.1860
Versión del paquete de actualización: 1.0.64469
Licencia: Caducado
-Información del sistema-
SO: Windows 10 (Build 19044.2364)
CPU: x64
Sistema de archivos: NTFS
Usuario: LAPTOP-HKJ5OOUL\mmuno
-Resumen del análisis-
Tipo de análisis: Análisis personalizado
Análisis iniciado por:: Manual
Resultado: Completado
Objetos analizados: 589480
Amenazas detectadas: 0
Amenazas en cuarentena: 0
Tiempo transcurrido: 26 min, 38 seg
-Opciones de análisis-
Memoria: Activado
Inicio: Activado
Sistema de archivos: Activado
Archivo: Activado
Rootkits: Activado
Heurística: Activado
PUP: Detectar
PUM: Detectar
-Detalles del análisis-
Proceso: 0
(No hay elementos maliciosos detectados)
Módulo: 0
(No hay elementos maliciosos detectados)
Clave del registro: 0
(No hay elementos maliciosos detectados)
Valor del registro: 0
(No hay elementos maliciosos detectados)
Datos del registro: 0
(No hay elementos maliciosos detectados)
Secuencia de datos: 0
(No hay elementos maliciosos detectados)
Carpeta: 0
(No hay elementos maliciosos detectados)
Archivo: 0
(No hay elementos maliciosos detectados)
Sector físico: 0
(No hay elementos maliciosos detectados)
WMI: 0
(No hay elementos maliciosos detectados)
(end)
```
---
### Author:  [@Chicloi](https://forospyware.com/u/Chicloi)
#### Post date: [10 Enero, 2023 21:50 UTC](https://forospyware.com/t/fotos-cambiada-extension/29134/40 "2023-01-10T21:50:03Z")
Buenas @curiozzo, acabo de revisar las capturas de pantalla que usted me ha enviado y usted ha realizado correctamente todos los procesos y el programa ha realizado correctamente su función.
Ahora, **realice usted los siguientes pasos:**
**IMPORTANTE:**
1️⃣ PASALE CADA PROGRAMA **POR SEPARADO** Y HASTA QUE **NO** ACABE EL PRIMER PROGRAMA DE ANALIZAR POR COMPLETO, **SIGUIENDO LAS INDICACIONES DADAS** , **NO** LE PASE EL SIGUIENTE Y **ASÍ CON EL RESTO DE PROGRAMAS.**
2️⃣ DURANTE TODO EL PROCESO DE DESINFECCIÓN DE SU ORDENADOR, QUE **NO** SE APAGUE LA PANTALLA, ES DECIR, QUE SU PANTALLA **NO** SE PONGA EN **ESTADO DE SUSPENSION** YA QUE **PUEDE INTERRUMPIRSE EL PROCESO DE DESINFECCIÓN DE SU ORDENADOR** Y **NO** ELIMINAR LAS AMENAZAS E INFECCIONES QUE ENCUENTRE.
3️⃣ SI LOS PROGRAMAS QUE SE LE INDIQUEN EN ESTE FORO QUE SE LE PASEN A SU ORDENADOR **YA LOS TUVIERA INSTALADOS** , **NO** HACE FALTA **QUE LOS INSTALE DE NUEVO** , SIMPLEMENTE **EJECUTE** EL PROGRAMA QUE SE LE INDIQUE EN ESTE FORO Y SIGA **LAS INDICACINES Y EL MANUAL** QUE SE LE DEJA **JUNTO AL PROGRAMA.**
4️⃣ SI ALGUNO DE LOS PROGRAMA DE LOS QUE **SE LE INDIQUE EN ESTE FORO** , **UNA VEZ FINALIZADO EL PROCESO DE ANALISIS** , LE INDICA QUE DEBE **REINICIAR!** PROCEDES! **PERO** **SÓLO SI SE LO INDICA DICHO PROGRAMA**.

Ahora ejecutarás una serie de herramientas respetando el orden los pasos **con todos los programas cerrados incluidos los navegadores.**
5️⃣ **Descargue,** **Instale** y **ejecute** el siguiente programa: **MalwareBytes Anti-Rootkit Beta**. A continuación, le dejo la **Url de Descarga** del programa: **MalwareBytes Anti-Rootkit Beta** , para que sepas cómo descargarlo e instalarlo correctamente y su **Manual** del: **MalwareBytes Anti-Rootkit Beta** , para que sepas cómo utilizarlo y configurarlo correctamente:
5️⃣ . 1️⃣. **Url de Descarga** del: **MalwareBytes Anti-Rootkit Beta:** , para que sepas cómo descargarlo e instalarlo correctamente: [MalwareBytes Anti-Rootkit Beta](https://downloads.malwarebytes.com/file/mbar/).
5️⃣ . 2️⃣. **Manual** del: **MalwareBytes Anti-Rootkit Beta** , para que sepas cómo utilizarlo y configurarlo correctamente: [Click aquí: Manual del MalwareBytes Anti-Rootkit Beta](https://forospyware.com/t/manual-malwarebytes-anti-rootkit-beta/143) ( **IMPORTANTE:** Elimine **TODAS** las amenazas e infecciones que encuentre y **NO** restaure **NADA** ).
```
MUY IMPORTANTE:
```
✅ Una vez finalizado el dicho programa, si encuentra amenazas, veremos una pantalla similar a esta:
✅ Nos aseguraremos que **todas las casillas** están marcadas de los elementos detectados y que la casilla esta tildada **como en la imagen.**
✅ A continuación, para eliminar las amenazas, pulsamos el botón: 
✅ Una vez finalizada la desinfección, pulsamos el botón:  y **reiniciamos** el PC.
5️⃣ . 3️⃣. Siga su **Manual** del: **MalwareBytes Anti-Rootkit Beta** al pie de la letra y me manda una **Captura de Pantalla** con todas las amenazas e infecciones **que se refleje que ´´haya eliminado´´** el dicho programa.
**Quedo a la espera de su respuesta!**
[Página anterior](https://forospyware.com/t/fotos-cambiada-extension/29134.md?page=1)
[Página siguiente](https://forospyware.com/t/fotos-cambiada-extension/29134.md?page=3)