Hola! Desde hace un par de d´´ias tengo esto de la doble tilde. Empez´´o a salir por algo de Adobe (mis licencias son de reseller pero originales), en adobe salia el doble acento pero en los mails por ejemplo no y la primera vez se soluciono reiniciando pero ya no se soluciona mas. Mirando los foros me he descargado el programita “does not belong”, os adjunto el resultado. Malware bytes no detecta nada.muchas gracias!!
DoesNotBelong_2026_06_26__08_07_11
_________________________________________________________________
# DoesNotBelong v11.5.8
# https://furtivex.net
# OS: Microsoft Windows 11 Home x64 25H2 Español (Spanish) - 0c0a - 1252 - 850
# Nombre de usuario: Usuario -> S-1-5-21-1383289433-3324560724-2772928039-1001
# Nombre del equipo: DESKTOP-65C6GUU
# Fecha: 2026_06_26__08_07_11
_________________________________________________________________

# Procesos:

# Servicios:

# Navegadores:

Chrome - Perfil: C:\Users\Usuario\AppData\Local\Google\Chrome\User Data\Default
Edge - Perfil: C:\Users\Usuario\AppData\Local\Microsoft\Edge\User Data\Default
Firefox - Perfil: C:\Users\Usuario\AppData\Roaming\Mozilla\Firefox\Profiles\6e6r0fkv.default-release

# Archivos:

C:\Perform\1.ps1
C:\Perform\7za.exe
C:\Perform\audio.vbs
C:\Perform\email.bat
C:\Perform\files.7z
C:\Perform\ntrights.exe
C:\Perform\Setu64.exe
C:\Perform\sys.vbs
C:\Perform\system.bat
C:\Perform\system.bat.bak
C:\Perform\system.ico
C:\Perform\system.vbs
C:\Perform\system.xml
C:\Perform\system32.vbs
C:\Perform\unistall.bat.bak
C:\Perform\unistall.vbs
C:\Perform\update.vbs
C:\Perform\WinIo64.sys
C:\Perform\WinRing0x64.sys
C:\Program Files\CCleaner\CCleanerPerformanceOptimizerService.exe
C:\Program Files\NVIDIA Corporation\NvBackend\NvTmRep.exe
C:\ProgramData\49237629106530378148.exe
C:\ProgramData\95473818803598533939.exe
C:\ProgramData\gemrc
C:\Users\Public\Documents\AdobeInstalledCodecsTier2\4.0\mc_dec_hevc.dll
C:\Users\Public\Documents\AdobeInstalledCodecsTier2\4.0\mc_enc_hevc.dll
C:\Users\Public\Documents\AdobeInstalledCodecsTier2\4.3\mc_dec_hevc.dll
C:\Users\Public\Documents\AdobeInstalledCodecsTier2\4.3\mc_enc_hevc.dll
C:\Users\Usuario\AppData\Local\Lavasoft\Search\Logs\search.log
C:\Users\Usuario\AppData\Local\Lavasoft\WebCompanion.exe_Url_mrpq523xmeo0cm2m0n5vj25z3nzkgep4\7.0.2417.4248\user.config
C:\Users\Usuario\AppData\Local\Lavasoft\WebCompanion.exe_Url_siq0lwf3tzgxp2khfkllybk3idtbehng\7.0.2417.4248\user.config
C:\Users\Usuario\AppData\Local\Lavasoft\WebCompanion.exe_Url_siq0lwf3tzgxp2khfkllybk3idtbehng\8.9.0.371\user.config
C:\Users\Usuario\AppData\Local\Lavasoft\WebCompanion.exe_Url_siq0lwf3tzgxp2khfkllybk3idtbehng\8.9.0.748\user.config
C:\Users\Usuario\AppData\Local\Microsoft\MSBuild\c_3791.proj
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\officec2rclient.exe.db
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\officeclicktorun.exe.db
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\officeclicktorun.exe.db-shm
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\officeclicktorun.exe.db-wal
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\operfmon.exe.db
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\operfmon.exe.db-shm
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\operfmon.exe.db-wal
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\setup.exe.db
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\setup.exe.db-shm
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\setup.exe.db-wal
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\winword.exe.db
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\winword.exe.db-shm
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele\winword.exe.db-wal
C:\Users\Usuario\AppData\LocalLow\wbk194B.tmp
C:\Users\Usuario\AppData\LocalLow\wbk2702.tmp
C:\Users\Usuario\AppData\LocalLow\wbk328D.tmp
C:\Users\Usuario\AppData\LocalLow\wbk42B9.tmp
C:\Users\Usuario\AppData\LocalLow\wbk49B4.tmp
C:\Users\Usuario\AppData\LocalLow\wbk4A37.tmp
C:\Users\Usuario\AppData\LocalLow\wbk7177.tmp
C:\Users\Usuario\AppData\LocalLow\wbk792A.tmp
C:\Users\Usuario\AppData\LocalLow\wbkB257.tmp
C:\Users\Usuario\AppData\LocalLow\wbkC426.tmp
C:\Users\Usuario\AppData\LocalLow\wbkD146.tmp
C:\Users\Usuario\AppData\LocalLow\wbkEF2F.tmp
C:\Users\Usuario\AppData\LocalLow\wbkF654.tmp
C:\Users\Usuario\AppData\Roaming\Lavasoft\Search\ProfileInfo.txt
C:\Users\Usuario\AppData\Roaming\Lavasoft\Search\searchenginetemplate.xml
C:\WINDOWS\Installer\MSI1013.tmp
C:\WINDOWS\Installer\MSI1055.tmp
C:\WINDOWS\Installer\MSI10B1.tmp
C:\WINDOWS\Installer\MSI10E3.tmp
C:\WINDOWS\Installer\MSI112F.tmp
C:\WINDOWS\Installer\MSI11AD.tmp
C:\WINDOWS\Installer\MSI192F.tmp
C:\WINDOWS\Installer\MSI19CD.tmp
C:\WINDOWS\Installer\MSI1D57.tmp
C:\WINDOWS\Installer\MSI1DD5.tmp
C:\WINDOWS\Installer\MSI1EB1.tmp
C:\WINDOWS\Installer\MSI2327.tmp
C:\WINDOWS\Installer\MSI2A29.tmp
C:\WINDOWS\Installer\MSI2AA7.tmp
C:\WINDOWS\Installer\MSI40F0.tmp
C:\WINDOWS\Installer\MSI40F2.tmp
C:\WINDOWS\Installer\MSI4170.tmp
C:\WINDOWS\Installer\MSI417E.tmp
C:\WINDOWS\Installer\MSI41EE.tmp
C:\WINDOWS\Installer\MSI420C.tmp
C:\WINDOWS\Installer\MSI429D.tmp
C:\WINDOWS\Installer\MSI42A9.tmp
C:\WINDOWS\Installer\MSI434A.tmp
C:\WINDOWS\Installer\MSI4394.tmp
C:\WINDOWS\Installer\MSI4460.tmp
C:\WINDOWS\Installer\MSI44A2.tmp
C:\WINDOWS\Installer\MSI44FE.tmp
C:\WINDOWS\Installer\MSI455F.tmp
C:\WINDOWS\Installer\MSI457C.tmp
C:\WINDOWS\Installer\MSI45FC.tmp
C:\WINDOWS\Installer\MSI4667.tmp
C:\WINDOWS\Installer\MSI467A.tmp
C:\WINDOWS\Installer\MSI46E5.tmp
C:\WINDOWS\Installer\MSI4763.tmp
C:\WINDOWS\Installer\MSI486F.tmp
C:\WINDOWS\Installer\MSI489D.tmp
C:\WINDOWS\Installer\MSI4A93.tmp
C:\WINDOWS\Installer\MSI4B11.tmp
C:\WINDOWS\Installer\MSI4B8F.tmp
C:\WINDOWS\Installer\MSI4BD.tmp
C:\WINDOWS\Installer\MSI51EA.tmp
C:\WINDOWS\Installer\MSI55A.tmp
C:\WINDOWS\Installer\MSI636.tmp
C:\WINDOWS\Installer\MSI703.tmp
C:\WINDOWS\Installer\MSI83D.tmp
C:\WINDOWS\Installer\MSI89F.tmp
C:\WINDOWS\Installer\MSIA26.tmp
C:\WINDOWS\Installer\MSIBF7.tmp
C:\WINDOWS\Installer\MSICC4.tmp
C:\WINDOWS\Installer\MSID92.tmp
C:\WINDOWS\Installer\MSIDDE.tmp
C:\WINDOWS\Installer\MSIE3F.tmp
C:\WINDOWS\Installer\MSIE5C.tmp
C:\WINDOWS\Installer\MSIE61C.tmp
C:\WINDOWS\Installer\MSIE6E9.tmp
C:\WINDOWS\Installer\MSIEDC.tmp
C:\WINDOWS\Installer\MSIF86.tmp
C:\WINDOWS\Installer\MSIFC8.tmp
C:\WINDOWS\Installer\MSIFD33.tmp
C:\WINDOWS\ServiceProfiles\NetworkService\Appdata\Local\Microsoft\Windows\usrclass.dat
C:\WINDOWS\System32\GroupPolicy\GPT.ini
C:\WINDOWS\System32\GroupPolicy\Machine\Registry.pol

# Carpetas:

C:\Perform
C:\Program Files (x86)\Lavasoft
C:\Users\Usuario\AppData\Local\Lavasoft
C:\Users\Usuario\AppData\Local\Microsoft\Office\OTele
C:\Users\Usuario\AppData\Roaming\Lavasoft
C:\WINDOWS\Installer\MSI125D.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI12AC.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI1C25.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI1C74.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI22AF.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI25CE.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI263D.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI2E1D.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI3D5B.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI3E85.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI4AED.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI4B5B.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSI5455.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSIF5A4.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSIF5F3.tmp- (JUNK.EmptyInstaller)
C:\WINDOWS\Installer\MSIF6CE.tmp- (JUNK.EmptyInstaller)

# Tareas:

Agent Activation Runtime\S-1-5-21-1383289433-3324560724-2772928039-1001
ASUS\AcPowerNotification
ASUS\ArmourySocketServer
ASUS\ASUSUpdateTaskMachineCore1dc7a385017f63e
ASUS\ASUSUpdateTaskMachineUA
ASUS\P508PowerAgent_sdk
audio system
CCleaner Update
CCleanerCrashReporting
CCleanerSkipUAC - Usuario
GarminUpdaterTask
GoogleSystem\GoogleUpdater\GoogleUpdaterTaskSystem150.0.7863.0{96CA8F89-BA5B-4EF1-91AF-7D2393676AB5}
GoogleUserPEH\RunPlatformExperienceHelper_Daily
GoogleUserPEH\RunPlatformExperienceHelper_Metrics
Microsoft\Office\Office Actions Server
Microsoft\Office\Office Automatic Updates 2.0
Microsoft\Office\Office Background Push Maintenance
Microsoft\Office\Office ClickToRun Service Monitor
Microsoft\Office\Office Feature Updates
Microsoft\Office\Office Feature Updates Logon
Microsoft\Office\Office Performance Monitor
Microsoft\Windows\AccountHealth\RecoverabilityToastTask
Microsoft\Windows\AppID\EDP Policy Manager
Microsoft\Windows\Application Experience\MareBackup
Microsoft\Windows\Application Experience\Microsoft Compatibility Appraiser Exp
Microsoft\Windows\Application Experience\PcaPatchDbTask
Microsoft\Windows\Application Experience\SdbinstMergeDbTask
Microsoft\Windows\Application Experience\StartupAppTask
Microsoft\Windows\ApplicationData\appuriverifierdaily
Microsoft\Windows\ApplicationData\appuriverifierinstall
Microsoft\Windows\ApplicationData\DsSvcCleanup
Microsoft\Windows\capabilityaccessmanager\maintenancetasks
Microsoft\Windows\Chkdsk\ProactiveScan
Microsoft\Windows\Clip\ClipESU
Microsoft\Windows\Clip\ClipESUConsumer
Microsoft\Windows\Clip\ClipESUConsumerProcessECUpdate
Microsoft\Windows\Clip\ClipEsuConsumerProcessPreOrder
Microsoft\Windows\Clip\ClipEsuConsumerProcessRefund
Microsoft\Windows\Clip\EnableClipESU
Microsoft\Windows\CloudExperienceHost\CreateObjectTask
Microsoft\Windows\ConsentUX\UnifiedConsent\UnifiedConsentSyncTask
Microsoft\Windows\Customer Experience Improvement Program\Consolidator
Microsoft\Windows\Customer Experience Improvement Program\UsbCeip
Microsoft\Windows\Defrag\ScheduledDefrag
Microsoft\Windows\Device Setup\Driver Recovery on Reboot
Microsoft\Windows\Diagnosis\RecommendedTroubleshootingScanner
Microsoft\Windows\Diagnosis\Scheduled
Microsoft\Windows\Diagnosis\UnexpectedCodepath
Microsoft\Windows\DiskDiagnostic\Microsoft-Windows-DiskDiagnosticDataCollector
Microsoft\Windows\DiskDiagnostic\Microsoft-Windows-DiskDiagnosticResolver
Microsoft\Windows\DiskFootprint\Diagnostics
Microsoft\Windows\DiskFootprint\StorageSense
Microsoft\Windows\Feedback\Siuf\DmClient
Microsoft\Windows\Feedback\Siuf\DmClientOnScenarioDownload
Microsoft\Windows\Flighting\FeatureConfig\BootstrapUsageDataReporting
Microsoft\Windows\Flighting\FeatureConfig\GovernedFeatureUsageProcessing
Microsoft\Windows\Flighting\FeatureConfig\ReconcileConfigs
Microsoft\Windows\Flighting\FeatureConfig\ReconcileFeatures
Microsoft\Windows\Flighting\FeatureConfig\SafeguardsReconciliation
Microsoft\Windows\Flighting\FeatureConfig\UsageDataFlushing
Microsoft\Windows\Flighting\FeatureConfig\UsageDataReceiver
Microsoft\Windows\Flighting\FeatureConfig\UsageDataReporting
Microsoft\Windows\Flighting\OneSettings\RefreshCache
Microsoft\Windows\HelloFace\FODCleanupTask
Microsoft\Windows\Hotpatch\Monitoring
Microsoft\Windows\input\RemoteMouseSyncDataAvailable
Microsoft\Windows\input\RemotePenSyncDataAvailable
Microsoft\Windows\input\RemoteTouchpadSyncDataAvailable
Microsoft\Windows\InstallService\RestoreDevice
Microsoft\Windows\InstallService\ScanForUpdates
Microsoft\Windows\InstallService\ScanForUpdatesAsUser
Microsoft\Windows\InstallService\SmartRetry
Microsoft\Windows\InstallService\WakeUpAndContinueUpdates
Microsoft\Windows\InstallService\WakeUpAndScanForUpdates
Microsoft\Windows\Location\Notifications
Microsoft\Windows\Maintenance\WinSAT
Microsoft\Windows\Maps\MapsToastTask
Microsoft\Windows\Maps\MapsUpdateTask
Microsoft\Windows\MemoryDiagnostic\AutomaticOfflineMemoryDiagnostic
Microsoft\Windows\MemoryDiagnostic\ProcessMemoryDiagnosticEvents
Microsoft\Windows\MemoryDiagnostic\RunFullMemoryDiagnostic
Microsoft\Windows\Mobile Broadband Accounts\MNO Metadata Parser
Microsoft\Windows\MSBuild\32240b79-6b29-57bc-39b2fa
Microsoft\Windows\Network Connectivity Status Indicator\NcsiIdentifyUserProxies
Microsoft\Windows\PCRPF\PCR Prediction Framework Firmware Update Task
Microsoft\Windows\PerformanceTrace\RequestTrace
Microsoft\Windows\PerformanceTrace\ShowFeedbackToast
Microsoft\Windows\PerformanceTrace\WhesvcToast
Microsoft\Windows\Pluton\Pluton-Ksp-Provisioning
Microsoft\Windows\Power Efficiency Diagnostics\AnalyzeSystem
Microsoft\Windows\PushToInstall\LoginCheck
Microsoft\Windows\PushToInstall\Registration
Microsoft\Windows\ReFsDedupSvc\Initialization
Microsoft\Windows\RemoteAssistance\RemoteAssistanceTask
Microsoft\Windows\Servicing\OOBEFodSetup
Microsoft\Windows\Setup\PITRTask
Microsoft\Windows\Setup\SetupRecoveryDataTask
Microsoft\Windows\Shell\CreateObjectTask
Microsoft\Windows\Shell\FamilySafetyMonitor
Microsoft\Windows\Shell\FamilySafetyRefreshTask
Microsoft\Windows\Shell\IndexerAutomaticMaintenance
Microsoft\Windows\Shell\ThemesSyncedImageDownload
Microsoft\Windows\Shell\UpdateUserPictureTaskContained
Microsoft\Windows\Subscription\EnableLicenseAcquisition
Microsoft\Windows\Subscription\LicenseAcquisition
Microsoft\Windows\Sustainability\PowerGridForecastTask
Microsoft\Windows\Sustainability\SustainabilityTelemetry
Microsoft\Windows\UpdateOrchestrator\Reboot_AC
Microsoft\Windows\UpdateOrchestrator\Reboot_Battery
Microsoft\Windows\UpdateOrchestrator\UIEOrchestrator
Microsoft\Windows\UpdateOrchestrator\USO_UxBroker
Microsoft\Windows\UsageAndQualityInsights\UsageAndQualityInsights-MaintenanceTask
Microsoft\Windows\User Profile Service\HiveUploadTask
Microsoft\Windows\Windows Media Sharing\UpdateLibrary
Microsoft\Windows\WindowsAI\ClickToDo\ModelCachingIdle
Microsoft\Windows\WindowsAI\ClickToDo\ModelCachingLimit
Microsoft\Windows\WindowsAI\ClickToDo\ModelCachingUpdate
Microsoft\Windows\WindowsAI\Recall\InitialConfiguration
Microsoft\Windows\WindowsAI\Recall\PolicyConfiguration
Microsoft\Windows\WindowsAI\Settings\InitialConfiguration
Microsoft\Windows\WindowsUpdate\Refresh Group Policy Cache
Microsoft\Windows\WindowsUpdate\Scheduled Start
Microsoft\Windows\WOF\WIM-Hash-Management
Microsoft\Windows\WOF\WIM-Hash-Validation
Microsoft\Windows\WwanSvc\NotificationTask
Microsoft\Windows\WwanSvc\OobeDiscovery
Microsoft\XblGameSave\XblGameSaveTask
MicrosoftEdgeUpdateTaskMachineCore
MicrosoftEdgeUpdateTaskMachineUA
Mozilla\Firefox Background Update 308046B0AF4A39CB
Mozilla\Firefox Background Update S-1-5-21-1383289433-3324560724-2772928039-1001 308046B0AF4A39CB
Mozilla\Firefox Default Browser Agent 308046B0AF4A39CB
NvDriverUpdateCheckDaily_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NVIDIA GeForce Experience SelfUpdate_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NvNodeLauncher_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NvProfileUpdaterDaily_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NvProfileUpdaterOnLogon_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NvTmRep_CrashReport1_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NvTmRep_CrashReport2_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NvTmRep_CrashReport3_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
NvTmRep_CrashReport4_{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}
OneDrive Per-Machine Standalone Update Task
OneDrive Reporting Task-S-1-5-21-1383289433-3324560724-2772928039-1001
OneDrive Startup Task-S-1-5-21-1383289433-3324560724-2772928039-1001
SoftLanding\S-1-5-21-1383289433-3324560724-2772928039-1001\SoftLandingCreativeManagementTask

# Registro:

HKCU\Software\Lavasoft
HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings\ZoneMap\Domains\webcompanion.com
HKLM\Software\Microsoft\Tracing\esu_RASAPI32
HKLM\Software\Microsoft\Tracing\esu_RASMANCS
HKLM\Software\Microsoft\Tracing\express_RASAPI32
HKLM\Software\Microsoft\Tracing\express_RASMANCS
HKCU\Software\Microsoft\Windows\CurrentVersion\ContentDeliveryManager\\SystemPaneSuggestionsEnabled [1] => [0]
HKCU\Software\Microsoft\Windows\CurrentVersion\ContentDeliveryManager\SubscribedContent-310093Enabled
HKCU\Software\Microsoft\Windows\CurrentVersion\ContentDeliveryManager\SubscribedContent-338388Enabled
HKCU\Software\Microsoft\Windows\CurrentVersion\ContentDeliveryManager\SubscribedContent-338389Enabled
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\AdobeBridge
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\CCleaner Smart Cleaning
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\CCXProcess
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\d4893001-e66e-5bc8-35f6cf
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\GarminExpress
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\profile
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\Teams
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\StartupApproved\Run\\telemetry
HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Connections\\DefaultConnectionSettings
HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Connections\\SavedLegacySettings
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\\AdobeBridge
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\\d4893001-e66e-5bc8-35f6cf
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\\GarminExpress
HKCU\Software\Microsoft\Windows\CurrentVersion\Run\\Teams
HKCR\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKCR\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Microsoft.BingNews_8wekyb3d8bbwe
HKCR\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Microsoft.BingSearch_8wekyb3d8bbwe
HKCR\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Microsoft.BingWeather_8wekyb3d8bbwe
HKCR\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKCU\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKCU\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Microsoft.BingNews_8wekyb3d8bbwe
HKCU\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Microsoft.BingSearch_8wekyb3d8bbwe
HKCU\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\Microsoft.BingWeather_8wekyb3d8bbwe
HKCU\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PolicyCache\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKCU\Software\Microsoft\Windows NT\CurrentVersion\HostActivityManager\CommitHistory\Clipchamp.Clipchamp_yxz26nhyzhsrt!App
HKCU\Software\Microsoft\Windows NT\CurrentVersion\HostActivityManager\CommitHistory\Microsoft.BingWeather_8wekyb3d8bbwe!App
HKCU\Software\Microsoft\Windows NT\CurrentVersion\HostActivityManager\CommitHistory\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy!Global.WidgetBoard
HKCU\Software\Microsoft\Windows NT\CurrentVersion\HostActivityManager\CommitHistory\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy!Widgets
HKCU\Software\Microsoft\Windows NT\CurrentVersion\HostActivityManager\CommitHistory\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy!WidgetService
HKCU\Software\Microsoft\Windows\CurrentVersion\BackgroundAccessApplications\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKCU\Software\Microsoft\Windows\CurrentVersion\BackgroundAccessApplications\Microsoft.BingNews_8wekyb3d8bbwe
HKCU\Software\Microsoft\Windows\CurrentVersion\BackgroundAccessApplications\Microsoft.BingSearch_8wekyb3d8bbwe
HKCU\Software\Microsoft\Windows\CurrentVersion\BackgroundAccessApplications\Microsoft.BingWeather_8wekyb3d8bbwe
HKCU\Software\Microsoft\Windows\CurrentVersion\BackgroundAccessApplications\Microsoft.Edge.GameAssist_8wekyb3d8bbwe
HKCU\Software\Microsoft\Windows\CurrentVersion\BackgroundAccessApplications\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKLM\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PackageRepository\Packages\Microsoft.Advertising.Xaml_10.1808.3.0_x64__8wekyb3d8bbwe
HKLM\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PackageRepository\Packages\Microsoft.BingWeather_4.25.20211.0_neutral_split.scale-150_8wekyb3d8bbwe
HKLM\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\PackageRepository\Packages\Microsoft.Edge.GameAssist_1.0.4019.0_x64__8wekyb3d8bbwe
HKLM\Software\Microsoft\SecurityManager\CapAuthz\ApplicationsEx\Microsoft.Edge.GameAssist_1.0.4019.0_x64__8wekyb3d8bbwe
HKLM\Software\Microsoft\Shared Tools\MSConfig\services\TeamViewer
HKLM\Software\Microsoft\Shared Tools\MSConfig\services\WpcMonSvc
HKLM\System\Setup\Upgrade\Appx\AppxAllUserStore\Staged\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKLM\System\Setup\Upgrade\Appx\AppxAllUserStore\Staged\Microsoft.Advertising.Xaml_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\AppxAllUserStore\Staged\Microsoft.BingNews_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\AppxAllUserStore\Staged\Microsoft.BingSearch_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\AppxAllUserStore\Staged\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\AppxAllUserStore\Applications\Microsoft.BingWeather_4.54.63029.0_neutral_~_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\AppxAllUserStore\S-1-5-18\Microsoft.BingWeather_4.54.63029.0_neutral_~_8wekyb3d8bbwe
HKLM\SYSTEM\Setup\Upgrade\Appx\DownlevelGather\AppxAllUserStore\S-1-5-21-1383289433-3324560724-2772928039-1001\Microsoft.BingWeather_4.54.63029.0_neutral_~_8wekyb3d8bbwe
HKLM\SYSTEM\Setup\Upgrade\Appx\DownlevelGather\AppxAllUserStore\S-1-5-21-1383289433-3324560724-2772928039-1001\Microsoft.Edge.GameAssist_1.0.3456.0_x64__8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.Advertising.Xaml_10.1808.3.0_x64__8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingSearch_1.1.40.0_neutral_split.language-ca_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingSearch_1.1.40.0_neutral_split.language-es_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingSearch_1.1.40.0_neutral_split.scale-150_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingSearch_1.1.40.0_x64__8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingSearch_2022.1.40.0_neutral_~_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingWeather_4.54.63029.0_neutral_~_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingWeather_4.54.63029.0_neutral_split.language-ca_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingWeather_4.54.63029.0_neutral_split.language-es_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingWeather_4.54.63029.0_neutral_split.scale-100_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingWeather_4.54.63029.0_neutral_split.scale-150_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\PackageInstallState\Microsoft.BingWeather_4.54.63029.0_x64__8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.Advertising.Xaml_10.1808.3.0_x64__8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingSearch_1.1.40.0_neutral_split.language-ca_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingSearch_1.1.40.0_neutral_split.language-es_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingSearch_1.1.40.0_neutral_split.scale-150_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingSearch_1.1.40.0_x64__8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingSearch_2022.1.40.0_neutral_~_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingWeather_4.54.63029.0_neutral_~_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingWeather_4.54.63029.0_neutral_split.language-ca_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingWeather_4.54.63029.0_neutral_split.language-es_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingWeather_4.54.63029.0_neutral_split.scale-100_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingWeather_4.54.63029.0_neutral_split.scale-150_8wekyb3d8bbwe
HKLM\System\Setup\Upgrade\Appx\DownlevelGather\SisDirectory\Microsoft.BingWeather_4.54.63029.0_x64__8wekyb3d8bbwe
HKU\.DEFAULT\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKU\.DEFAULT\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingNews_8wekyb3d8bbwe
HKU\.DEFAULT\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingSearch_8wekyb3d8bbwe
HKU\.DEFAULT\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingWeather_8wekyb3d8bbwe
HKU\.DEFAULT\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKU\S-1-5-18\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKU\S-1-5-18\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingNews_8wekyb3d8bbwe
HKU\S-1-5-18\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingSearch_8wekyb3d8bbwe
HKU\S-1-5-18\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingWeather_8wekyb3d8bbwe
HKU\S-1-5-18\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKU\S-1-5-19\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKU\S-1-5-19\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingNews_8wekyb3d8bbwe
HKU\S-1-5-19\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingSearch_8wekyb3d8bbwe
HKU\S-1-5-19\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingWeather_8wekyb3d8bbwe
HKU\S-1-5-19\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKU\S-1-5-19\Software\Microsoft\Windows\CurrentVersion\RunOnce\\OneDrive
HKU\S-1-5-20\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Clipchamp.Clipchamp_yxz26nhyzhsrt
HKU\S-1-5-20\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingNews_8wekyb3d8bbwe
HKU\S-1-5-20\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingSearch_8wekyb3d8bbwe
HKU\S-1-5-20\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\Microsoft.BingWeather_8wekyb3d8bbwe
HKU\S-1-5-20\Software\Classes\Local Settings\Software\Microsoft\Windows\CurrentVersion\AppModel\SystemAppData\MicrosoftWindows.Client.WebExperience_cw5n1h2txyewy
HKU\S-1-5-20\Software\Microsoft\Windows\CurrentVersion\RunOnce\\OneDrive
HKLM\Software\Microsoft\Windows\CurrentVersion\Run\\Adobe CCXProcess
HKLM\Software\Microsoft\Windows\CurrentVersion\Run\\Adobe Creative Cloud
HKLM\Software\Microsoft\Windows\CurrentVersion\Run\\KeePass 2 PreLoad
HKLM\Software\WOW6432Node\Microsoft\Windows\CurrentVersion\Run\\Adobe CCXProcess
HKLM\Software\WOW6432Node\Microsoft\Windows\CurrentVersion\Run\\Adobe Creative Cloud
HKLM\Software\WOW6432Node\Microsoft\Windows\CurrentVersion\Run\\KeePass 2 PreLoad
HKLM\System\CurrentControlSet\Control\CrashControl\\AutoReboot [1] => [0]
HKLM\System\CurrentControlSet\Control\Session Manager\Power\\HiberbootEnabled [1] => [0]
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{1B7FB2FB-C898-423C-8B7C-5711EB917D7C}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{2E253B83-C109-4BB0-A6A8-8A35BEF465F1}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{3A564DF7-367A-463E-8246-2CC4CA1A38E4}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{72F00BCA-FE3F-4B63-86F2-2A9CD6B4A917}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{7E6CC54C-33A1-4EC8-8B72-6AFC173ACB5C}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{87BE295F-3831-46BD-A7CD-C66C87399682}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{8AC8C8CC-8561-4C1E-A743-671889073C3F}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{9E3928F4-E383-46C5-87CE-CA6172B92152}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{9E5B9B37-753B-4A03-833F-0412B753CDAD}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{AE66674F-AA79-426B-9A56-615705D0F0C0}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{B9BBEC00-FFF3-45C5-88B9-C994D428E6B1}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{BD3A0720-8735-4485-AABB-3B72FF524625}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{C14FA19A-3197-4C90-A74C-BE7BE2D2E1C4}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{D0E49761-5085-41CF-B3C5-051102B3394E}
HKLM\System\CurrentControlSet\Services\SharedAccess\Parameters\FirewallPolicy\FirewallRules\\{D1C39367-F2BD-4F5A-9D77-D4D5BF3D4E67}
HKU\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Connections\\DefaultConnectionSettings
HKU\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Internet Settings\Connections\\SavedLegacySettings

# Cachés:

C:\ProgramData\Microsoft\Search\Data\Applications\Windows\GatherLogs\SystemIndex (F-121)
C:\Users\Usuario\AppData\Local\D3DSCache (D-0)
C:\Users\Usuario\AppData\Local\Microsoft\Office\16.0\OfficeFileCache (F-1)
C:\Users\Usuario\AppData\Local\Microsoft\TokenBroker\Cache (F-16)
C:\Users\Usuario\AppData\Local\Microsoft\Windows\ActionCenterCache (F-1)
C:\Users\Usuario\AppData\Local\Microsoft\Windows\INetCache\IE (D-4)
C:\Users\Usuario\AppData\Local\Mozilla\Firefox\Profiles\<Profile>\cache2\entries (F-21968)
C:\Users\Usuario\AppData\Local\NVIDIA\DxCache (F-542)
C:\Users\Usuario\AppData\Local\NVIDIA\GLCache (F-70)
C:\Users\Usuario\AppData\Local\Temp (D-52)
C:\Users\Usuario\AppData\LocalLow\Sun\Java\Deployment\cache\6.0 (D-66)
C:\Users\Usuario\AppData\Roaming\Mozilla\Firefox\Profiles\<Profile>\shader-cache (F-29)
C:\WINDOWS\Logs\CBS (F-1)
C:\WINDOWS\Logs\SIH (F-6)
C:\WINDOWS\Logs\WindowsUpdate (F-43)
C:\WINDOWS\Prefetch (F-499)
C:\WINDOWS\SchCache (F-0)
C:\WINDOWS\ServiceProfiles\LocalService\AppData\Local\FontCache\Fonts (F-1)
C:\WINDOWS\ServiceProfiles\LocalService\AppData\Local\NVIDIA\DxCache (F-2)
C:\WINDOWS\ServiceProfiles\LocalService\AppData\Local\Temp (F-0)
C:\WINDOWS\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\DeliveryOptimization\Cache (D-11)
C:\WINDOWS\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\DeliveryOptimization\Logs (F-349)
C:\WINDOWS\ServiceProfiles\NetworkService\AppData\Local\Microsoft\Windows\INetCache (F-0)
C:\WINDOWS\ServiceProfiles\NetworkService\AppData\Local\Temp (F-1)
C:\WINDOWS\ServiceState\WinHttpAutoProxySvc\Data (F-0)
C:\WINDOWS\System32\config\systemprofile\AppData\Local (D-0)
C:\WINDOWS\System32\config\systemprofile\AppData\Local\D3DSCache (D-0)
C:\WINDOWS\System32\config\systemprofile\AppData\Local\NVIDIA\DxCache (F-5)
C:\WINDOWS\SystemTemp (D-11)
C:\WINDOWS\SystemTemp (F-3)
C:\WINDOWS\Temp (F-42)

# Paquetes:

Clipchamp.Clipchamp_4.5.10620.0_x64__yxz26nhyzhsrt
Microsoft.Advertising.Xaml_10.1808.3.0_x64__8wekyb3d8bbwe
Microsoft.BingNews_4.55.62231.0_x64__8wekyb3d8bbwe
Microsoft.BingSearch_1.1.40.0_x64__8wekyb3d8bbwe
Microsoft.BingWeather_4.54.63040.0_x64__8wekyb3d8bbwe
Microsoft.Edge.GameAssist_1.0.4019.0_x64__8wekyb3d8bbwe
MicrosoftWindows.Client.WebExperience_526.15201.50.0_x64__cw5n1h2txyewy

# Misceláneo:

[!] Service Error: (06/26/2026 08:07:13) - El servicio Servicio Bonjour se terminó de manera inesperada. Esto ha sucedido 1 veces.
[!] Service Error: (06/26/2026 08:07:13) - El servicio DTS APO3 Service se terminó de manera inesperada. Esto ha sucedido 1 veces.
[!] Service Error: (06/26/2026 08:07:12) - El servicio ASUS Certificate Service se terminó de manera inesperada. Esto ha sucedido 1 veces.
[!] Service Error: (06/26/2026 08:07:12) - El servicio Adobe Acrobat Update Service se terminó de manera inesperada. Esto ha sucedido 1 veces.
[!] Service Error: (06/26/2026 08:07:12) - El servicio AdobeUpdateService se terminó de manera inesperada. Esto ha sucedido 1 veces.
[!] Service Error: (06/26/2026 08:04:32) - El servicio Servicio de Google Update (gupdate) no pudo iniciarse debido al siguiente error: El servicio no respondió a tiempo a la solicitud de inicio o de control.
[!] Service Error: (06/26/2026 08:02:35) - El servicio Daemon Update Assistant Service se terminó de manera inesperada. Esto ha sucedido 1 veces.
[!] Service Error: (06/26/2026 07:54:26) - El servicio Daemon Update Assistant Service se terminó de manera inesperada. Esto ha sucedido 31 veces.
[!] Service Error: (06/26/2026 07:44:26) - El servicio Daemon Update Assistant Service se terminó de manera inesperada. Esto ha sucedido 30 veces.
[!] Service Error: (06/25/2026 19:32:08) - El servicio Daemon Update Assistant Service se terminó de manera inesperada. Esto ha sucedido 29 veces.
Date: 06/26/2026 08:04  Boot Time was: 58.6 s (58641 ms)
Date: 06/24/2026 20:27  Boot Time was: 34.8 s (34815 ms)
Date: 06/24/2026 11:37  Boot Time was: 107.5 s (107463 ms)
[08:07:30]: __FilterToConsumerBinding | Name:
  -> [INFO] Status: No encontrado
[?] AntiVirus Software: Windows Defender
[?] Se borraron los registros del Visor de eventos

C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.26040.7-0
C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.26050.15-0
C:\Program Files\Google\Chrome\Application\149.0.7827.115
C:\Program Files (x86)\Microsoft\Edge\Application\149.0.4022.80

HKLM\Software\Microsoft\Windows Defender\Exclusions\Extensions

HKLM\Software\Microsoft\Windows Defender\Exclusions\IpAddresses

HKLM\Software\Microsoft\Windows Defender\Exclusions\Paths
    C:\Perform    REG_DWORD    0x0
    C:\Users\Usuario    REG_DWORD    0x0
    C:    REG_DWORD    0x0
    C:\ProgramData    REG_DWORD    0x0

HKLM\Software\Microsoft\Windows Defender\Exclusions\Processes

HKLM\Software\Microsoft\Windows Defender\Exclusions\TemporaryPaths

___

C:\Users\Usuario\AppData\Local\CrashDumps\Malwarebytes\Malwarebytes.exe.18264.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.19820.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.19924.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.23432.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.24168.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.24464.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.24608.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.24948.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.26172.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.3936.dmp
C:\WINDOWS\System32\config\systemprofile\AppData\Local\CrashDumps\DaemonUpdateAssistantService.exe.5712.dmp


___________________________ EOF DNB __________________________

 capturada7100%75%50%
 IMPORTANTE:
 QUE SU ORDENADOR NO SE PONGA EN ESTADO DE SUSPENSIÓN DURANTE TODO EL PROCESO DE ANALISIS QUE SE LE VAN A REALIZAR CON LOS DIFERENTES PROGRAMAS QUE SE LE INDIQUEN EN ESTE TEMA, ES DECIR, QUE SU ORDENADOR NO SE APAGUE LA PANTALLA YA QUE PODRÍA INTERFERIR EN EL PROCESO DE ANALISIS Y NO ELIMINARSE CORRECTAMENTE LAS INFECCIONES Y VIRUS QUE ENCUENTRE.
 SIGA SU MANUAL QUE SE LE DEJA JUNTO AL PROGRAMA EN ESTE TEMA.
 SI DICHO PROGRAMA LE PIDE REINICIAR! PROCEDES! PERO SÓLO SI SE LO SOLICITA DICHO PROGRAMA.
 Descarga, Instala, y ejecuta: Dr.Web Cureit!. Aquí te dejo la Url de Descarga del: Dr.Web Cureit!, para que sepa cómo instalarlo y descargarlo correctamente:


 (Pantalla Anterior)
 Aparecerá la siguiente pantalla similar y ´´MARQUE´´ y ´´HABILITE´´ ´´TODAS LAS OPCIONES´´ Y PESTAÑAS ´´QUE LE APAREZCAN A USTED´´ y deslícese con el Ratón (Mouse) hacia abajo:

 Quedará de la siguiente forma similar:

 En esa misma pantalla en la que se encuentra usted, (Pantalla Anterior), Busque y Un Clic en la pestaña que pone:

 Aparecerá de la siguiente forma similar:

 En esa misma pantalla en la que se encuentra usted, (Pantalla Anterior), Busque** y Un Clic en la pestaña que aparece:


 (Pantalla Anterior)


 (Pantalla Anterior)
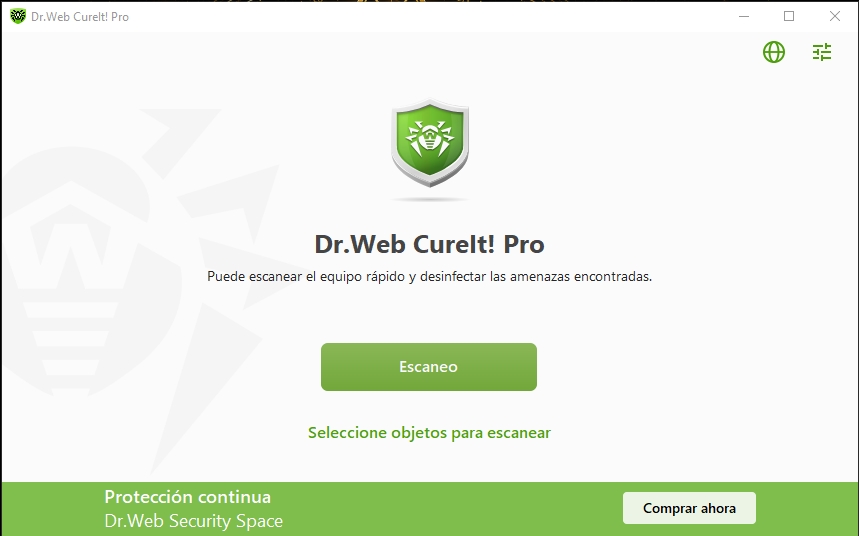
 (Pantalla Anterior)
 Cuando finalice el proceso completo de análisis el programa: Dr.Web Cureit!, aparecerá una pantalla similar a la que se muestra a continuación:

 Un Clic en la siguiente pestaña:
 de la lista de opciones que ofrece el programa: Dr.Web Cureit! Un Clic en la opción que pone: Eliminar ó Delete en: ´´TODOS´´ los recuadros que le aparezcan a usted en dicho programa. Si usted no está seguro de la acción a tomar me lo comunica usted por aquí! y aparecerá una pantalla similar a esta:
 o algo parecido tal como se indica en el apartado anterior.
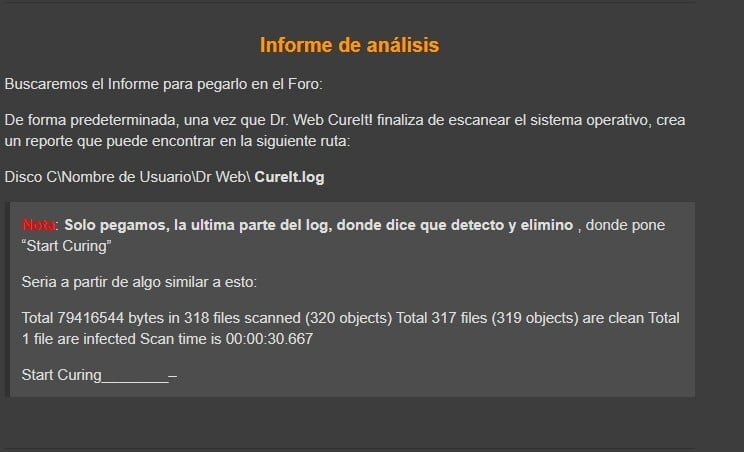


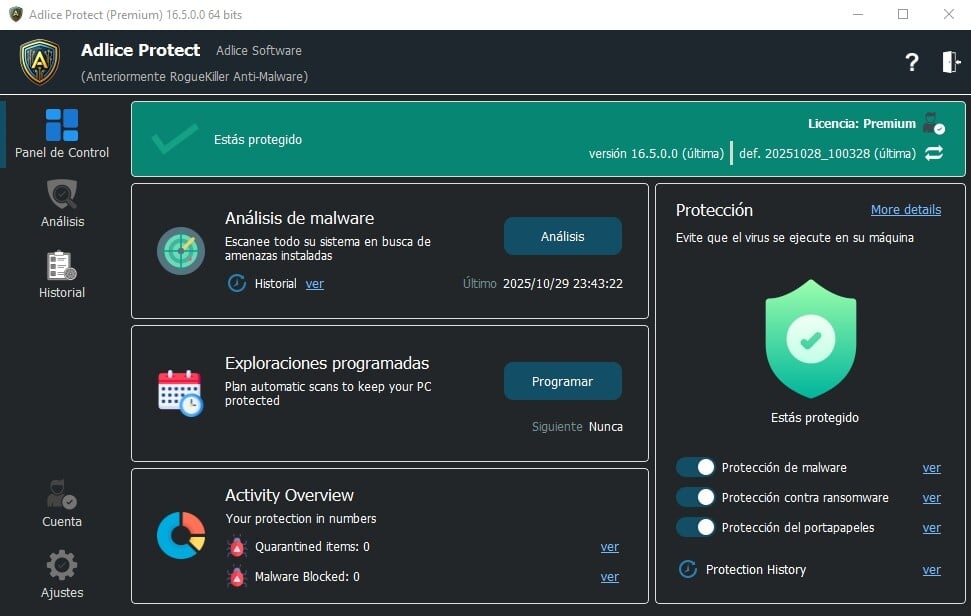
 tal como aparece en la pantalla anterior.
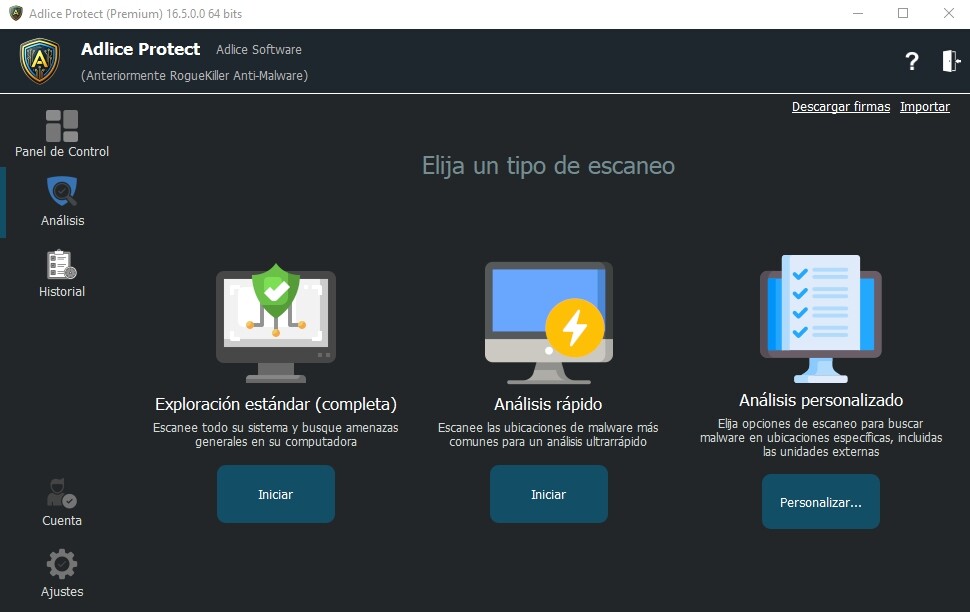
 (Tal como se muestra en la pantalla anterior)